

GSocket Linux Backdoor Surges, Threat Actors Weaponize Legitimate Remote Access Tool
November 12, 2026 Threat actors are weaponizing GSocket, a legitimate open-source remote access tool, to maintain persistent access to Linux servers even after defenders patch the vulnerabilities used for initial entry. Microsoft Defender for Endpoint…
Microsoft Outlook Zero-Day Steals NTLMv2 Hashes via One Click
November 12, 2026 Microsoft has patched CVE-2026-124194, an actively exploited zero-day vulnerability in Microsoft Outlook that silently exposes NTLMv2 authentication hashes to remote attackers. Also added to CISA’s Known Exploited Vulnerabilities…
AntiFox AI Pentesting Platform Targets AWS Production Secrets in Active Cloud Intrusions
November 11, 2026 Cybersecurity researchers at Arctic Wolf Labs have uncovered an active campaign where attackers abuse AntiFox, an open-source AI-driven penetration testing platform, to steal Amazon Web Services (AWS) credentials and access production…
CISA Adds Cisco BroadWorks XXE CVE to KEV Catalog
November 11, 2026 CISA added CVE-2026-20320 to its Known Exploited Vulnerabilities Catalog on November 10, 2026. This high-severity flaw in Cisco BroadWorks lets unauthenticated remote attackers read sensitive configuration data via a crafted XML…
Nitori Data Breach Exposes 37.6 Million Customer Records
November 11, 2026 Nitori Holdings, Japan’s largest furniture and home accessories retailer, disclosed a massive data breach that may have exposed up to 37.62 million customer records. The incident ranks among the largest retail data breaches of…
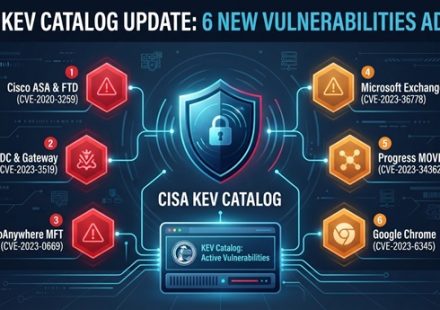
CISA Adds Six Actively Exploited Flaws to KEV Catalog
November 11, 2026 CISA has added six actively exploited vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog. The additions span Microsoft Outlook, Google Chrome, Barracuda Email Security Gateway, Cisco BroadWorks, and Openwave Webtop.…
SAP Patches Four CVSS 10.0 Flaws
November 10, 2026 SAP released critical security updates on November 10, 2026, patching four maximum-severity vulnerabilities rated CVSS 10.0. These flaws affect SAP NetWeaver, SAP Web Dispatcher, SAP Gateway, and the SAML2 service provider. Attackers…
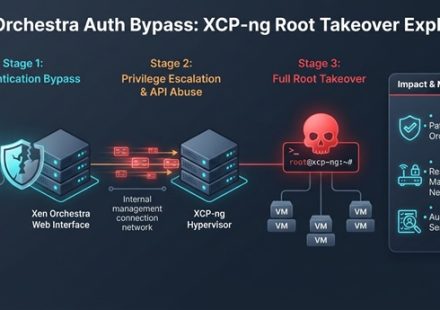
Critical Xen Orchestra Authentication Bypass Enables XCP-ng Root Takeover
November 10, 2026 Cybersecurity researchers disclosed a critical authentication bypass vulnerability in Xen Orchestra today. The flaw is being actively exploited in attacks that grant administrator privileges and allow full takeover of XCP-ng…
Google Chrome CVE Eighth Actively Exploited Zero-Day of 2026 Patched
November 10, 2026 Google has patched a high-severity use-after-free vulnerability in Chrome that attackers are actively exploiting in the wild. The flaw, tracked as CVE-2026-125350, marks the eighth actively exploited zero-day in Chrome this year.…
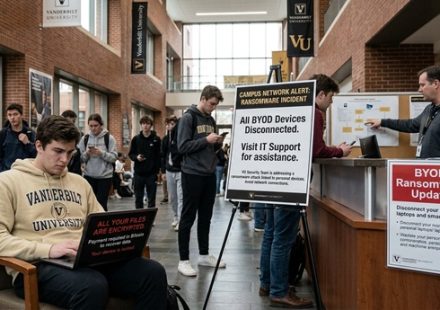
BYOD Ransomware Gang Encrypts Vanderbilt University
November 9, 2026 Vanderbilt University confirmed an active cybersecurity incident on Monday after the BYOD ransomware gang claimed responsibility for encrypting databases and stealing sensitive student, employee, and research data. The attackers allege…