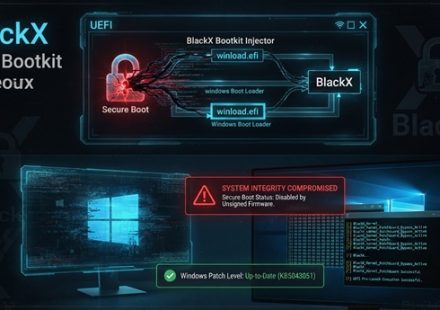
BlackX UEFI Bootkit Exploits Baton Drop Flaw to Bypass Secure Boot on Patched Windows Systems

October 24, 2026 A new UEFI bootkit named BlackX is actively bypassing Secure Boot on fully patched Windows systems. Kaspersky researchers attribute the espionage campaign to APT41 and warn that the bootkit exploits a now-patched vulnerability that…
Armory Castle Exploits Remote Support Zero-Day Since August
BeyondTrust patched a critical authentication bypass zero-day in Remote Support after Mandiant confirmed China-nexus actor Armory Castle exploited it since late August, deploying new SAWFLY and BARECLAW malware.
Meta Muse AI Assistant Creates macOS Backdoor Vulnerability
September 22, 2026 Security researcher Patrick Wardle has disclosed a serious vulnerability in Meta’s new Muse AI assistant for macOS. The flaw lets malware already on a Mac quietly hijack Muse and abuse the broad permissions its owner granted the…
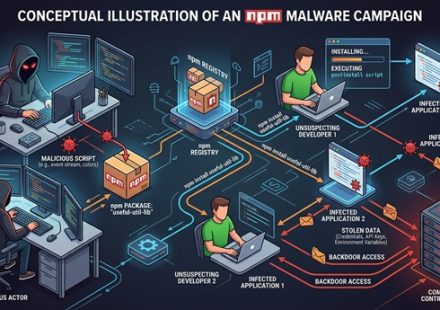
Malicious npm Packages Evade Install-Script Defenses
September 20, 2026 Threat actors have published a malicious npm package named indexed-btree that evades GitHub’s latest install-script defenses by hiding its payload inside normal runtime behavior. The package has already accumulated more than 2…
Iranian Hackers Deploy CHOSEN BRICK Malware
September 16, 2026 Government agencies in the United States, United Kingdom, and the Netherlands have issued a joint warning about an Iranian state-linked espionage campaign that deploys a Windows malware strain named CHOSEN BRICK. The malware targets…
Socket Uncovers 19 Malicious Chrome and Edge Extensions Stealing Crypto Wallets and Credentials
August 30, 2026 Socket researchers have uncovered a sprawling malware campaign hidden inside 19 browser extensions for Google Chrome and Microsoft Edge. Furthermore, the malicious framework steals cryptocurrency wallet secrets, harvests credentials, and…
ATF Confirms Major Cybersecurity Incident After Qilin Ransomware Breach Claim
August 27, 2026 The Bureau of Alcohol, Tobacco, Firearms and Explosives (ATF) confirmed a major cybersecurity incident on August 26, 2026, after the Qilin ransomware gang listed the U.S. federal law enforcement agency on its dark web data leak portal.…
ToxicPanda 2.0 Android Malware Abuses VPN and Wireless ADB
August 23, 2026 A critical vulnerability in the Elementor Pro WordPress plugin allows unauthenticated attackers to upload executable PHP files for remote code execution on affected servers. Furthermore, the flaw has been actively disclosed and patched,…
MoYu Group Deploys Proxy Botnet Malware on Android Car Head Units via DoFun Update App
August 22, 2026 Kaspersky researchers have uncovered a supply-chain attack targeting Android-based car head units that uses a legitimate device-update app to spread proxy botnet malware. The operation, attributed to the MoYu threat actor group, marks the…
Sable Squirrel Spends Million on Expired Domains for Malware
August 16, 2026 A threat actor tracked as Sable Squirrel has spent nearly $7 million acquiring expired domains to build a sprawling criminal enterprise. Consequently, the group operates illegal sports streaming platforms, online gambling promotions, and…