Apache Roller CVE Actively Exploited RCE Flaw in Blogging Server

November 19, 2026 Apache Roller CVE-2026-129448 is a critical unauthenticated remote code execution flaw in the Apache Roller group-blogging server, and the Apache Software Foundation has confirmed that the flaw is being actively exploited in the wild.…
CISA Confirms Active Exploitation in Synology NAS Ransomware Attacks
November 19, 2026 Synology NAS devices are under active attack after the U.S. Cybersecurity and Infrastructure Security Agency (CISA) added CVE-2024-10441 to its Known Exploited Vulnerabilities catalog. The Synology DiskStation Manager remote code…
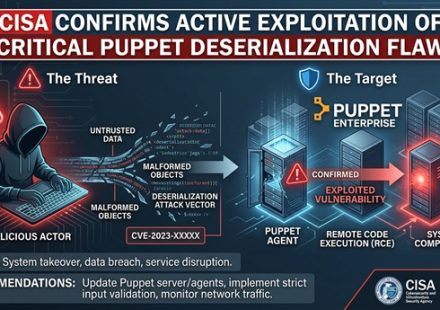
CISA Confirms Active Exploitation of Critical Puppet Deserialization Flaw
November 19, 2026 CISA added CVE-2026-115731 to its Known Exploited Vulnerabilities catalog on November 17, 2026, confirming active exploitation of a critical deserialization flaw in Perforce Puppet Enterprise. The vulnerability carries a CVSS 4.0 score…
NGINX HTTP/2 Flaw Enables Unauthenticated RCE
November 18, 2026 CVE-2026-123007, a decade-old memory corruption flaw in NGINX HTTP/2 flow control, allows unauthenticated attackers to run code on any server with HTTP/2 enabled. F5 and the NGINX project released fixed builds today, and researchers…
FreeSWITCH Critical RCE Actively Exploited
November 18, 2026 A critical remote code execution vulnerability in SignalWire FreeSWITCH, tracked as CVE-2026-116779, is being actively exploited in the wild. The flaw lets a remote attacker run arbitrary operating system commands with the privileges of…
Java4Shell Critical Pre-Auth RCE in Jira, Jenkins, and Keycloak
November 18, 2026 Security researchers have disclosed a critical pre-authentication remote code execution flaw in OpenJDK called Java4Shell (CVE-2026-114938). The vulnerability affects Jira, Jenkins, Keycloak, and other widely deployed Java applications.…
Apache Axis RCE Exploited in Confluence Data Center
November 17, 2026 The CVE-2026-90436 Apache Axis remote code execution flaw is now being actively exploited against Atlassian Confluence Data Center and N-able N-central servers. Rapid7 detected real intrusions on November 13, 2026, and the attackers…
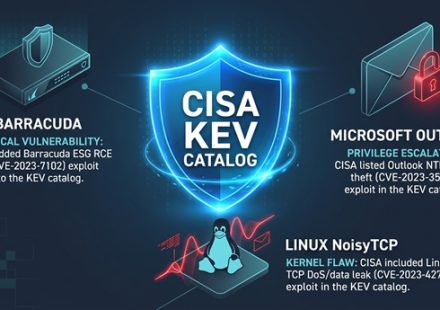
CISA Adds Barracuda, Outlook, and Linux NoisyTCP Flaws to KEV Catalog
November 16, 2026 An 11-year-old Linux kernel vulnerability, dubbed NoisyTCP, affects almost all Linux distributions and lets attackers crash systems running Nginx, Apache, and SSH servers with default configurations. Furthermore, the U.S. Cybersecurity…
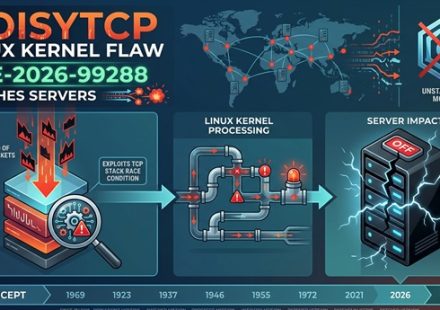
NoisyTCP Linux Kernel Flaw CVE Crashes Servers
November 16, 2026 The NoisyTCP vulnerability (CVE-2026-99288) is an 11-year-old Linux kernel flaw that lets unauthenticated attackers crash nearly every Linux server running Nginx, Apache, or SSH with default settings. Security researcher Hyunwoo Kim…
Mior and Skyfall Attacks Break AMD SEV-SNP Confidentiality
November 15, 2026 The Mior and Skyfall attacks disclosed this week break the confidentiality guarantees of AMD SEV-SNP, the confidential computing platform used to protect virtual machines from malicious cloud hosts. Two ETH Zurich research teams showed…