SAP Patches Four CVSS 10.0 Flaws

November 10, 2026 SAP released critical security updates on November 10, 2026, patching four maximum-severity vulnerabilities rated CVSS 10.0. These flaws affect SAP NetWeaver, SAP Web Dispatcher, SAP Gateway, and the SAML2 service provider. Attackers…
Google Chrome CVE Eighth Actively Exploited Zero-Day of 2026 Patched
November 10, 2026 Google has patched a high-severity use-after-free vulnerability in Chrome that attackers are actively exploiting in the wild. The flaw, tracked as CVE-2026-125350, marks the eighth actively exploited zero-day in Chrome this year.…
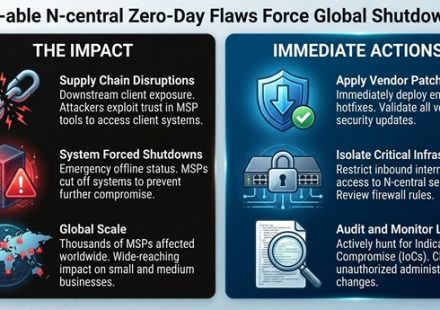
N-able N-central 30+ Zero-Day Flaws Force Global Platform Shutdown | November 2026
November 9, 2026 N-able has taken its hosted N-central environments offline worldwide after a security researcher disclosed more than 30 alleged zero-day vulnerabilities in the remote monitoring and management platform. Furthermore, the most severe…
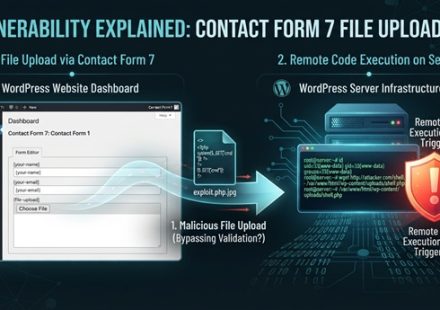
Contact Form 7 Unauthenticated File Upload Enables RCE on WordPress Sites
November 9, 2026 A critical unauthenticated file upload vulnerability has been disclosed in Contact Form 7, one of the most widely used WordPress plugins with more than 10 million active installations. Tracked as CVE-2026-114432 and scored CVSS 3.1 9.8…
CISA Adds Apple CVE to KEV, APT29 Actively Exploiting
November 8, 2026 CISA added CVE-2024-27834 to its Known Exploited Vulnerabilities catalog on November 4, 2026. Attackers linked to Russia’s APT29 group are actively exploiting this Apple Pointer Authentication bypass to deliver information-stealing…
D-Link DGS-3130 Zero-Day Flaws Expose Enterprise Switch Configurations and Credentials
November 8, 2026 D-Link disclosed multiple unpatched zero-day vulnerabilities in its DGS-3130 series managed Gigabit stackable switches on November 6, 2026. The flaws affect the D-Link Discovery Protocol (DDP) and portions of the switch firmware security…
Microsoft Paint RCE CVE Store-Only Fix Leaves Windows Systems Vulnerable
November 8, 2026 Microsoft has patched a remote code execution flaw in Windows Paint, but the fix arrives only through the Microsoft Store. CVE-2026-83844 leaves systems vulnerable unless administrators verify that every user copy of Paint has updated.…
SonicWall SSL-VPN MFA Bypass CVE, CISA Confirms Active Exploitation
November 7, 2026 SonicWall has patched a critical SSL-VPN authentication bypass vulnerability that allows attackers to circumvent multi-factor authentication controls on affected firewalls. The flaw, tracked as CVE-2026-19868, carries a CVSS score of 7.1…
OpenSSH SSHole Authentication Bypass Actively Exploited Within Hours
November 6, 2026 Threat actors began exploiting a critical OpenSSH authentication bypass vulnerability within hours of its disclosure on November 5, 2026. The flaw, tracked as CVE-2026-123158 and nicknamed SSHole, lets unauthenticated attackers log into…
Zyxel GS1900 Patch Fails to Block Zero-Day
November 5, 2026 Zyxel GS1900 network switches that received the vendor’s earlier patch for an actively exploited flaw are still vulnerable to the same attack chain. Binarly researchers discovered that Patch 2 firmware fails to block the exploit,…