Hackers Scan for Critical Oracle EBS RCE Flaw Days After Patch

October 29, 2026 Threat actors have started scanning for a newly patched critical vulnerability in Oracle E-Business Suite (EBS) within days of its disclosure. Tracked as CVE-2026-101767, this unauthenticated SQL injection flaw carries a CVSS score of…
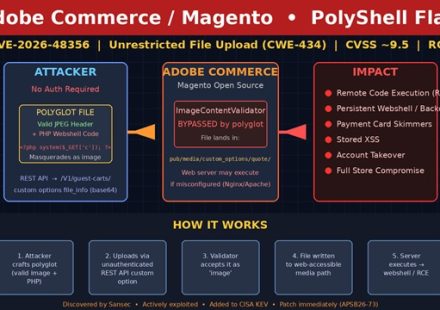
CISA Adds Adobe Commerce PolyShell Flaw to KEV
October 28, 2026 The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a critical Adobe Commerce and Magento vulnerability to its Known Exploited Vulnerabilities (KEV) catalog on October 27, 2026. Tracked as CVE-2026-48356 and dubbed…
CISA Adds Brotli2Shell to KEV Catalog Enables RCE Across Node.js, .NET, and Python
October 28, 2026 CISA has added CVE-2026-111497 to its Known Exploited Vulnerabilities catalog after confirmed in-the-wild exploitation. The flaw, also known as Brotli2Shell, Node2Shell, and HTTP2Shell, is an out-of-bounds write in Google’s Brotli…
CISA Confirms PHP2Shell RCE Exploitation Added to KEV Catalog
October 27, 2026 CISA confirmed active exploitation of two critical PHP vulnerabilities collectively tracked as PHP2Shell. Threat actors can exploit CVE-2026-109618 and CVE-2026-109619 to gain unauthenticated remote code execution on millions of…
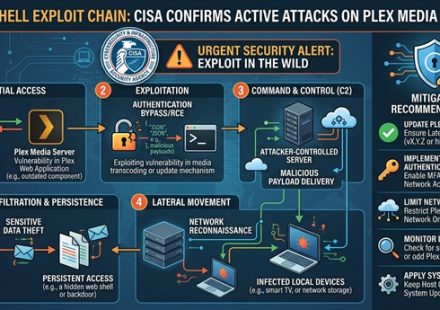
Plex2Shell Exploit Chain: CISA Confirms Active Attacks on Plex Media Server
October 26, 2026 CISA has added four Plex Media Server vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog after confirming active exploitation in the wild. The flaws, collectively tracked as Plex2Shell, allow remote attackers to achieve…
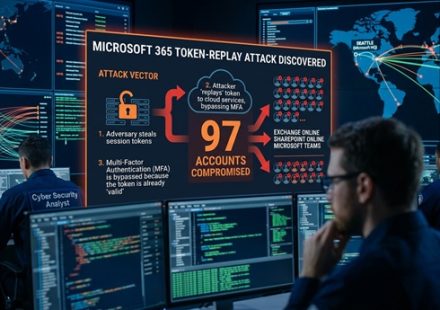
Microsoft 365 Token-Replay Attacks Compromise 97 Accounts at 79 Organizations
October 26, 2026 Huntress researchers have disclosed a widespread Microsoft 365 campaign that leveraged adversary-in-the-middle (AitM) relays to steal and replay session tokens. Consequently, attackers compromised 97 accounts across 79 organizations…
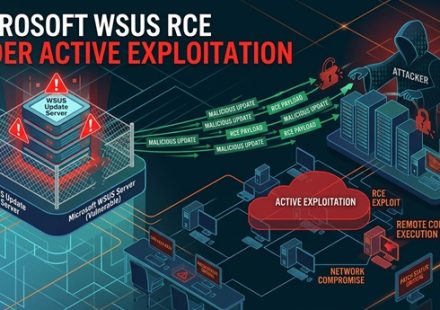
Windows Server WSUS Critical RCE Under Active Exploitation
October 25, 2026 On October 14, 2025, Microsoft disclosed a critical remote code execution (RCE) vulnerability in the Windows Server Update Service (WSUS). Tracked as CVE-2025-59287, this flaw allows unauthenticated attackers to execute code with SYSTEM…
k0t Threat Actor Breaches Enterprise Firewalls and VPNs
October 25, 2026 Cybersecurity researchers from Group-IB and NyxLab have uncovered a massive campaign that has breached enterprise firewalls and VPNs worldwide. Consequently, the threat actor known as k0t has exposed over 70,000 credentials and…
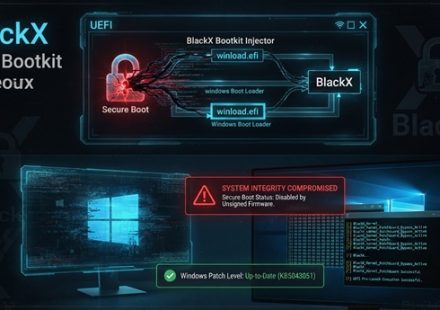
BlackX UEFI Bootkit Exploits Baton Drop Flaw to Bypass Secure Boot on Patched Windows Systems
October 24, 2026 A new UEFI bootkit named BlackX is actively bypassing Secure Boot on fully patched Windows systems. Kaspersky researchers attribute the espionage campaign to APT41 and warn that the bootkit exploits a now-patched vulnerability that…
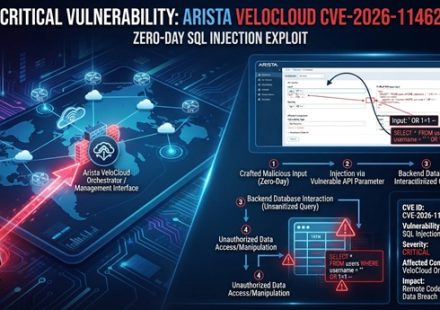
Arista VeloCloud Orchestrator SQL Injection Zero-Day Grants Operator Privileges
October 22, 2026 Arista Networks disclosed a critical zero-day vulnerability in VeloCloud Orchestrator on October 22, 2026. CVE-2026-114625 lets any authenticated user escalate to operator privileges through SQL injection. Attackers are actively…