Ivanti Connect Secure Zero-Day Chain Grants Root to Attackers

October 13, 2026 Ivanti disclosed an actively exploited zero-day vulnerability chain in Connect Secure (ICS) VPN appliances on October 13, 2026. Tracked as CVE-2026-104935, the flaw combines an authentication bypass and remote code execution to let…
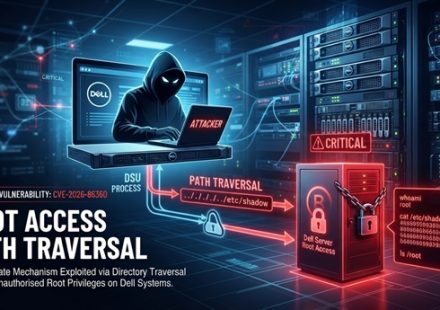
Dell System Update Path Traversal Grants Root to Unauthenticated Attackers
October 11, 2026 Dell disclosed a critical path traversal vulnerability in its System Update (DSU) command-line tool that allows unauthenticated remote attackers to execute arbitrary code with root privileges. The flaw, tracked as CVE-2026-86360, carries…
Rejetto HFS Authentication Bypass Under Active Exploitation
October 11, 2026 Threat actors are actively exploiting a critical authentication bypass in Rejetto HTTP File Server (HFS) that enables full administrative access and remote code execution. The vulnerability, tracked as CVE-2026-61500 (CVSS score: 9.3),…
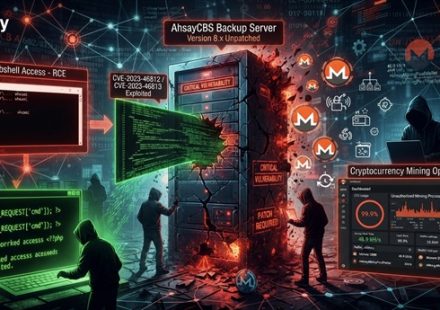
Unpatched AhsayCBS Flaws Exploited to Deploy Webshells and Mine Crypto
October 10, 2026 Threat actors are actively exploiting two unpatched vulnerabilities in the AhsayCBS backup management platform to deploy webshells and cryptocurrency miners on victim systems. The flaws, tracked as CVE-2026-105133 and CVE-2026-105134,…
FBI Seizes Flax Typhoon Hacking Tools Used to Breach Critical Infrastructure
October 9, 2026 The FBI has seized seven domains used by Chinese state-sponsored hackers known as Flax Typhoon to operate two hacking platforms, MicroScan and FishHub. These tools were used in attacks that breached critical infrastructure and other…
Cisco Critical NX-OS Flaws Enable Nexus Switch Takeover
October 8, 2026 Cisco disclosed five critical vulnerabilities in its NX-OS data center network operating system on October 7, 2026. These flaws affect Nexus 3000 and Nexus 9000 Series switches and could allow remote attackers to execute arbitrary code…
Critical Unpatched LMCache RCE Threatens LLM Inference Infrastructure
October 7, 2026 A critical, unpatched vulnerability in LMCache allows unauthenticated attackers to execute remote code on the LLM inference cache layer. The flaw, tracked as CVE-2026-105192, carries a CVSS score of 9.8 and remains unpatched as of this…
Microsoft Exchange Flaw Lets Authenticated Attackers Read Other Users Mailboxes
October 7, 2026 Microsoft has released out-of-band security updates for a high-severity vulnerability in Exchange Server. The flaw, tracked as CVE-2026-96940, allows authenticated attackers to read other users’ mailboxes within the same…
Critical Atlassian CVE Allows Unauthenticated File Access in 8 Data Center Products
October 6, 2026 A critical path traversal vulnerability in eight Atlassian Data Center products allows unauthenticated attackers to read sensitive files from the web application root directory. Atlassian disclosed CVE-2026-21589 on October 5, 2026, and…
Citrix NetScaler CVE SAML Zero-Day Under Active Exploitation
October 5, 2026 Citrix has released emergency security updates for a new NetScaler vulnerability tracked as CVE-2026-88779. The flaw is a memory buffer weakness affecting NetScaler ADC and NetScaler Gateway appliances that use SAML authentication.…