NGINX HTTP/2 Flaw Enables Unauthenticated RCE

November 18, 2026 CVE-2026-123007, a decade-old memory corruption flaw in NGINX HTTP/2 flow control, allows unauthenticated attackers to run code on any server with HTTP/2 enabled. F5 and the NGINX project released fixed builds today, and researchers…
FreeSWITCH Critical RCE Actively Exploited
November 18, 2026 A critical remote code execution vulnerability in SignalWire FreeSWITCH, tracked as CVE-2026-116779, is being actively exploited in the wild. The flaw lets a remote attacker run arbitrary operating system commands with the privileges of…
Apache Axis RCE Exploited in Confluence Data Center
November 17, 2026 The CVE-2026-90436 Apache Axis remote code execution flaw is now being actively exploited against Atlassian Confluence Data Center and N-able N-central servers. Rapid7 detected real intrusions on November 13, 2026, and the attackers…
GPUStack CVE Critical Authentication Bypass Enables Unauthenticated Admin Takeover
November 12, 2026 GPUStack CVE-2026-102895 is a critical authentication bypass vulnerability. It enables unauthenticated attackers to gain full administrative access to GPUStack deployments. Furthermore, active exploitation has been confirmed in the…
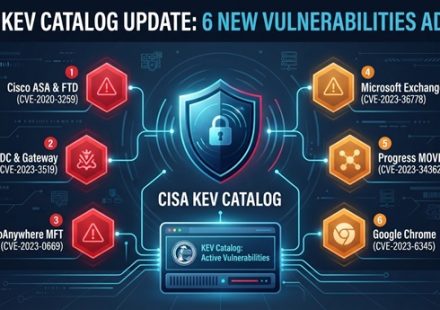
CISA Adds Six Actively Exploited Flaws to KEV Catalog
November 11, 2026 CISA has added six actively exploited vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog. The additions span Microsoft Outlook, Google Chrome, Barracuda Email Security Gateway, Cisco BroadWorks, and Openwave Webtop.…
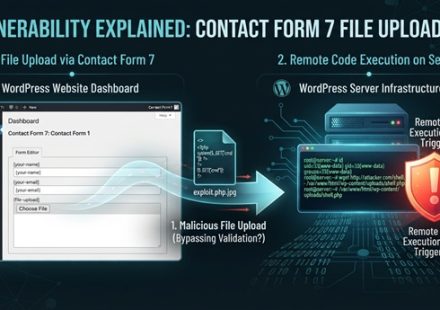
Contact Form 7 Unauthenticated File Upload Enables RCE on WordPress Sites
November 9, 2026 A critical unauthenticated file upload vulnerability has been disclosed in Contact Form 7, one of the most widely used WordPress plugins with more than 10 million active installations. Tracked as CVE-2026-114432 and scored CVSS 3.1 9.8…
CISA Confirms Active Exploitation of WordPress Core RCE Flaw CVE-2026-119977
November 04, 2026 The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has confirmed active exploitation of a high-severity remote code execution flaw in WordPress Core. CVE-2026-119977 stems from a Time-of-check Time-of-use (TOCTOU) race…
Siemens IoT2050 Node-RED Flaw Under Active Exploitation
November 4, 2026 A maximum-severity authentication flaw in Siemens SIMATIC IoT2050 Advanced devices is being actively exploited in the wild. Attackers are abusing CVE-2026-58115 to deploy Linux bot payloads and persistent command backdoors on unprotected…
Windows Server WSUS Critical RCE Under Active Exploitation
October 25, 2026 On October 14, 2025, Microsoft disclosed a critical remote code execution (RCE) vulnerability in the Windows Server Update Service (WSUS). Tracked as CVE-2025-59287, this flaw allows unauthenticated attackers to execute code with SYSTEM…
Critical RCE Flaws in PHP Runtime Put 75% of Websites at Risk
October 21, 2026 The PHP security team shipped emergency patches for two critical remote code execution flaws tracked collectively as PHP2Shell. These vulnerabilities sit in the PHP runtime itself, which means every website running a vulnerable version…