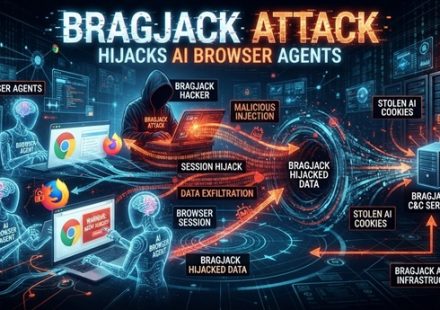
BragJack Attack Hijacks AI Browser Agents

September 19, 2026 Security researcher Gal Weizman of Forever Security has disclosed BragJack, a new attack technique that hijacks AI browser agents through malicious extensions. The proof-of-concept works against five major Chromium-based browsers and…
Check Point Root RCE via Management Server Login Flaw
September 18, 2026 Check Point Software has disclosed a critical vulnerability that lets unauthenticated attackers execute code with root privileges on Security Management Server and Log Server systems. The flaw, tracked as CVE-2026-91843, stems from a…
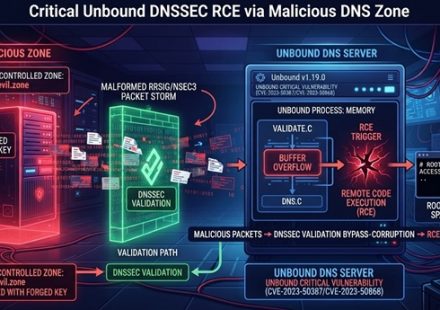
Critical Unbound DNSSEC Validator RCE via Malicious DNS Zone
September 18, 2026 A critical heap overflow vulnerability in the Unbound DNS resolver enables remote code execution through malicious DNS zones. The flaw, tracked as CVE-2026-81642, affects every Unbound release before version 1.26.1 and carries a CVSS…
Ransomware Gangs Exploit Critical VMware vCenter RCE CVE
September 16, 2026 Ransomware gangs have joined attacks exploiting a critical VMware vCenter remote code execution flaw. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) updated its Known Exploited Vulnerabilities catalog to flag…
Google Patches Actively Exploited Android Zero-Day on Pixel Devices
September 16, 2026 Google has released the September 2026 security patches for Pixel devices. This update fixes 110 vulnerabilities, including one zero-day flaw that is actively exploited in targeted attacks. The zero-day, tracked as CVE-2026-58704, is a…
Cisco Secure Email Gateway CVE Critical Zero-Day
September 15, 2026 Cisco has disclosed a critical zero-day vulnerability in its Secure Email Gateway that threat actors are actively exploiting to gain root-level command execution. The flaw, tracked as CVE-2026-76461, carries a CVSS score of 9.8 and was…
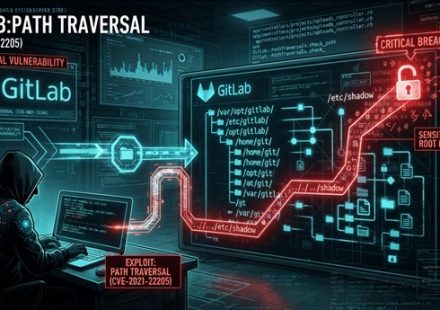
CISA Confirms Active Exploitation of Critical GitLab Path Traversal
September 14, 2026 CISA has added CVE-2026-85706 to its Known Exploited Vulnerabilities catalog after confirming active exploitation in the wild. This maximum-severity path traversal flaw affects GitLab Community Edition and Enterprise Edition.…
UNC3569 Exploits Sogou Input Method Flaw to Deploy GRAYRABBIT Backdoor
September 13, 2026 Threat actors linked to a China-aligned espionage group are exploiting a critical vulnerability (CVE-2026-51990) in Tencent’s Sogou Input Method for Windows to deploy the GrayRabbit backdoor. The flaw allows one-click remote code…
Critical Path Traversal Flaw Under Active Exploitation
September 11, 2026 On September 10, 2026, GitLab disclosed CVE-2026-85706, a maximum-severity path traversal vulnerability in its repository commits API. The flaw carries a CVSS score of 10.0 and allows unauthenticated attackers to read arbitrary files…
Cisco Critical FMC Authentication Bypass Confirmed Under Active Exploitation
September 10, 2026 Cisco has confirmed that a maximum-severity authentication bypass vulnerability tracked as CVE-2026-20079 in its Secure Firewall Management Center (FMC) software is being actively exploited in attacks. Furthermore, the U.S.…