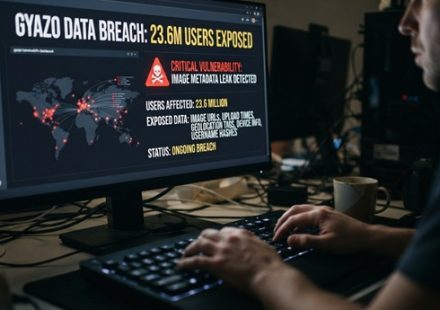
Gyazo Data Breach Exposes 23.6 Million Users

September 19, 2026 The Gyazo image-sharing platform has confirmed a massive data breach after attackers exploited a server vulnerability. Consequently, approximately 23.6 million user records and 490 million image metadata entries were exposed. The…
Iranian Hackers Deploy CHOSEN BRICK Malware
September 16, 2026 Government agencies in the United States, United Kingdom, and the Netherlands have issued a joint warning about an Iranian state-linked espionage campaign that deploys a Windows malware strain named CHOSEN BRICK. The malware targets…
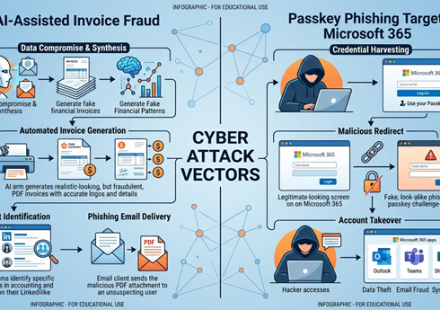
Microsoft Discloses AI-Assisted Invoice Fraud and Passkey Phishing Campaigns
Microsoft has disclosed details of two active campaigns targeting enterprise cloud environments through AI-assisted executive impersonation and passkey-themed social engineering. The attacks leverage third-party email delivery infrastructure to bypass…
Passkey-Themed Phishing Attacks Target Microsoft 365
September 11, 2026 Microsoft has confirmed that threat actors linked to the ShinyHunters and Helix extortion gangs are conducting sophisticated passkey-themed phishing campaigns that compromise corporate Microsoft 365 accounts and steal sensitive data.…
Cronos Tectonic Exploit Drained 4 Million in 20 Minutes
September 1, 2026 Cronos blockchain halted all transactions on August 30, 2026, after a threat actor exploited the Tectonic lending platform in a $74 million price-manipulation attack. The attacker artificially inflated the price of Tectonic’s…
Fire Ant Espionage Campaign Hijacks Cisco Routers
August 31, 2026 A China-nexus cyber espionage actor tracked as Fire Ant has evolved beyond hypervisor compromise to hijack Cisco IOS XR routers, TACACS authentication servers, and Linux management hosts. Consequently, the group turns trusted network…
Socket Uncovers 19 Malicious Chrome and Edge Extensions Stealing Crypto Wallets and Credentials
August 30, 2026 Socket researchers have uncovered a sprawling malware campaign hidden inside 19 browser extensions for Google Chrome and Microsoft Edge. Furthermore, the malicious framework steals cryptocurrency wallet secrets, harvests credentials, and…
CISA Imposes 3-Day Patch Mandate on Perfect-10 Oracle WebLogic Proxy Flaw
August 28, 2026 The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has imposed its tightest emergency patch mandate on a maximum-severity Oracle vulnerability that China-linked threat actors have exploited across government and commercial…
Check Point Researchers Weaponize Microsoft Defender Remediation Driver for Kernel-Level Attacks
August 23, 2026 Check Point Research has disclosed a technique that weaponizes Microsoft Defender’s own signed boot-time remediation driver, BTR.sys, to execute arbitrary kernel-level file and registry operations on fully patched Windows systems.…
MoYu Group Deploys Proxy Botnet Malware on Android Car Head Units via DoFun Update App
August 22, 2026 Kaspersky researchers have uncovered a supply-chain attack targeting Android-based car head units that uses a legitimate device-update app to spread proxy botnet malware. The operation, attributed to the MoYu threat actor group, marks the…