Helix Ransomware Attacks Sonoco
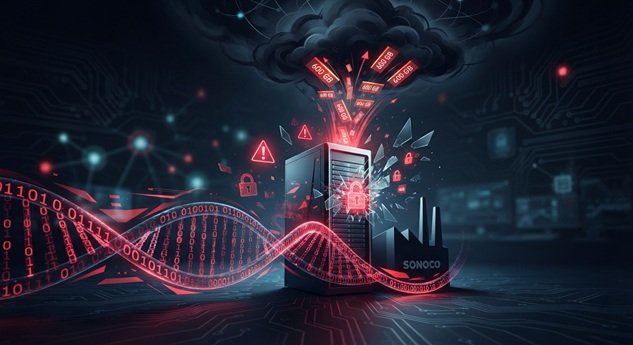
The Helix ransomware gang has claimed an attack on Sonoco, a U.S.-based global packaging manufacturer with roughly $6.8 billion in annual revenue. The group allegedly exfiltrated more than 600 GB of data from the company. Furthermore, the stolen files have already been published on the Helix leak site. This incident highlights how ransomware operators continue to target large industrial organizations for both data theft and public pressure.
What Happened: Helix Ransomware Hits Global Packaging Manufacturer Sonoco
Sonoco appeared on the Helix ransomware leak site on November 17, 2026. The listing claims 578,129 files totaling approximately 603 GB were stolen. The group has made those files available through multiple GoFile archive links. Consequently, employees, customers, and partners of Sonoco face potential exposure of sensitive business records.
Sonoco operates in 33 countries and provides packaging products across consumer, industrial, healthcare, and food-service sectors. Therefore, the breadth of the company’s footprint means the stolen data could span intellectual property, supply-chain documents, financial records, and employee information across multiple geographies.
Helix is a ransomware-as-a-service operation that emerged in mid-2026. It follows a double-extortion model. First, the operators encrypt systems. Then they threaten to publish stolen data if the victim refuses to pay. The Sonoco listing follows that playbook. The group did not disclose an exact ransom demand publicly, but the published archives suggest the operators are treating this as a confirmed leak.
Technical Details of the Helix Ransomware Attack on Sonoco
While Sonoco has not released a public incident report, the Helix leak data provides some technical indicators:
- Data volume: Approximately 602.96 GB spread across T1 through T4 GoFile archives.
- File count: 578,129 individual files.
- Leak site: Helix’s public extortion portal.
- Discovery timestamp: November 17, 2026, 19:22 UTC.
Helix typically gains access through phishing emails, stolen credentials, or vulnerable remote-access tools. After initial access, the operators move laterally using built-in Windows utilities and living-off-the-land binaries. They then deploy a custom encryptor and exfiltrate data through cloud storage services or file-sharing platforms like GoFile. In the Sonoco case, the presence of archived files on a public sharing service confirms the exfiltration phase was completed before the leak announcement.
Threat Actor Profile
Helix operates as a closed affiliate program. Access to its tooling is sold to vetted partners who carry out the actual intrusions. The group maintains a Tor-based leak site and uses social-media channels, including X, to amplify claims. Bitsight’s threat intelligence assigns Helix a high DVE score, reflecting both active exploitation and broad targeting of manufacturing and logistics organizations.
Business and Operational Impact
The Sonoco breach carries consequences for multiple stakeholder groups:
- Operational disruption: If encryption occurred, production scheduling, order fulfillment, and shipping systems may face downtime.
- Intellectual property exposure: Packaging designs, manufacturing processes, and supplier contracts are valuable to competitors.
- Customer and supplier risk: Third-party contracts, pricing agreements, and contact databases could be misused for fraud or further targeting.
- Employee data exposure: Payroll records, personally identifiable information, and benefits data may be included in the stolen archive.
- Regulatory and legal exposure: Depending on the jurisdictions affected, Sonoco may face breach-notification obligations under GDPR, state-level U.S. privacy laws, or sector-specific regulations.
- Reputational damage: Public confirmation of a 600 GB leak erodes trust with existing customers and prospective partners.
Mitigation and Recommendations
Immediate Actions for Organizations
- Monitor for leaked credentials. Employees and partners with Sonoco accounts should change passwords immediately and enable multi-factor authentication wherever possible.
- Watch for phishing. Threat actors often follow ransomware leaks with targeted phishing campaigns using leaked contact lists.
- Review third-party risk. Organizations in Sonoco’s supply chain should assess whether their own data appears in the leaked archives.
- Check exposure databases. Use breach-notification services and dark-web monitoring to identify if employee credentials have surfaced.
Defensive Hardening
- Segment manufacturing networks from corporate IT and internet-facing systems.
- Restrict remote-access tools to managed devices and enforce conditional-access policies.
- Deploy endpoint detection and response solutions with behavioral analytics tuned for ransomware behaviors.
- Back up critical systems to immutable storage and test recovery procedures quarterly.
- Conduct tabletop exercises that include both encryption and data-leak scenarios.
Bottom line: The Helix ransomware attack on Sonoco is a confirmed data breach with more than 600 GB of files already published. Organizations connected to Sonoco should treat this as an active exposure risk, rotate credentials, monitor for abuse, and review their own supply-chain security posture.
Incident Summary
| Incident: | Helix Ransomware Attack on Sonoco |
| Target: | Sonoco (U.S.-based global packaging manufacturer) |
| Revenue: | Approximately $6.8 billion annually |
| Threat Actor: | Helix ransomware group |
| Data Volume: | 602.96 GB (578,129 files) |
| Disclosure Date: | November 17, 2026 |
| Leak Status: | Published on Helix extortion site via GoFile archives |
| Attack Vector: | Unknown; typical Helix methods include phishing and stolen credentials |
References
- HookPhish, “Sonoco Data Breach: Helix Ransomware Claim (Nov 2026),” November 18, 2026, https://www.hookphish.com/blog/ransomware-group-helix-hits-sonoco/, accessed November 18, 2026.
- Ransomware.live, “Victim: Sonoco – Helix,” November 17, 2026, https://www.ransomware.live/id/U29ub2NvQEhlbGl4, accessed November 18, 2026.
- Dark Web Informer, “Helix Ransomware Claims Sonoco,” November 18, 2026, https://x.com/DarkWebInformer/status/2122808289390149754, accessed November 18, 2026.
- The Record by Recorded Future, “Shipping Giant Maersk Says Recent Cyber Incident Affected Legacy System,” November 12, 2026, https://therecord.media/shipping-giant-maersk-says-recent-incident-affected-legacy-system, accessed November 18, 2026.