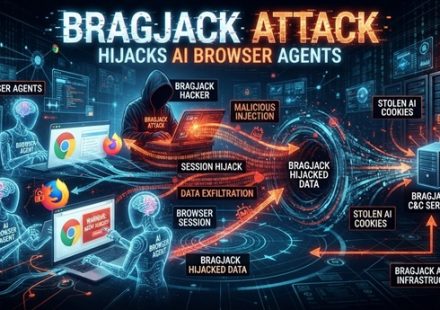
BragJack Attack Hijacks AI Browser Agents

September 19, 2026 Security researcher Gal Weizman of Forever Security has disclosed BragJack, a new attack technique that hijacks AI browser agents through malicious extensions. The proof-of-concept works against five major Chromium-based browsers and…
Iranian Hackers Deploy CHOSEN BRICK Malware
September 16, 2026 Government agencies in the United States, United Kingdom, and the Netherlands have issued a joint warning about an Iranian state-linked espionage campaign that deploys a Windows malware strain named CHOSEN BRICK. The malware targets…
Google Patches Actively Exploited Android Zero-Day on Pixel Devices
September 16, 2026 Google has released the September 2026 security patches for Pixel devices. This update fixes 110 vulnerabilities, including one zero-day flaw that is actively exploited in targeted attacks. The zero-day, tracked as CVE-2026-58704, is a…
Cisco Secure Email Gateway CVE Critical Zero-Day
September 15, 2026 Cisco has disclosed a critical zero-day vulnerability in its Secure Email Gateway that threat actors are actively exploiting to gain root-level command execution. The flaw, tracked as CVE-2026-76461, carries a CVSS score of 9.8 and was…
CISA Confirms Active Exploitation of Critical GitLab Path Traversal
September 14, 2026 CISA has added CVE-2026-85706 to its Known Exploited Vulnerabilities catalog after confirming active exploitation in the wild. This maximum-severity path traversal flaw affects GitLab Community Edition and Enterprise Edition.…
UNC3569 Exploits Sogou Input Method Flaw to Deploy GRAYRABBIT Backdoor
September 13, 2026 Threat actors linked to a China-aligned espionage group are exploiting a critical vulnerability (CVE-2026-51990) in Tencent’s Sogou Input Method for Windows to deploy the GrayRabbit backdoor. The flaw allows one-click remote code…
Passkey-Themed Phishing Attacks Target Microsoft 365
September 11, 2026 Microsoft has confirmed that threat actors linked to the ShinyHunters and Helix extortion gangs are conducting sophisticated passkey-themed phishing campaigns that compromise corporate Microsoft 365 accounts and steal sensitive data.…
Critical Path Traversal Flaw Under Active Exploitation
September 11, 2026 On September 10, 2026, GitLab disclosed CVE-2026-85706, a maximum-severity path traversal vulnerability in its repository commits API. The flaw carries a CVSS score of 10.0 and allows unauthenticated attackers to read arbitrary files…
Cisco Critical FMC Authentication Bypass Confirmed Under Active Exploitation
September 10, 2026 Cisco has confirmed that a maximum-severity authentication bypass vulnerability tracked as CVE-2026-20079 in its Secure Firewall Management Center (FMC) software is being actively exploited in attacks. Furthermore, the U.S.…
ShieldCrash Zero-Day Bypasses Microsoft Defender Patch and Grants SYSTEM Access
An anonymous security researcher known as Nightmare Eclipse has released a new Microsoft Defender zero-day exploit named ShieldCrash on September 9, 2026. The exploit bypasses a recently patched Defender flaw called ShieldBreak and grants SYSTEM…