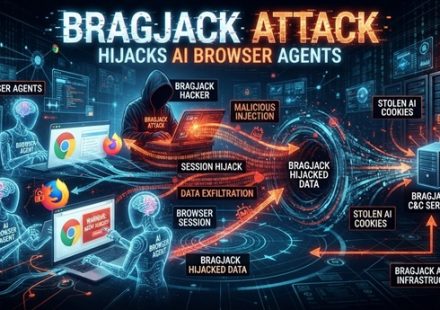
BragJack Attack Hijacks AI Browser Agents

September 19, 2026 Security researcher Gal Weizman of Forever Security has disclosed BragJack, a new attack technique that hijacks AI browser agents through malicious extensions. The proof-of-concept works against five major Chromium-based browsers and…
Check Point Root RCE via Management Server Login Flaw
September 18, 2026 Check Point Software has disclosed a critical vulnerability that lets unauthenticated attackers execute code with root privileges on Security Management Server and Log Server systems. The flaw, tracked as CVE-2026-91843, stems from a…
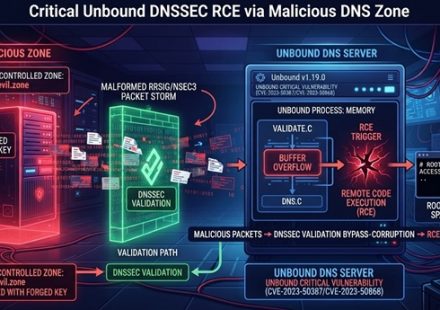
Critical Unbound DNSSEC Validator RCE via Malicious DNS Zone
September 18, 2026 A critical heap overflow vulnerability in the Unbound DNS resolver enables remote code execution through malicious DNS zones. The flaw, tracked as CVE-2026-81642, affects every Unbound release before version 1.26.1 and carries a CVSS…
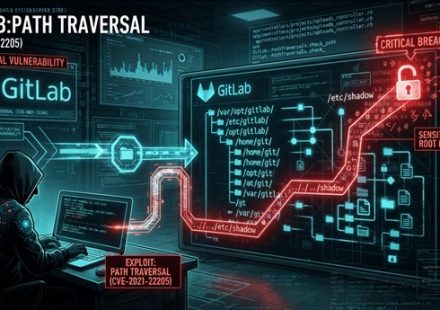
CISA Confirms Active Exploitation of Critical GitLab Path Traversal
September 14, 2026 CISA has added CVE-2026-85706 to its Known Exploited Vulnerabilities catalog after confirming active exploitation in the wild. This maximum-severity path traversal flaw affects GitLab Community Edition and Enterprise Edition.…
UNC3569 Exploits Sogou Input Method Flaw to Deploy GRAYRABBIT Backdoor
September 13, 2026 Threat actors linked to a China-aligned espionage group are exploiting a critical vulnerability (CVE-2026-51990) in Tencent’s Sogou Input Method for Windows to deploy the GrayRabbit backdoor. The flaw allows one-click remote code…
ShieldCrash Zero-Day Bypasses Microsoft Defender Patch and Grants SYSTEM Access
An anonymous security researcher known as Nightmare Eclipse has released a new Microsoft Defender zero-day exploit named ShieldCrash on September 9, 2026. The exploit bypasses a recently patched Defender flaw called ShieldBreak and grants SYSTEM…
Critical Kernel Flaw Enables Unauthenticated Remote Code Execution
September 9, 2026 SAP has patched a maximum-severity vulnerability in its kernel that enables unauthenticated remote code execution with administrative privileges. Tracked as CVE-2026-44756 and codenamed OVERPASS, the flaw carries a CVSS score of 10.0…
PEEP Toolkit Turns Chrome and Edge Into Post-Compromise Backdoors
September 8, 2026 A newly disclosed post-exploitation toolkit called PEEP is turning Google Chrome and Microsoft Edge into persistent backdoors for host-level command execution. Cybersecurity researchers at SOCRadar disclosed the framework this week,…
MikroTik RouterOS Attack Chain Hijacks Devices
September 7, 2026 Threat actors are actively exploiting a chain of two critical vulnerabilities in MikroTik routers. The attack, dubbed “MikroTrick,” allows hackers to bypass SSH authentication and escalate privileges to gain full administrative control…
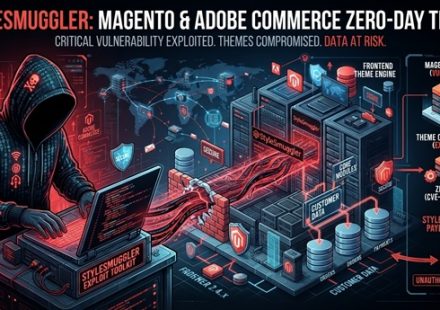
StyleSmuggler Magento and Adobe Commerce Zero-Day
September 06, 2026 Attackers are actively exploiting a new unpatched vulnerability in Magento Open Source and Adobe Commerce that lets them run malicious code on an online store’s server without logging in. Dutch e-commerce security company Sansec…