FBI Warns ARTEX AI Hacking Framework Powers Global Cyberattacks

November 15, 2026 The FBI has issued a FLASH advisory warning that threat actors are using ARTEX, an AI-powered penetration testing framework, to automate cyberattacks against organizations worldwide. The open-source tool turns a plain-language goal into…
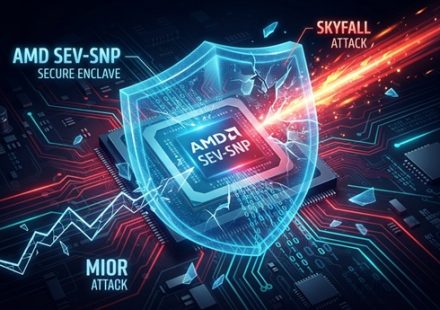
Mior and Skyfall Attacks Break AMD SEV-SNP Confidentiality
November 15, 2026 The Mior and Skyfall attacks disclosed this week break the confidentiality guarantees of AMD SEV-SNP, the confidential computing platform used to protect virtual machines from malicious cloud hosts. Two ETH Zurich research teams showed…
Cursor Security Breach Caused by Malicious Claude Code Extension
November 15, 2026 Cursor confirmed a security breach that let hackers distribute a malicious Claude Code extension through its marketplace after stealing credentials from AI infrastructure provider Fireworks AI. The incident, disclosed on November…
N-able 4EverAble2Shell Zero-Day Actively Exploited
November 14, 2026 The N-able 4EverAble2Shell zero-day is being actively exploited in the wild, chaining Apache Axis CVE-2026-90436 with an N-central privilege escalation flaw to gain root access on remote monitoring and management servers. Security…
Red Hat Quay CVE Lets Attackers Overwrite All Private Containers
November 14, 2026 A critical vulnerability in Red Hat Quay container registry allows attackers to read and overwrite private container images across every repository. This flaw, tracked as CVE-2026-123710, carries a CVSS score of 9.8 and has existed…
Check Point CVE Zero-Day Grants Root Access on Firewalls and Management Servers
November 14, 2026 Check Point Software has released emergency hotfixes for CVE-2026-123039, a high-severity local privilege escalation flaw that threat actors have actively exploited since late October to gain root privileges on enterprise firewalls and…
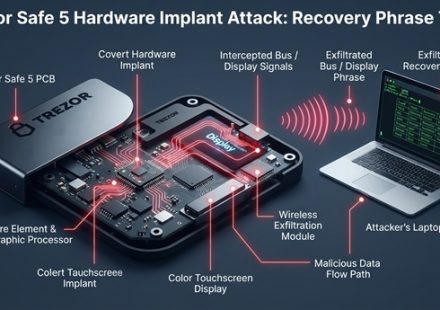
CryptoBilis Supply Chain Attack Steals Recovery Phrases via Cellular Networks
November 13, 2026 Cryptocurrency hardware wallet maker Trezor confirmed that malicious hardware implants in Safe 5 devices sold by Southeast Asian reseller CryptoBilis were designed to steal wallet recovery phrases and transmit them to attackers over…
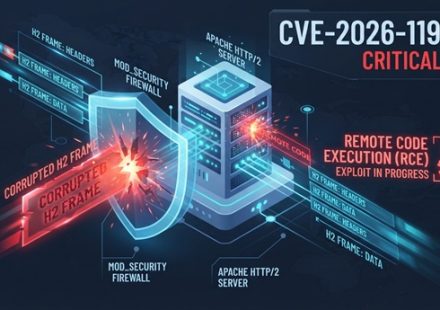
Critical Apache HTTP/2 CVE Enables Unauthenticated Remote Code Execution
November 12, 2026 A critical vulnerability in Apache HTTP Server’s HTTP/2 module allows unauthenticated remote attackers to execute arbitrary code on affected systems. The flaw, tracked as CVE-2026-119618, carries a CVSS score of 9.8 out of 10 and…
AntiFox AI Pentesting Platform Targets AWS Production Secrets in Active Cloud Intrusions
November 11, 2026 Cybersecurity researchers at Arctic Wolf Labs have uncovered an active campaign where attackers abuse AntiFox, an open-source AI-driven penetration testing platform, to steal Amazon Web Services (AWS) credentials and access production…
CISA Adds Cisco BroadWorks XXE CVE to KEV Catalog
November 11, 2026 CISA added CVE-2026-20320 to its Known Exploited Vulnerabilities Catalog on November 10, 2026. This high-severity flaw in Cisco BroadWorks lets unauthenticated remote attackers read sensitive configuration data via a crafted XML…