Critical Apache HTTP/2 CVE Enables Unauthenticated Remote Code Execution
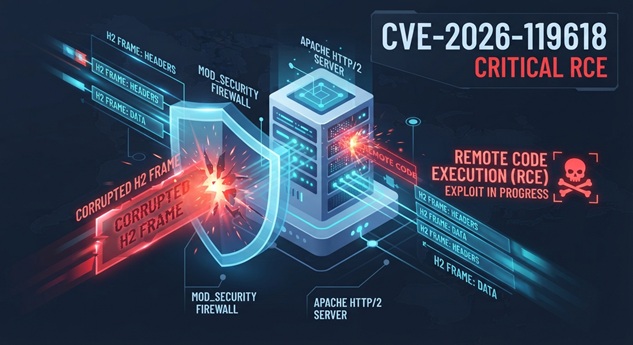
A critical vulnerability in Apache HTTP Server’s HTTP/2 module allows unauthenticated remote attackers to execute arbitrary code on affected systems. The flaw, tracked as CVE-2026-119618, carries a CVSS score of 9.8 out of 10 and affects versions 2.4.55 through 2.4.70. Patched builds shipped yesterday in version 2.4.71. Furthermore, public research has already demonstrated a reliable exploit against default configurations.
What Happened: Critical Apache HTTP/2 RCE Disclosed with Public Exploit
On November 11, 2026, the Apache HTTP Server project released version 2.4.71 to fix a critical remote code execution flaw in its HTTP/2 module, mod_http2. The vulnerability allows any reachable attacker to take full control of the server process without providing credentials.
Red Hat, which embeds the server in Red Hat Enterprise Linux, published its severity assessment on November 11. The vendor confirmed that public research has demonstrated a reliable exploit against a server running in its default configuration with mod_http2 enabled. However, no exploitation in the wild had been reported at the time of publication.
Security company Wiz also published an analysis on November 11. Wiz noted that no exploit was publicly available and that no in-the-wild exploitation had been observed. Therefore, the risk remains primarily from the existence of a working proof of concept rather than active campaigns.
Technical Details of the CVE-2026-119618 Vulnerability
The flaw resides in mod_http2, the module that implements the HTTP/2 protocol inside Apache HTTP Server. HTTP/2 must be explicitly enabled through the Protocols directive, which administrators add to server-wide or virtual-host configurations.
Attack vectors and prerequisites include:
- An accessible Apache HTTP Server instance with
mod_http2loaded - The
Protocolsdirective includesh2(HTTP/2 over TLS) orh2c(HTTP/2 over cleartext) - No authentication or special client credentials are required
Standalone builds of the module, released on GitHub as mod_h2, are also affected from version 2.0.8 through 2.0.42. Notably, that repository was archived on June 9 and has not published a fixed release.
Consequently, admins running the standalone module must disable HTTP/2 rather than wait for an update.
Business and Operational Impact
Apache HTTP Server powers roughly one-third of all websites on the internet. Any unauthenticated RCE in this codebase has broad implications for hosting providers, enterprises, and cloud workloads.
Key impact categories include:
- Complete server compromise: Successful exploitation grants control of the server process
- Data exposure: Attackers can read files, steal credentials, and pivot into internal networks
- Service disruption: Compromised hosts may be taken offline for forensics and rebuilding
- Supply-chain risk: Managed hosting and platform-as-a-service providers may host many tenants on one affected instance
Moreover, the vulnerability was discovered by two separate research efforts. Anthropic’s OSS Scanner reported it on October 26, and Google Cloud Vulnerability Research independently disclosed it last week. The dual discovery timeline suggests the bug class was being actively investigated.
Mitigation and Recommendations
Immediate Actions for Defenders
- Upgrade to Apache HTTP Server 2.4.71 or the equivalent distribution package as soon as possible
- If patching is not immediate, remove
h2andh2cfrom theProtocolsdirective and leave onlyhttp/1.1 - Audit every virtual host for HTTP/2 enablement, not just the server-wide configuration
- Verify module versions on container images and custom builds, then replace end-of-life mod_h2 standalone builds
- Monitor access logs for anomalous HTTP/2 traffic preceding unexpected process behavior
Platform-Specific Patch Status
Red Hat shipped fixes for RHEL 9 and 10 on November 11. RHEL 8 and earlier releases do not contain the vulnerable code. Debian unstable (sid) received apache2 2.4.71-1, while Debian stable branches remain vulnerable at the time of writing. Amazon Linux fixes are pending, and Ubuntu had no published tracker page when checked.
Red Hat rates the flaw as Important on RHEL 9 and 10 rather than Critical. Their mod_http2 packages give each HTTP/2 stream its own memory allocator, which makes exploitation significantly harder.
Bottom line: If your Apache HTTP Server instance has HTTP/2 enabled, treat this as a patch-now event. The combination of unauthenticated access, reliable public exploit, and extremely widespread deployment creates a narrow window before mass exploitation begins.
Incident Summary
| CVE ID / Incident: | CVE-2026-119618 |
| Affected Systems: | Apache HTTP Server 2.4.55–2.4.70 with mod_http2 enabled; mod_h2 standalone 2.0.8–2.0.42 |
| Disclosure Date: | November 11, 2026 |
| Patch Status: | Fixed in Apache HTTP Server 2.4.71; distribution patches available for RHEL 9/10, Debian sid |
| CVSS Score: | 9.8 (Critical) |
| Exploit Status: | Public proof of concept demonstrated; no confirmed in-the-wild exploitation reported |
References
- The Hacker News, “Critical Apache HTTP/2 Flaw Could Let Unauthenticated Attackers Execute Code Remotely,” November 12, 2026, https://thehackernews.com/2026/11/critical-apache-http2-flaw-could-let.html
- Apache HTTP Server Security Advisory, “CVE-2026-119618,” November 11, 2026, https://httpd.apache.org/security/vulnerabilities_24.html#CVE-2026-119618
- Red Hat Security Advisory, “CVE-2026-119618 Severity Assessment,” November 11, 2026, https://access.redhat.com/security/cve/cve-2026-119618
- Wiz, “CVE-2026-119618: RCE Apache HTTP Server Vulnerability Analysis,” November 11, 2026, https://www.wiz.io/blog/cve-2026-119618-rce-apache-http-server-vulnerability
- BleepingComputer, “Apache HTTP Server Patches Critical HTTP/2 Remote Code Execution Flaw,” November 12, 2026, https://www.bleepingcomputer.com/news/security/apache-http-server-patches-critical-http-2-remote-code-execution-flaw/