SonicWall GMS End-of-Life Flaws Expose Files and Database

November 5, 2026 SonicWall disclosed two critical vulnerabilities in its end-of-life Global Management System that will not receive patches. Administrators must migrate to SonicWall Network Security Manager or accept permanent exposure. What Happened:…
Siemens IoT2050 Node-RED Flaw Under Active Exploitation
November 4, 2026 A maximum-severity authentication flaw in Siemens SIMATIC IoT2050 Advanced devices is being actively exploited in the wild. Attackers are abusing CVE-2026-58115 to deploy Linux bot payloads and persistent command backdoors on unprotected…
Barracuda Critical Flaws Allow Root Access
November 3, 2026 Barracuda Networks disclosed two critical vulnerabilities in its Email Security Gateway and other products that allow attackers to gain root access to affected appliances. The flaws, tracked as CVE-2026-116606 and CVE-2026-111560,…
Drupal Commerce Core Active Access Bypass Threatens 42,000 E-Commerce Sites
November 3, 2026 Drupal warned administrators this week that attackers are actively exploiting a critical access bypass vulnerability in the Commerce Core module. Tracked as CVE-2026-118539, the flaw allows unauthenticated threat actors to bypass…
CISA Confirms GitLab CI/CD RCE Exploitation
November 2, 2026 CISA has confirmed active exploitation of a maximum-severity remote code execution (RCE) flaw in GitLab. Over 1,000 self-managed GitLab servers remain unpatched and exposed to ongoing attacks, despite patches being available for three…
Android SMS of Death Zero-Click Text Message Crash Threatens Phones
November 1, 2026 A zero-click Android vulnerability, dubbed the SMS of Death, lets attackers crash phones by sending a single malformed text message. The flaw, tracked as CVE-2026-58882, disrupts cellular service and can even interrupt emergency calls…
Northflank Breach Exposes AI API Keys in Black October Campaign
October 31, 2026 On October 30, 2026, cloud application hosting platform Northflank disclosed a security breach that exposed decrypted customer environment variables. Attackers abused stolen AI API keys across multiple accounts in what security…
Hackers Scan for Critical Oracle EBS RCE Flaw Days After Patch
October 29, 2026 Threat actors have started scanning for a newly patched critical vulnerability in Oracle E-Business Suite (EBS) within days of its disclosure. Tracked as CVE-2026-101767, this unauthenticated SQL injection flaw carries a CVSS score of…
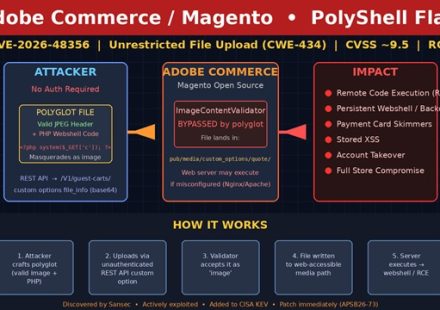
CISA Adds Adobe Commerce PolyShell Flaw to KEV
October 28, 2026 The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a critical Adobe Commerce and Magento vulnerability to its Known Exploited Vulnerabilities (KEV) catalog on October 27, 2026. Tracked as CVE-2026-48356 and dubbed…
CISA Adds Brotli2Shell to KEV Catalog Enables RCE Across Node.js, .NET, and Python
October 28, 2026 CISA has added CVE-2026-111497 to its Known Exploited Vulnerabilities catalog after confirmed in-the-wild exploitation. The flaw, also known as Brotli2Shell, Node2Shell, and HTTP2Shell, is an out-of-bounds write in Google’s Brotli…