CISA Confirms PHP2Shell RCE Exploitation Added to KEV Catalog

October 27, 2026 CISA confirmed active exploitation of two critical PHP vulnerabilities collectively tracked as PHP2Shell. Threat actors can exploit CVE-2026-109618 and CVE-2026-109619 to gain unauthenticated remote code execution on millions of…
k0t Threat Actor Breaches Enterprise Firewalls and VPNs
October 25, 2026 Cybersecurity researchers from Group-IB and NyxLab have uncovered a massive campaign that has breached enterprise firewalls and VPNs worldwide. Consequently, the threat actor known as k0t has exposed over 70,000 credentials and…
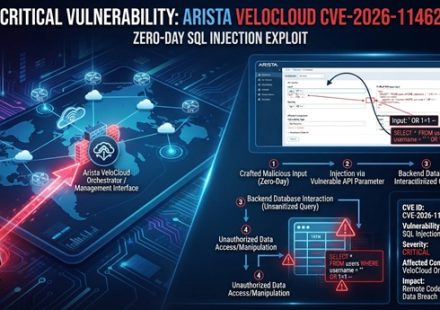
Arista VeloCloud Orchestrator SQL Injection Zero-Day Grants Operator Privileges
October 22, 2026 Arista Networks disclosed a critical zero-day vulnerability in VeloCloud Orchestrator on October 22, 2026. CVE-2026-114625 lets any authenticated user escalate to operator privileges through SQL injection. Attackers are actively…
eMudhra CA Private Keys Compromised
October 20, 2026 The private keys of eight eMudhra intermediate certificate authority certificates have been compromised. Mozilla and Google confirmed the breach on October 20, 2026, after a researcher reported it on the evening of October 17. The…
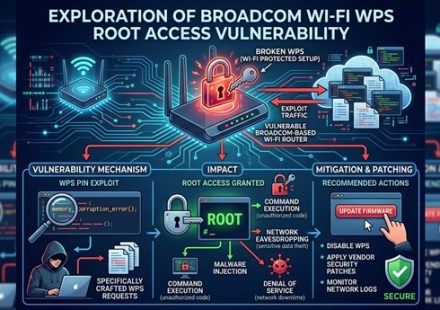
Broadcom Wi-Fi WPS Vulnerability Grants Root Access to Nearby Attackers
October 20, 2026 A newly disclosed vulnerability in Broadcom’s Wi-Fi software lets attackers within wireless range take complete control of vulnerable routers without knowing the Wi-Fi password. Security researcher Quentin Kaiser revealed the flaw…
Rank Math PRO Supply Chain Attack Delivers Self-Restoring Backdoor
October 19, 2026 Attackers compromised the official download channel of Rank Math PRO, a popular WordPress SEO plugin, and distributed a self-restoring backdoor to any site that installed or updated the plugin during an 11-hour window on October 15–16,…
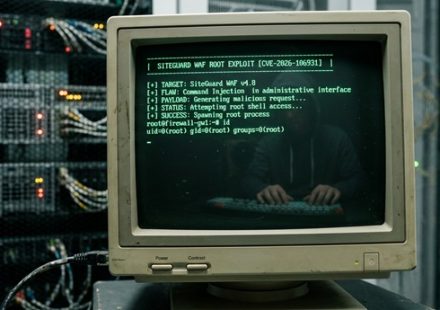
SiteGuard WAF Actively Exploited for Root Command Execution
October 18, 2026 Attackers are actively exploiting a critical OS command injection vulnerability in the SiteGuard Server Edition web application firewall. The flaw, tracked as CVE-2026-106931, allows threat actors to execute commands with root or SYSTEM…
ARMORY CASTLE Exploits BeyondTrust Remote Support Zero-Day
October 15, 2026 A critical authentication bypass vulnerability in BeyondTrust Remote Support has been exploited as a zero-day by a suspected China-nexus espionage group since August 2026. The flaw, tracked as CVE-2026-102764, lets unauthenticated remote…
Hackers Breach 162+ Microsoft 365 Tenants via Compromised Vendor Credentials
October 17, 2026 ConnectWise has shut down customer access to its Cloud Backup service after hackers compromised vendor application credentials and used them to breach at least 162 Microsoft 365 tenants. The incident is an active supply-chain attack that…
Drupal Field UI Critical RCE Flaw CVE Grants Unauthenticated Code Execution
October 16, 2026 Drupal maintainers shipped emergency security updates on October 14, 2026, for a critical remote code execution flaw in the Field UI module. Tracked as CVE-2026-108097, the vulnerability carries a near-maximum risk rating of 19 out of 25…