Tensorlake npm Package Compromised by Shai-Hulud Credential-Stealing Worm

October 8, 2026 The npm package tensorlake was compromised on October 8, 2026, in a ChainDrop supply chain attack. Malicious version 0.5.144 contained the Shai-Hulud credential-stealing worm. The malware harvests developer credentials, establishes…
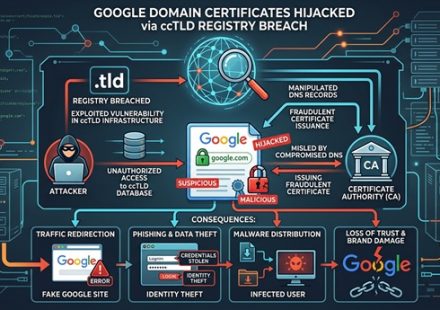
Google Domain Certificates Hijacked via ccTLD Registry Breach
October 7, 2026 Attackers compromised the country-code top-level domain (ccTLD) registries for Ghana, Sierra Leone, and American Samoa. They used this access to change authoritative DNS records and obtain unauthorized HTTPS certificates for Google and…
Critical Unpatched LMCache RCE Threatens LLM Inference Infrastructure
October 7, 2026 A critical, unpatched vulnerability in LMCache allows unauthenticated attackers to execute remote code on the LLM inference cache layer. The flaw, tracked as CVE-2026-105192, carries a CVSS score of 9.8 and remains unpatched as of this…
Microsoft Exchange Flaw Lets Authenticated Attackers Read Other Users Mailboxes
October 7, 2026 Microsoft has released out-of-band security updates for a high-severity vulnerability in Exchange Server. The flaw, tracked as CVE-2026-96940, allows authenticated attackers to read other users’ mailboxes within the same…
Critical Atlassian CVE Allows Unauthenticated File Access in 8 Data Center Products
October 6, 2026 A critical path traversal vulnerability in eight Atlassian Data Center products allows unauthenticated attackers to read sensitive files from the web application root directory. Atlassian disclosed CVE-2026-21589 on October 5, 2026, and…
Dell CSM Flaws Enable Unauthenticated Admin and Root on Kubernetes Nodes
October 4, 2026 Dell disclosed critical vulnerabilities in its Container Storage Modules (CSM) that allow unauthenticated attackers to gain admin access and remote root on Kubernetes nodes. These flaws affect self-hosted CSM deployments and are being…
Zammad CVEs Allow Session Fixation to Root Under Active Exploitation
October 4, 2026 On October 2, 2026, the U.S. Cybersecurity and Infrastructure Security Agency (CISA) added two critical zero-day vulnerabilities in the open-source Zammad helpdesk platform to its Known Exploited Vulnerabilities (KEV) Catalog. The flaws —…
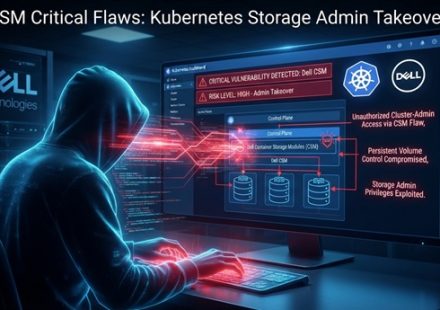
Six Critical Flaws Expose Kubernetes Storage to Full Admin Takeover
October 3, 2026 Dell has patched two maximum-severity vulnerabilities in its Container Storage Modules (CSM) that could let unauthenticated attackers seize full administrative control over enterprise storage arrays connected to Kubernetes environments.…
CVE-2026-104286: Critical FortiMail Zero-Day Under Active Exploit
October 2, 2026 Fortinet is warning customers of a critical vulnerability in FortiMail, tracked as CVE-2026-104286, that attackers are actively exploiting in zero-day attacks. Also, CISA has added the flaw to its Known Exploited Vulnerability (KEV)…
Citrix NetScaler Zero-Days CVEs Under Active Exploitation
September 30, 2026 CISA and Google Threat Intelligence Group have confirmed active exploitation of two critical Citrix NetScaler zero-day vulnerabilities. Attackers are deploying custom web shells and Python tunnelers to gain root access and move…