Critical Atlassian CVE Allows Unauthenticated File Access in 8 Data Center Products
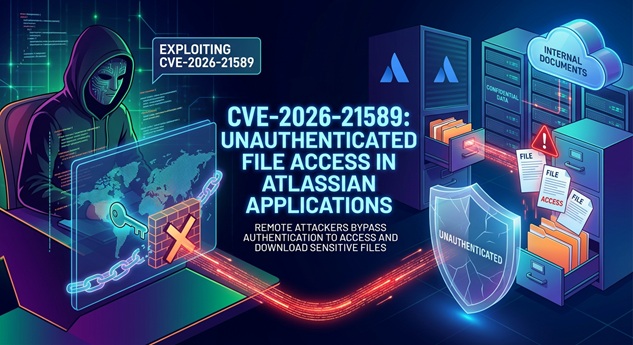
A critical path traversal vulnerability in eight Atlassian Data Center products allows unauthenticated attackers to read sensitive files from the web application root directory. Atlassian disclosed CVE-2026-21589 on October 5, 2026, and rated it 9.3 out of 10. Cloud-hosted instances have already been patched. Self-hosted customers must upgrade immediately or apply temporary mitigations.
What Happened: Critical Atlassian Path Traversal Enables Unauthenticated File Access
On October 5, 2026, Atlassian published a security advisory for CVE-2026-21589, a path traversal flaw affecting eight self-hosted Data Center products. The vulnerability lets an attacker with no authentication read specific files in each product’s web application root directory. The attacker must know the exact file name and path. Directory listing is not possible.
Atlassian rated the flaw 9.3 using CVSS v4.0. The score reflects network reachability, no required privileges, and high confidentiality impact. Integrity and availability impacts on the vulnerable system are rated as none. However, the advisory notes a high impact on other systems, suggesting that exposed files could lead to broader compromise.
Cloud-hosted versions of the affected products have already been patched by Atlassian. Customers using Atlassian Cloud do not need to take any action. Bitbucket Cloud is explicitly not affected.
Technical Details of the CVE-2026-21589 Vulnerability
CVE-2026-21589 is a path traversal vulnerability. In a path traversal attack, a specially crafted request uses directory traversal sequences to access files outside the intended directory. Atlassian’s advisory confirms that requests containing .. directly next to /, \\, or :: can reach files in the web application root.
The web application root directory is the folder on the server that holds the web application itself. In some configurations, this directory may contain sensitive files such as configuration files, credential stores, or deployment artifacts. The exact files and configurations at risk depend on each customer’s deployment.
Atlassian has not disclosed evidence of active exploitation. However, the company cannot confirm whether self-hosted instances have been affected. This uncertainty is significant because a similar Atlassian path traversal, CVE-2021-26086 in Jira Server and Data Center, was added to CISA’s Known Exploited Vulnerabilities catalog in November 2024 after attackers began using it in the wild.
Affected Products and Fixed Versions
The flaw affects all versions of the following eight products before the fixed versions listed. Versions that have reached end of life are also affected. Atlassian recommends upgrading to a fixed long-term support (LTS) version or later.
| Product | Fixed Versions |
| Bitbucket Data Center | 9.4.26, 10.2.8, 10.5.1 |
| Confluence Data Center | 9.2.26, 10.2.19 |
| Jira Software Data Center | 9.12.40, 10.3.26, 11.3.12 |
| Jira Service Management Data Center | 5.12.40, 10.3.26, 11.3.12 |
| Bamboo Data Center | 10.2.24, 12.1.12 |
| Crowd Data Center | 6.3.7, 7.0.3, 7.1.7, 7.2.4 |
| Crucible | 4.9.15 |
| Fisheye | 4.9.15 |
The CVE record also lists older Server editions of these products as affected. For Bamboo Server, Bitbucket Server, Confluence Server, and Crowd Server, no fixed versions are listed. Crowd has had no Server release since version 5.2 in September 2023. Jira Software Server, Jira Service Management Server, Crucible Server, and Fisheye Server list fixed versions starting from 9.12.40, 5.12.40, and 4.9.15 respectively.
Temporary Mitigations
Atlassian provides three temporary blocking rules for customers who cannot upgrade immediately. All rules block requests whose URL contains .. adjacent to /, \\, or ::, including URL-encoded forms.
- All eight products: Deploy a web application firewall (WAF) or reverse proxy rule that blocks matching URLs.
- Confluence, Jira Software, Jira Service Management, Bamboo, and Crowd: Install a Tomcat RewriteValve rule on each node, then restart the instance.
- Bitbucket: Add a rule in
urlrewrite.xmlon every node, mirror, and mirror farm node, then restart.
Atlassian emphasizes that these mitigations are limited and not a replacement for patching. Crucible and Fisheye have only the WAF or reverse proxy option.
Business and Operational Impact
Atlassian Data Center products are widely deployed in enterprises, government agencies, and development teams. The impact of CVE-2026-21589 extends beyond the immediate file-read risk.
- Confidentiality exposure: Sensitive files in the web application root, such as configuration files or deployment secrets, could be read by unauthenticated attackers.
- Lateral movement risk: Exposed credentials or tokens could enable attackers to pivot to other systems, explaining the high impact rating on other systems.
- Compliance implications: Organizations under regulatory frameworks such as PCI-DSS, HIPAA, or SOC 2 may face audit findings if unpatched vulnerabilities expose sensitive data.
- Operational downtime: Atlassian advises customers who cannot upgrade to take instances offline. This recommendation signals the severity of the flaw and may force maintenance windows.
- Server edition risk: Organizations running older Server editions may have no patch path, potentially requiring migration to Data Center or cloud versions.
Mitigation and Recommendations
Immediate Actions for Defenders
- Identify affected instances: Inventory all self-hosted Atlassian Data Center and Server installations. Check versions against the fixed version list.
- Upgrade immediately: Apply the fixed version for each product. Prioritize internet-facing instances.
- Restrict network access: For instances that cannot be patched immediately, restrict access from the public internet. Require VPN or private network access.
- Deploy WAF rules: If immediate patching is not possible, implement the WAF or reverse proxy blocking rules provided by Atlassian.
- Review access logs: Search logs for requests containing traversal patterns. URL-decode each request line up to two times and look for
..next to/,\\, or::.
Long-Term Recommendations
Organizations should treat this vulnerability as a catalyst for broader security improvements. Consider the following steps.
- Migrate from Server editions: Atlassian ended support for Server products in February 2024. Organizations still running Server editions face accumulating unpatched vulnerabilities. Migration to Data Center or cloud versions should be prioritized.
- Harden web application roots: Ensure that sensitive files are not stored in web-accessible directories. Use secure configuration management to prevent accidental exposure.
- Enable centralized logging: Forward access logs to a SIEM or centralized logging platform to detect traversal attempts in real time.
- Conduct regular vulnerability scanning: Include self-hosted Atlassian instances in vulnerability management programs. Scan for known CVEs and misconfigurations.
Bottom line: CVE-2026-21589 is a critical, unauthenticated path traversal affecting eight widely used Atlassian products. Self-hosted customers must patch immediately, apply temporary mitigations if patching is delayed, and review access logs for signs of prior exploitation. The severity rating, historical precedent of similar Atlassian flaws being exploited, and the broad product scope make this a high-priority vulnerability for enterprise security teams.
Incident Summary
| CVE ID / Incident: | CVE-2026-21589 |
| Affected Systems: | Atlassian Data Center: Bitbucket, Confluence, Jira Software, Jira Service Management, Bamboo, Crowd, Crucible, Fisheye |
| Disclosure Date: | October 5, 2026 |
| Patch Status: | Patches available for Data Center versions; Server editions partially covered or unsupported |
| Severity: | CVSS 9.3 (Critical) |
| Exploitation Status: | No confirmed exploitation; similar past flaw (CVE-2021-26086) added to CISA KEV |
References
- Atlassian, “CVE-2026-21589 — Arbitrary File Access Vulnerability Impacts Multiple Products,” October 5, 2026. https://confluence.atlassian.com/security/cve-2026-21589-arbitrary-file-access-vulnerability-impacts-multiple-products-1870495748.html (accessed October 6, 2026).
- The Hacker News, “Critical Atlassian Flaw Lets Unauthenticated Attackers Read Known Files Across 8 Products,” October 6, 2026. https://thehackernews.com/2026/10/critical-atlassian-flaw-lets.html (accessed October 6, 2026).
- NIST National Vulnerability Database, “CVE-2026-21589,” https://github.com/CVEProject/cvelistV5/blob/main/cves/2026/21xxx/CVE-2026-21589.json (accessed October 6, 2026).
- NIST National Vulnerability Database, “CVE-2021-26086,” https://nvd.nist.gov/vuln/detail/CVE-2021-26086 (accessed October 6, 2026).
- Horizon3, “Anthropic Mythos Rejetto HFS RCE,” September 30, 2026. https://horizon3.ai/attack-research/disclosures/anthropic-mythos-rejetto-hfs-rce/ (accessed October 6, 2026).