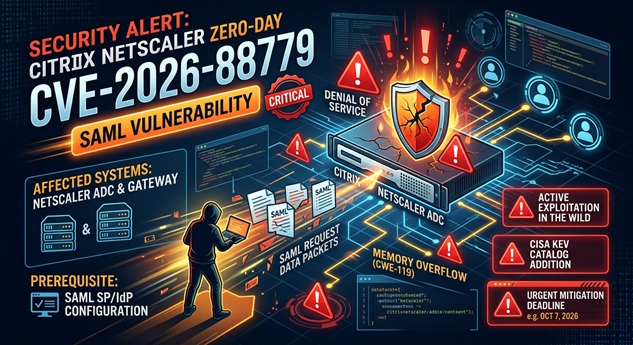
Citrix has released emergency security updates for a new NetScaler vulnerability tracked as CVE-2026-88779. The flaw is a memory buffer weakness affecting NetScaler ADC and NetScaler Gateway appliances that use SAML authentication. Moreover, CISA added this vulnerability to its Known Exploited Vulnerabilities catalog on Sunday, confirming active exploitation in the wild.
What Happened: Citrix NetScaler SAML Zero-Day Triggers Emergency Patch
Citrix disclosed CVE-2026-88779 on October 4, 2026, after observing targeted attacks against customer-managed NetScaler deployments. The vulnerability carries a CVSS score of 8.7 and initially appeared to cause denial-of-service conditions through memory buffer issues. However, security researchers quickly discovered evidence suggesting remote code execution may also be possible.
The attacks began on Thursday, October 1, when NetScaler administrators reported unexpected appliance reboots. In addition, some patched systems continued crashing, which raised suspicions about a new vulnerability rather than scanner-induced instability.
Technical Details of the NetScaler Vulnerability
CVE-2026-88779 is a memory buffer flaw located in the SAML authentication handling of NetScaler ADC and Gateway appliances. Consequently, the vulnerability triggers when appliances process SAML authentication requests while configured as either a SAML Service Provider or Identity Provider.
Administrators can check if their appliances are vulnerable by verifying whether these configurations exist:
- Appliance configured as a SAML SP:
add authentication samlAction - Appliance configured as a SAML IdP:
add authentication samlIdPProfile
Furthermore, Kevin Beaumont reported that patched NetScaler honeypots received requests from multiple source IP addresses and subsequently crashed. Most importantly, one patched honeypot was found running a downloaded malware payload, suggesting exploitation goes beyond simple denial-of-service.
Business and Operational Impact
The impact of CVE-2026-88779 extends across multiple sectors that rely on NetScaler appliances for secure remote access and application delivery. Therefore, organizations should assess their exposure immediately.
- Service Disruption: Repeated exploitation crashes the nsaaad service, which triggers Pitboss process reboots
- Potential Remote Code Execution: Researchers observed shell commands embedded in crafted authentication usernames
- Malware Deployment: At least one honeypot executed a downloaded payload after exploitation
- Federal Compliance Pressure: CISA gave FCEB agencies until October 7 to mitigate
Mitigation and Recommendations
Citrix released emergency firmware updates early Sunday morning to address the vulnerability. Thus, administrators should prioritize patching.
Immediate Actions for Defenders
- Upgrade NetScaler ADC and Gateway to version 14.1-73.41 or 13.1-64.28
- For FIPS deployments, install 14.1-73.41 FIPS or 13.1-37.282
- Apply Citrix Global Deny Lists to block known malicious IP addresses
- Review SAML authentication logs for suspicious username patterns containing shell commands
- Monitor for downloads from IP address 213.209.159[.]55
Detection Guidance
Security teams should monitor NetScaler logs for the following indicators:
- Repeated nsaaad crashes followed by Pitboss-initiated reboots
- Crafted SAML authentication usernames containing shell metacharacters
- Unexpected file downloads or outbound connections from NetScaler appliances
- Anomalous authentication attempts targeting SAML endpoints
Bottom line: Organizations using NetScaler with SAML authentication should treat this as an active threat requiring immediate patching, especially given CISA’s KEV addition and the demonstrated potential for remote code execution.
Incident Summary
| CVE ID / Incident: | CVE-2026-88779 |
| Affected Systems: | Citrix NetScaler ADC and NetScaler Gateway with SAML authentication configured |
| Disclosure Date: | October 4, 2026 |
| Patch Status: | Patches available: 14.1-73.41, 13.1-64.28, and FIPS variants |
| CVSS Score: | 8.7 |
| CISA KEV: | Added October 4, 2026; FCEB deadline October 7, 2026 |
References
- Citrix Security Advisory CTX697174, “Understanding and Addressing CVE-2026-88779 in Citrix NetScaler ADC and Citrix NetScaler Gateway,” October 4, 2026, https://support.citrix.com/support-home/kbsearch/article?articleNumber=CTX697174
- Citrix Community Blog, “Security Update Guidance for NetScaler SAML Authentication Deployments,” October 3, 2026, http://community.citrix.com/techzone-blogs/110_security-updates/security-update-guidance-for-netscaler-saml-authentication-deployments/
- BleepingComputer, “Citrix patches NetScaler SAML zero-day exploited in attacks,” Lawrence Abrams, October 4, 2026, https://www.bleepingcomputer.com/news/security/citrix-patches-netscaler-saml-zero-day-exploited-in-attacks/
- CISA Known Exploited Vulnerabilities Catalog, “CVE-2026-88779,” added October 4, 2026, https://www.cisa.gov/known-exploited-vulnerabilities-catalog