Apple CoreGraphics Zero-Day Actively Exploited in Targeted IOS Attacks

September 29, 2026 Apple has released emergency security updates to fix a zero-day vulnerability in its CoreGraphics framework. The flaw, tracked as CVE-2026-20700, is an out-of-bounds write weakness that has been exploited in “extremely…
Microsoft SharePoint Code-Injection Flaw Added to CISA KEV
Threat actors are actively exploiting a critical Microsoft SharePoint Server vulnerability tracked as CVE-2026-65660. The Cybersecurity and Infrastructure Security Agency added the flaw to its Known Exploited Vulnerabilities catalog on September 25,…
CISA Adds WSO2 and Adobe Commerce Critical Flaws to KEV Catalog
September 27, 2026 CISA has added two new critical vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog, warning that attackers are actively exploiting flaws in WSO2 enterprise software and Adobe Commerce e-commerce platforms. Federal…
Citrix NetScaler RCE Zero-Days Under Active Exploitation
September 27, 2026 Two new unpatched zero-day vulnerabilities in Citrix NetScaler ADC and NetScaler Gateway appliances allow remote code execution and are being actively exploited in the wild. Security firm watchTowr disclosed the flaws on September 26,…
PamStealer macOS Malware Adds Live C2 Decryption
September 25, 2026 Cybersecurity researchers at Jamf Threat Labs have identified a major evolution in the PamStealer macOS infostealer family. The new variant, distributed through a fake cryptocurrency wallet called Wavel, adds server-side payload…
North Korean Hackers Steal $351.6 Million from Bitget Crypto Exchange
September 25, 2026 Cryptocurrency exchange Bitget disclosed today that suspected North Korean hackers have stolen $351.6 million from its hot and warm wallets. Consequently, the company has temporarily suspended all withdrawals while it investigates the…
Meta Muse AI Assistant Creates macOS Backdoor Vulnerability
September 22, 2026 Security researcher Patrick Wardle has disclosed a serious vulnerability in Meta’s new Muse AI assistant for macOS. The flaw lets malware already on a Mac quietly hijack Muse and abuse the broad permissions its owner granted the…
WordPress CVE Critical Path Traversal Enables RCE
September 22, 2026 WordPress has released version 7.1.2 to patch a critical path traversal vulnerability in core. The flaw, tracked as CVE-2026-87902 with a CVSS score of 9.2, allows an unauthenticated attacker to include a readable PHP file from outside…
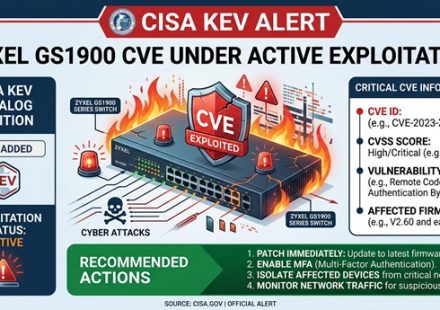
CISA KEV Alert: Zyxel GS1900 Switch CVE Under Active Exploitation
September 22, 2026 Attackers are now actively exploiting a stack-based buffer overflow in Zyxel GS1900 series switches, enabling unauthenticated remote code execution on local area networks. The flaw, tracked as CVE-2026-7273, has been added to…
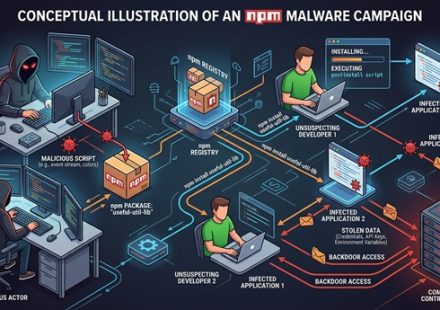
Malicious npm Packages Evade Install-Script Defenses
September 20, 2026 Threat actors have published a malicious npm package named indexed-btree that evades GitHub’s latest install-script defenses by hiding its payload inside normal runtime behavior. The package has already accumulated more than 2…