Citrix NetScaler RCE Zero-Days Under Active Exploitation
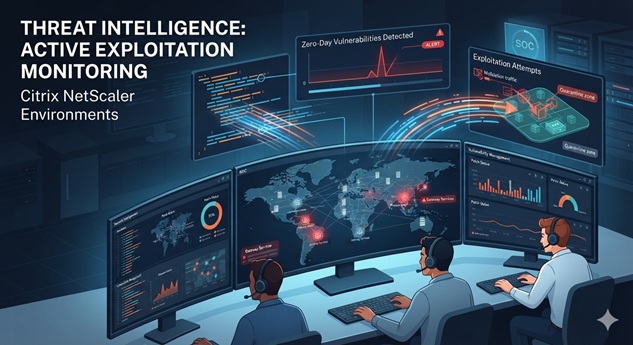
Two new unpatched zero-day vulnerabilities in Citrix NetScaler ADC and NetScaler Gateway appliances allow remote code execution and are being actively exploited in the wild. Security firm watchTowr disclosed the flaws on September 26, and Citrix has not yet confirmed them or published a fix.
NetScaler ADC and NetScaler Gateway sit at the edge of enterprise networks. They handle VPN access, load balancing, and user authentication. Consequently, successful exploitation gives attackers a foothold at the network perimeter.
What Happened: watchTowr Discovers Two Unpatched Citrix NetScaler RCE Zero-Days
On September 26, watchTowr reported that two previously unknown remote code execution vulnerabilities in Citrix NetScaler ADC and NetScaler Gateway are under active exploitation. The firm stated that the information is credible, even though details remain scarce.
Moreover, watchTowr’s follow-up post at 22:19 UTC clarified the situation. Two vulnerabilities exist. Both allow remote code execution. Both are unpatched. Exploitation began before any fix existed. The flaws were discovered during forensic investigations. Citrix communications and patches are expected early in the week of September 28.
However, Citrix has not said whether appliances running the August builds, versions 14.1-73.32 and 13.1-63.21, or any newer builds, are affected by these new flaws. The company had published nothing about the vulnerabilities as of Sunday morning.
Technical Details of the NetScaler Vulnerabilities
The new flaws are distinct from CVE-2026-19490, an authentication bypass vulnerability that Citrix patched on August 19 and that CISA added to its Known Exploited Vulnerabilities catalog on September 9. watchTowr described the new flaws as unpatched, and a fix for the earlier bypass has existed since August 19.
Because exploitation happened before any fix existed, installing a patch will not tell operators whether an attacker already compromised their systems. This is a classic zero-day scenario. Defenders cannot rely on patching alone to determine compromise status.
In 2025, after a NetScaler flaw was exploited as a zero-day against Dutch organizations, the Netherlands’ National Cyber Security Center warned that updating alone did not remove the risk. Attackers could maintain access gained before the patch. Therefore, the agency told administrators to run its check scripts.
Business and Operational Impact
The impact of these vulnerabilities is severe for several reasons:
- Network edge exposure: NetScaler appliances sit at the perimeter. They manage VPN, remote access, and authentication for thousands of organizations worldwide.
- No patch available: Without a confirmed fix, administrators face a difficult decision. They must choose between keeping critical infrastructure online or taking it offline.
- Forensic uncertainty: Because exploitation predates disclosure, organizations cannot assume they are safe simply because they applied previous patches.
- Password and credential exposure: If compromised, the appliance stores service accounts, user credentials, and certificates that attackers can abuse for lateral movement.
Reports of shutdown advice appeared on Reddit on September 26. An administrator posting on r/Citrix wrote that their IT supplier’s security team phoned to advise shutting NetScalers down immediately. Others in the thread said their organizations had done the same.
Mitigation and Recommendations
Until Citrix releases a patch, organizations running NetScaler ADC or NetScaler Gateway should take immediate defensive action.
Immediate Actions for Defenders
- Preserve evidence first: Create a snapshot of any VPX instance. Collect logs from remote syslog servers and NetScaler Console. Generate a technical support bundle and a core dump of the packet engine.
- Isolate the appliance from the network: If possible, disconnect NetScaler from the internet or place it behind a strict firewall.
- Change every service account password and secret: Reset passwords for users who signed in through the appliance. Revoke certificates and private keys stored on it.
- Keep the management interface off the internet: Citrix guidance explicitly states that NetScaler Management Services should never be exposed to the public internet.
- Run the Dutch NCSC check scripts: The 2025 live-appliance script looks for files that indicate compromise. It is not vulnerability-specific and comes with no guarantee, but it offers an additional check.
Long-Term Hardening Steps
Furthermore, organizations should review their NetScaler deployment architecture. Ensure management interfaces are restricted to internal networks. Implement network segmentation so that a compromised edge appliance cannot move laterally. Monitor NetScaler logs for anomalous activity.
Bottom line: With no patch available and active exploitation confirmed, administrators must assume their NetScaler appliances could already be compromised. Evidence preservation and isolation should take priority over waiting for a fix.
Incident Summary
| Incident: | Citrix NetScaler ADC and Gateway Unpatched RCE Zero-Days |
| Disclosure Date: | September 26, 2026 |
| Discovered By: | watchTowr |
| Affected Products: | Citrix NetScaler ADC, NetScaler Gateway |
| Patch Status: | No patch available as of September 27, 2026 |
| Exploitation Status: | Active exploitation confirmed in the wild |
| Related Prior CVE: | CVE-2026-19490 (patched August 19, 2026) |
References
- The Hacker News, “Warning: Two Unpatched Citrix NetScaler RCE Zero-Days Under Active Exploitation,” September 27, 2026, https://thehackernews.com/2026/09/warning-two-unpatched-citrix-netscaler.html.
- BleepingComputer, “ShinyHunters uses WAF bypass trick in Oracle PeopleSoft attacks,” September 26, 2026, https://www.bleepingcomputer.com/news/security/shinyhunters-uses-waf-bypass-trick-in-oracle-peoplesoft-attacks/.
- watchTowr, X (formerly Twitter), “Two new unpatched zero-day vulnerabilities in Citrix NetScaler… actively exploited in the wild,” September 26, 2026, https://x.com/watchtowrcyber.
- CISA, “Known Exploited Vulnerabilities Catalog,” accessed September 27, 2026, https://www.cisa.gov/known-exploited-vulnerabilities-catalog.
- Netherlands National Cyber Security Center, “Checking NetScaler appliances for traces of misuse,” accessed September 27, 2026.