CVE-2026-104286: Critical FortiMail Zero-Day Under Active Exploit
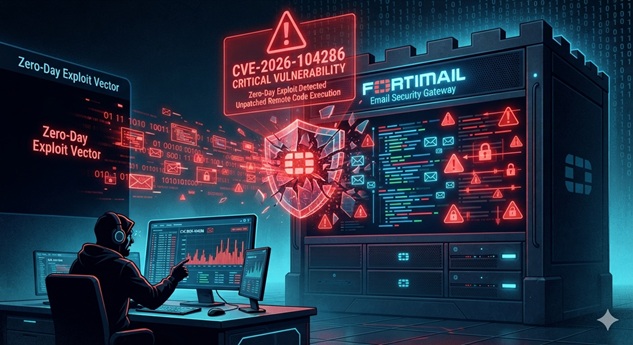
Fortinet is warning customers of a critical vulnerability in FortiMail, tracked as CVE-2026-104286, that attackers are actively exploiting in zero-day attacks. Also, CISA has added the flaw to its Known Exploited Vulnerability (KEV) catalog. Consequently, federal agencies must act fast.
What Happened: CVE-2026-104286 FortiMail Zero-Day Under Active Exploit
On October 1, 2026, Fortinet published an advisory confirming that CVE-2026-104286 is being actively exploited. The vulnerability carries a CVSS score of 9.8 and affects the FortiMail management interface. Therefore, it is one of the most severe email security flaws disclosed this year.
An Improper Limitation of a Pathname to a Restricted Directory (CWE-22) and Improper Neutralization of NULL Byte or NULL Character (CWE-158) vulnerability may allow an unauthenticated attacker to write arbitrary files on the underlying system via crafted HTTP or HTTPS requests. Moreover, successful exploitation could lead to unauthorized remote code execution.
Fortinet discovered the vulnerability internally through Gwendal Guégniaud of its Product Security team. However, by the time the advisory was released, attackers had already exploited it in the wild.
Technical Details of the FortiMail Vulnerability
The flaw resides in the FortiMail management interface and stems from improper input validation. Attackers can exploit it without authentication by sending specially crafted HTTP or HTTPS requests. Furthermore, the vulnerability involves path traversal and null byte injection weaknesses.
Affected Versions
- FortiMail 8.0.0 through 8.0.1
- FortiMail 7.6.0 through 7.6.6
- FortiMail 7.4.0 through 7.4.8
- FortiMail 7.2.0 through 7.2.9
Indicators of Compromise
Fortinet published the following IOCs to help defenders identify compromised systems:
| File | Status | SHA-256 |
| /data/lib/liblog.so | Added | 8015f34dc84922b03688399d7f9fe7a00361789f7e420c7e2a2cdb23e75cef84 |
| /bin/smit | Modified | 77324ac428bde86d351fc5fc06f6d64a6bfe737dfb2743df1d4c5ac2418a5b6a |
| /data/bin/webconsole | Added | 7a6cea9f5c9e2e9994d4e3c4da73f86cf5acd05ea5d312c066c9d1dafd69ee38 |
| /data/bin/mailservice | Added | 4000276a150a165d3c2537d1e19fb393c4de8333076a16655e28059cae82157b |
| /data/etc/httpd.conf | Modified | 703e97c64e61e41dc3aaba580d82bb2aa7b6a11b54ee6fb467ed5d5a3bffdef5 |
| /data/etc/ld.so.preload | Added | 8953ec7960b09f544a880b072ad4e6cfda7a8303f486251d3478dcfdfbac23b6 |
| /data/migadmin.tar.gz | Modified | d6fe51c22b91776f4c961ea58bcac5917f15d560a619d7ce726d3d51795609d3 |
Fortinet also listed the following IP addresses associated with the attacks:
- 79.141.169.187
- 45.129.0.192
Attack Behavior Observed
Log analysis shows attackers configured an archive account named archive234 with remote server 79.141.169.187 and remote directory /uploads. This suggests the attackers set up data exfiltration from compromised appliances. In addition, administrators observed cron jobs executing commands related to /migadmin, failed login attempts, and IBE decryption errors.
Business and Operational Impact
The active exploitation of CVE-2026-104286 poses significant risks to organizations using FortiMail for email security. The potential consequences include:
- Unauthorized remote code execution: Attackers can run arbitrary commands on affected devices.
- Data exfiltration: Log entries show attackers configured archiving to remote servers.
- Email gateway compromise: FortiMail is a critical security control; its compromise exposes entire organizations.
- Persistence: Modified system files and added binaries indicate attackers establish long-term access.
- CISA KEV addition: Federal agencies must patch or mitigate by October 4, 2026.
Fortinet has not disclosed how many systems were compromised or who is behind the attacks. However, the company confirmed it is coordinating with government agencies including CISA.
Mitigation and Recommendations
Immediate Actions for Defenders
- Apply workarounds immediately: Fortinet urges customers to apply shared workarounds until patches are available.
- Disable IBE feature support: Run the following commands on affected systems:
config system encryption ibe
set status disable
end
- Restrict management interface access: Disable internet access to the FortiMail management interface or restrict it to trusted private networks.
- Check for IOCs: Scan systems for the published file hashes and IP addresses.
- Review logs: Look for archive account configurations, cron job executions, and failed login attempts.
Patch Status
Security updates are not yet available for FortiMail 7.4, 7.6, and 8.0. Fortinet has listed FortiMail 7.4.9, 7.6.7, and 8.0.2 as upcoming fixed versions. Therefore, organizations must rely on workarounds in the interim.
Monitoring Guidance
- Monitor FortiMail logs for archive account creation events.
- Watch for cron job executions related to /migadmin paths.
- Alert on connections to IPs 79.141.169.187 and 45.129.0.192.
- Track file integrity for /bin/smit, /data/etc/httpd.conf, and other IOC files.
Bottom line: CVE-2026-104286 is a critical FortiMail zero-day under active exploitation. Organizations should disable IBE features and restrict management interface access immediately while awaiting patches.
Incident Summary
| CVE ID / Incident: | CVE-2026-104286 (FG-IR-26-175) |
| Affected Systems: | FortiMail 7.2.0–7.2.9, 7.4.0–7.4.8, 7.6.0–7.6.6, 8.0.0–8.0.1 |
| Disclosure Date: | October 1, 2026 |
| Patch Status: | Not yet available for 7.4, 7.6, 8.0; workaround released |
| CVSS Score: | 9.8 (Critical) |
| CISA KEV Deadline: | October 4, 2026 |
References
- Fortinet, “FG-IR-26-175: FortiMail — Path traversal and null byte vulnerability,” FortiGuard PSIRT Advisory, October 1, 2026. https://fortiguard.fortinet.com/psirt/FG-IR-26-175
- BleepingComputer, “Fortinet warns of critical FortiMail flaw exploited in zero-day attacks,” October 1, 2026. https://www.bleepingcomputer.com/news/security/fortinet-warns-of-critical-fortimail-flaw-exploited-in-zero-day-attacks/
- CISA, “Known Exploited Vulnerability Catalog,” accessed October 2, 2026. https://www.cisa.gov/known-exploited-vulnerabilities-catalog