SonicWall GMS End-of-Life Flaws Expose Files and Database
SonicWall disclosed two critical vulnerabilities in its end-of-life Global Management System that will not receive patches. Administrators must migrate to SonicWall Network Security Manager or accept permanent exposure.
What Happened: SonicWall GMS End-of-Life Flaws Expose Internal Files and Database Records
SonicWall published security bulletin SNWLID-2026-0019 on November 3, 2026. The alert confirms two vulnerabilities in Global Management System versions 9.5.2 and earlier.
CVE-2026-109593 carries a CVSS score of 9.1 and allows unauthenticated file read. CVE-2026-109594 carries a CVSS score of 6.8 and allows post-authentication SQL injection.
SonicWall stated clearly that the affected product has reached end-of-life. Therefore, no remediation or security update will be released. Organizations are strongly encouraged to upgrade to SonicWall Network Security Manager.
Technical Details of the SonicWall GMS Vulnerabilities
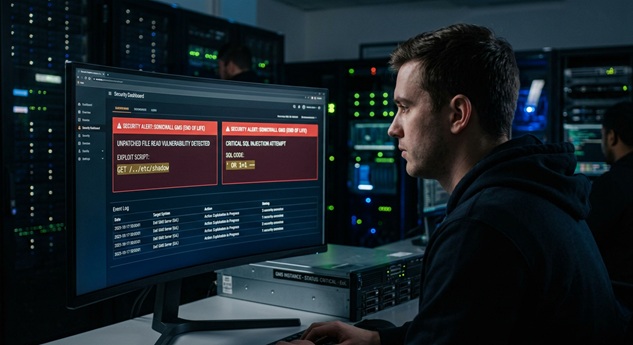
CVE-2026-109593 is an unauthenticated file read flaw. An attacker with network access can read internal GMS files without logging in. This exposure can leak sensitive configuration data, credentials, or system files that enable further attacks.
CVE-2026-109594 is a post-authentication SQL injection vulnerability. An authenticated attacker can access or modify information stored in the GMS database under specific conditions. This could allow privilege escalation, data tampering, or unauthorized administrative actions.
Both flaws affect GMS 9.5.2 and earlier versions. The products are end-of-life, so no patch schedule exists.
Business and Operational Impact
The impact on organizations running legacy GMS is severe and persistent.
- Permanent unpatched exposure: SonicWall will not release fixes. Risk remains until migration is complete.
- Confidential data leakage: CVE-2026-109593 can expose internal files to any attacker on the network.
- Database integrity compromise: CVE-2026-109594 allows authenticated attackers to read or modify GMS database records.
- Compliance violations: Running unpatched end-of-life security infrastructure may violate regulatory requirements.
- Operational disruption: Exploitation could lead to appliance takeover, management plane failure, or lateral movement into the corporate network.
Mitigation and Recommendations
SonicWall recommends migration to Network Security Manager. Until migration is complete, administrators should implement compensating controls.
Immediate Actions for Defenders
- Inventory all SonicWall GMS deployments and confirm version numbers.
- Restrict network access to GMS administrative interfaces to trusted internal networks only.
- Monitor logs for anomalous file access or unexpected database queries.
- Plan and execute migration to SonicWall Network Security Manager as soon as possible.
- Review third-party exposure if GMS manages firewalls or VPN appliances.
Detection and Monitoring Guidance
Network defenders should monitor for unauthorized HTTP or HTTPS requests to GMS endpoints. Furthermore, look for unusual file download patterns from the management server. Database monitoring should flag unexpected SELECT, INSERT, or UPDATE operations against the GMS database from non-administrative accounts.
Bottom line: SonicWall GMS is end-of-life and permanently vulnerable. Migration to Network Security Manager is the only remediation.
Incident Summary
| CVE ID / Incident: | CVE-2026-109593 (CVSS 9.1) and CVE-2026-109594 (CVSS 6.8) |
| Affected Systems: | SonicWall Global Management System 9.5.2 and earlier |
| Disclosure Date: | November 3, 2026 |
| Patch Status: | No patches planned; product end-of-life |
References
- The Hacker News, “SonicWall Won’t Patch EoL GMS Flaws That Could Expose Files, Alter Database Records,” November 4, 2026, https://thehackernews.com/2026/11/sonicwall-wont-patch-eol-gms-flaws-that.html, accessed November 5, 2026.
- SonicWall PSIRT, Security Advisory SNWLID-2026-0019, November 3, 2026, https://psirt.global.sonicwall.com/vuln-detail/SNWLID-2026-0019, accessed November 5, 2026.