Siemens IoT2050 Node-RED Flaw Under Active Exploitation
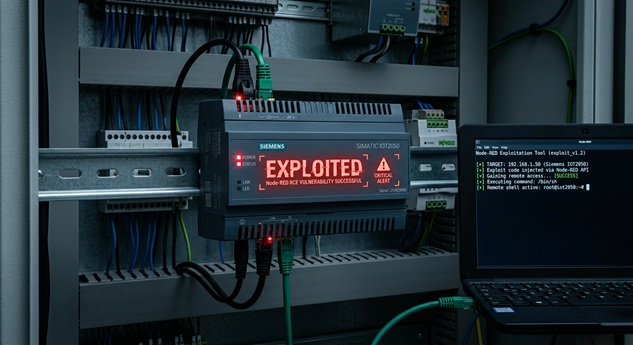
A maximum-severity authentication flaw in Siemens SIMATIC IoT2050 Advanced devices is being actively exploited in the wild. Attackers are abusing CVE-2026-58115 to deploy Linux bot payloads and persistent command backdoors on unprotected industrial systems.
What Happened: Attackers Exploit Siemens IoT2050 Node-RED Flaw for Remote Code Execution
Siemens disclosed CVE-2026-58115 in August 2026. The vulnerability is a missing authentication bug in the Node-RED HTTP interface bundled with SIMATIC IoT2050 Advanced devices running Industrial OS. It carries a CVSS score of 10.0, the highest possible rating.
More than two months after disclosure, VulnCheck confirmed active exploitation on October 30, 2026. An attacker sent a complete exploit in a single POST request to the Node-RED /flows endpoint. Furthermore, the exploit deployed a malicious flow, triggered it automatically, and pulled a binary from an attacker-controlled server.
The attack source was an IP address geolocated in Brazil within Microsoft’s cloud network. Consequently, VulnCheck observed 16 exploit attempts against this flaw between October 30 and November 1, 2026. In addition, the same IP hit eight other CVEs across Apache Solr, Camunda, Gitea, MLflow, Traefik, and Joomla.
Technical Details of the CVE-2026-58115 Vulnerability
CVE-2026-58115 stems from missing authentication on the Node-RED HTTP interface in Siemens SIMATIC IoT2050 Advanced devices. Therefore, unauthenticated remote attackers can create malicious Node-RED flows and execute arbitrary code with maximum privileges.
Node-RED is a flow-based programming tool built on Node.js. It lets users wire together event-driven applications in a browser-based editor. Moreover, it is embedded in commercial ICS and OT products across manufacturing, healthcare, and industrial automation sectors.
The exploit leverages two built-in node types:
- Inject node: Fires a message on a schedule or once at startup
- Exec node: Runs a shell command on the underlying server
When wired together, the flow executes a command as soon as it deploys. Thus, no further attacker interaction is required.
The observed attack chain works as follows:
- The attacker sends a crafted POST request to
/flowswith an encoded malicious flow - The inject node triggers automatically upon deployment
- The exec node runs a shell script wrapper
- The wrapper uses
wget(withcurlas fallback) to fetch a binary from an attacker server - The binary saves to
/dev/shm/.band executes in the background
Subsequent attacks added webshell backdoors. For example, some flows exposed HTTP endpoints such as /cmd wired to exec nodes. Therefore, attackers could run arbitrary commands later by passing them in query parameters. These webshells survive reboots, unlike the memory-resident bot.
Business and Operational Impact
The impact of CVE-2026-58115 extends far beyond a single product line. Siemens SIMATIC IoT2050 devices are deployed in critical infrastructure environments worldwide. A successful exploit grants attackers full control over industrial edge devices with maximum privileges.
Key impact areas include:
- Operational Technology Disruption: Compromised IoT gateways can manipulate industrial processes and sensor data
- Lateral Movement: Attackers can pivot from edge devices into connected OT networks
- Persistent Access: Webshell backdoors remain active after reboots, enabling long-term presence
- Data Exfiltration: Full system access allows theft of sensitive industrial data and credentials
- Supply Chain Risk: Node-RED is used across multiple vendors and platforms beyond Siemens
Moreover, the attacker’s mass-scanning behavior indicates this is not a targeted campaign. It is opportunistic exploitation of internet-exposed industrial devices at scale.
Mitigation and Recommendations
Immediate Actions for Defenders
- Update SIMATIC IoT2050 Advanced devices to Industrial OS V4.3.4.1 or later immediately
- Audit all Node-RED instances for exposure to untrusted networks
- Enable admin authentication on Node-RED installations per the Node-RED security guide
- Restrict network access to Node-RED interfaces using firewalls or VLAN segmentation
- Uninstall Node-RED if it is not required for operations
Detection Guidance
Monitor for the following indicators of compromise:
- Unexpected POST requests to
/flowsendpoints - Outbound connections to suspicious IPs:
85.215.73[.]250and45.194.90[.]57:38472 - New files in
/dev/shm/or/tmp/masquerading as kernel worker threads - New HTTP endpoints exposed by Node-RED flows
Network Hardening
Siemens strongly recommends protecting network access with appropriate mechanisms. In addition, configure environments according to Siemens’ operational guidelines for Industrial Security.
Bottom line: CVE-2026-58115 is a maximum-severity flaw with confirmed active exploitation in industrial environments. Patch now, audit your Node-RED exposure, and enforce authentication. In OT environments, the cost of delay is not just data loss. It is physical process compromise.
Incident Summary
| CVE ID: | CVE-2026-58115 |
| Affected Product: | Siemens SIMATIC IoT2050 Advanced (6ES7647-0BA00-1YA2) with Industrial OS and Node-RED installed |
| Affected Versions: | All versions prior to V4.3.4.1 |
| CVSS Score: | 10.0 (Critical) |
| CWE: | CWE-306: Missing Authentication for Critical Function |
| Disclosure Date: | August 11, 2026 |
| Active Exploitation Confirmed: | October 30, 2026 (VulnCheck) |
| Patch Status: | Available — Update to V4.3.4.1 or later |
| Exploit Complexity: | Low — single POST request, no authentication required |
References
- Siemens ProductCERT, “SSA-834709: Missing Authentication Vulnerability in Node-RED on SIMATIC IoT2050 Advanced with Industrial OS,” August 11, 2026, https://cert-portal.siemens.com/productcert/html/ssa-834709.html, accessed November 4, 2026.
- The Hacker News, “Attackers Exploit Critical Siemens IoT2050 Flaw to Plant Remote Command Backdoors,” November 3, 2026, https://thehackernews.com/2026/11/attackers-exploit-critical-siemens.html, accessed November 4, 2026.
- Help Net Security, “Attackers exploit critical Node-RED flaw to deploy Linux bot and backdoors (CVE-2026-58115),” November 3, 2026, https://www.helpnetsecurity.com/2026/11/03/node-red-cve-2026-58115-exploitation/, accessed November 4, 2026.
- VulnCheck, “Exploitation Targeting Node-RED,” November 2026, https://www.vulncheck.com/blog/exploitation-targeting-node-red, accessed November 4, 2026.
- Node-RED, “Securing Node-RED,” https://nodered.org/docs/user-guide/runtime/securing-node-red, accessed November 4, 2026.