Dell System Update Path Traversal Grants Root to Unauthenticated Attackers
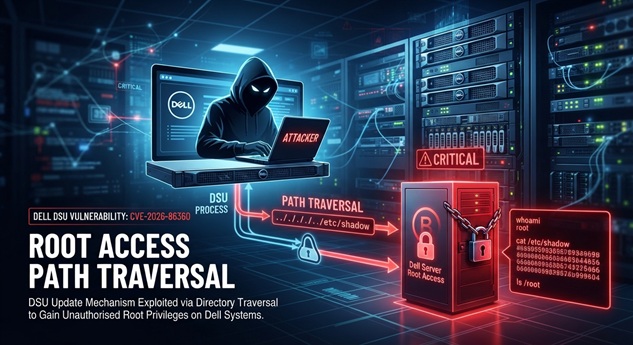
Dell disclosed a critical path traversal vulnerability in its System Update (DSU) command-line tool that allows unauthenticated remote attackers to execute arbitrary code with root privileges. The flaw, tracked as CVE-2026-86360, carries a CVSS score of 9.6 and affects enterprise PowerEdge server deployments worldwide.
What Happened: Dell DSU Path Traversal Enables Root Access
On October 2, 2026, Dell published security advisory DSA-2026-324 warning customers of five vulnerabilities in Dell System Update (DSU). The most severe flaw, CVE-2026-86360, stems from improper limitation of a pathname to a restricted directory. Consequently, an unauthenticated attacker with network access can traverse the filesystem and overwrite critical files.
The vulnerability resides in DSU versions prior to 2.3.0.0. Dell System Update is a CLI deployment tool that IT administrators use to push BIOS, firmware, and software updates to PowerEdge servers running Linux and Windows. Because DSU operates with elevated privileges, successful exploitation grants the attacker complete control over the affected system.
Dell explicitly rated the flaw critical. In its advisory, the company stated that successful exploitation “may allow complete compromise of the vulnerable application and underlying operating system.” Moreover, the FBI and CISA have repeatedly urged software vendors to eliminate path traversal weaknesses, calling them “unforgivable” since at least 2007.
Technical Details of the Vulnerability
CVE-2026-86360 is a path traversal vulnerability classified under CWE-22. It allows an attacker to bypass directory restrictions and write files to arbitrary locations on the filesystem. The attack vector is network-based, requires no authentication, and demands no user interaction.
The affected component is the Dell System Update CLI tool. Systems at risk include:
- Dell PowerEdge servers using DSU for automated patching
- Enterprise environments with centralized update management
- Linux and Windows hosts running DSU versions earlier than 2.3.0.0
In addition to CVE-2026-86360, Dell patched four other high-severity DSU flaws:
- CVE-2026-63697 – Remote code execution vulnerability
- CVE-2026-71168 – Remote code execution vulnerability
- CVE-2026-86361 – Privilege escalation vulnerability
- CVE-2026-86362 – Privilege escalation vulnerability
Furthermore, Dell disclosed two maximum-severity Container Storage Module (CSM) vulnerabilities (CVE-2026-63688 and CVE-2026-63692) on the same day. These flaws allow unauthenticated attackers to gain administrative privileges on Kubernetes nodes.
Business and Operational Impact
The implications for enterprise infrastructure are severe. PowerEdge servers underpin data centers, cloud workloads, and critical business applications worldwide. A root compromise on these systems can cascade rapidly through an environment.
Key business risks include:
- Complete server compromise: Attackers can install persistent backdoors, exfiltrate data, or pivot to adjacent systems
- Supply chain risk: Compromised update infrastructure can be used to distribute malicious firmware or BIOS implants
- Regulatory exposure: Root-level breaches trigger notification requirements under GDPR, HIPAA, and state privacy laws
- Operational downtime: Incident response and forensics on server infrastructure typically require extended maintenance windows
While Dell has not confirmed active exploitation of CVE-2026-86360, the company noted that state-backed threat groups have abused other Dell vulnerabilities in the past. For example, the North Korean Lazarus group deployed a Windows rootkit by exploiting CVE-2021-21551 in Dell’s dbutil driver. Similarly, Chinese cyber spies tracked as UNC6201 exploited a Dell RecoverPoint zero-day (CVE-2026-22769) since mid-2024.
Mitigation and Recommendations
Immediate Actions for Defenders
- Upgrade DSU immediately. Update Dell System Update to version 2.3.0.0 or later. Dell released this version specifically to address the five DSU vulnerabilities.
- Audit PowerEdge deployments. Identify all systems running DSU and verify their patch status. Prioritize internet-facing management interfaces.
- Restrict network access. Limit DSU management plane access to trusted administrative subnets. Disable external access where possible.
- Review CSM deployments. If you use Dell Container Storage Modules, assess exposure to CVE-2026-63688 and CVE-2026-63692 and apply vendor patches.
Detection and Monitoring Guidance
Security teams should monitor for suspicious filesystem activity on PowerEdge servers, particularly unauthorized writes to system directories. In addition, review authentication logs for DSU management sessions and alert on anomalous CLI tool executions.
Bottom line: CVE-2026-86360 is a critical, easily exploitable path traversal flaw in a widely deployed enterprise update tool. Organizations running Dell PowerEdge infrastructure should treat this as a high-priority patching event and upgrade DSU to version 2.3.0.0 without delay.
Incident Summary
| CVE ID: | CVE-2026-86360 |
| Affected Product: | Dell System Update (DSU) |
| Affected Versions: | Prior to 2.3.0.0 |
| Severity: | Critical (CVSS 9.6) |
| Attack Vector: | Network, unauthenticated |
| Impact: | Arbitrary code execution with root privileges |
| Disclosure Date: | October 2, 2026 |
| Patch Status: | Available — upgrade to DSU 2.3.0.0 |
| Additional CVEs: | CVE-2026-63697, CVE-2026-71168, CVE-2026-86361, CVE-2026-86362 (DSU); CVE-2026-63688, CVE-2026-63692 (CSM) |
References
- Dell Technologies, “DSA-2026-324: Security Update for Dell System Update (DSU) Vulnerabilities,” October 2, 2026, https://www.dell.com/support/kbdoc/en-us/000515843/dsa-2026-324.
- BleepingComputer, “New Dell System Update flaw lets hackers gain root privileges,” October 5, 2026, https://www.bleepingcomputer.com/news/security/new-dell-system-update-flaw-lets-hackers-gain-root-privileges/.
- CISA, “CISA Urges Software Developers to Weed Out Path Traversal Vulnerabilities,” May 2024, https://www.cisa.gov/news-events/news/cisa-urges-software-developers-weed-out-path-traversal-vulnerabilities.
- BleepingComputer, “CISA orders feds to patch actively exploited Dell flaw within 3 days,” February 2026, https://www.bleepingcomputer.com/news/security/cisa-orders-feds-to-patch-actively-exploited-dell-flaw-within-3-days/.