Critical RCE Flaws in PHP Runtime Put 75% of Websites at Risk

October 21, 2026 The PHP security team shipped emergency patches for two critical remote code execution flaws tracked collectively as PHP2Shell. These vulnerabilities sit in the PHP runtime itself, which means every website running a vulnerable version…
Rank Math PRO Supply Chain Attack Delivers Self-Restoring Backdoor
October 19, 2026 Attackers compromised the official download channel of Rank Math PRO, a popular WordPress SEO plugin, and distributed a self-restoring backdoor to any site that installed or updated the plugin during an 11-hour window on October 15–16,…
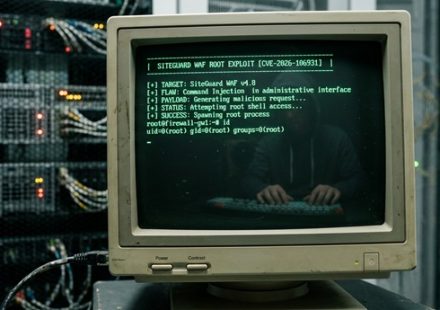
SiteGuard WAF Actively Exploited for Root Command Execution
October 18, 2026 Attackers are actively exploiting a critical OS command injection vulnerability in the SiteGuard Server Edition web application firewall. The flaw, tracked as CVE-2026-106931, allows threat actors to execute commands with root or SYSTEM…
ARMORY CASTLE Exploits BeyondTrust Remote Support Zero-Day
October 15, 2026 A critical authentication bypass vulnerability in BeyondTrust Remote Support has been exploited as a zero-day by a suspected China-nexus espionage group since August 2026. The flaw, tracked as CVE-2026-102764, lets unauthenticated remote…
Drupal Field UI Critical RCE Flaw CVE Grants Unauthenticated Code Execution
October 16, 2026 Drupal maintainers shipped emergency security updates on October 14, 2026, for a critical remote code execution flaw in the Field UI module. Tracked as CVE-2026-108097, the vulnerability carries a near-maximum risk rating of 19 out of 25…
Armory Castle Exploits Remote Support Zero-Day Since August
BeyondTrust patched a critical authentication bypass zero-day in Remote Support after Mandiant confirmed China-nexus actor Armory Castle exploited it since late August, deploying new SAWFLY and BARECLAW malware.
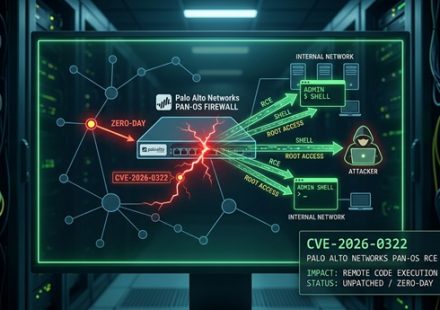
Palo Alto Networks PAN-OS RCE Zero-Day Lets Attackers Gain Root on Firewalls
October 15, 2026 Palo Alto Networks disclosed a high-severity remote code execution vulnerability in PAN-OS on October 14, 2026. The flaw, tracked as CVE-2026-0322, lets authenticated attackers execute code as root on vulnerable firewalls. CISA quickly…
Cisco Secure Email Gateway Zero-Day Grants Root via Malicious Attachments
October 14, 2026 Cisco disclosed an actively exploited zero-day vulnerability in its Secure Email Gateway (SEG) on October 14, 2026. Tracked as CVE-2026-76519, this flaw lets remote unauthenticated attackers execute commands with root privileges by…
Actively Exploited Windows Shell Flaw Bypasses Mark of the Web Defenses
October 14, 2026 Microsoft patched an actively exploited command injection vulnerability in Windows Shell on October 13, 2026. Tracked as CVE-2026-96951, the flaw lets unauthorized attackers bypass Mark of the Web (MOTW) defenses over a network.…
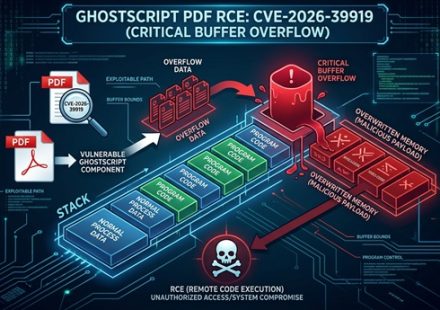
Critical Ghostscript PDF RCE Flaw Lets Attackers Hijack Servers via Malicious PDF Uploads
October 13, 2026 A critical heap buffer overflow vulnerability tracked as CVE-2026-39919 has been disclosed in the Ghostscript interpreter and rendering engine. Also known as the Ghostscript PDF RCE flaw, this vulnerability lets attackers execute remote…