SiteGuard WAF Actively Exploited for Root Command Execution
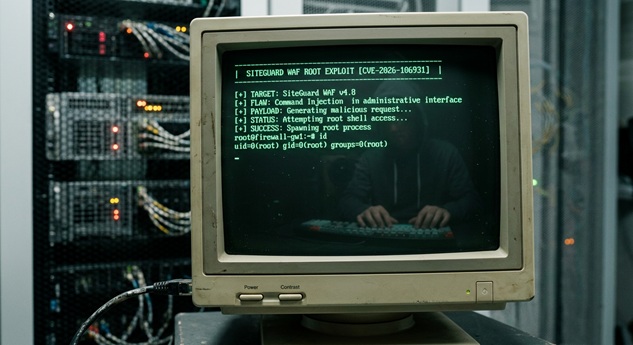
Attackers are actively exploiting a critical OS command injection vulnerability in the SiteGuard Server Edition web application firewall. The flaw, tracked as CVE-2026-106931, allows threat actors to execute commands with root or SYSTEM privileges on affected servers. SiteGuard is a leading Japanese WAF vendor protecting more than 1.5 million websites, with over 500,000 active WordPress plugin installations.
What Happened: SiteGuard WAF Command Injection Grants Root Access
On October 18, 2026, SiteGuard and Japan’s JPCERT/CC disclosed that attackers are actively abusing CVE-2026-106931. The vulnerability resides in the statistics feature of SiteGuard Server Edition, which is enabled by default on host-based WAF instances.
Consequently, successful exploitation gives attackers the highest level of access on the underlying server. Neither the vendor nor JPCERT/CC has disclosed the attacker identity, victim count, or attack methods at this time.
Technical Details of the SiteGuard WAF Vulnerability
CVE-2026-106931 is an OS command injection flaw in the statistics function of SiteGuard Server Edition. The vulnerability affects multiple versions and platforms.
The following product versions are vulnerable when the statistics function is active:
- SiteGuard Server Edition for Apache httpd, Nginx, and IIS (excluding FreeBSD): versions 2.20 and later, before 8.00 Update 5
- SiteGuard Server Edition for Apache httpd and Nginx on FreeBSD: versions 2.20 and later, before 7.00 Update 6
IIS editions from 3.10 through 4.00 Update 4 are not affected, according to JPCERT/CC advisory JVN88474777.
For example, an attacker who can reach the statistics endpoint may inject shell commands that execute with the privileges of the WAF process. On most installations, this process runs as root or SYSTEM.
Business and Operational Impact
The impact of CVE-2026-106931 is severe for any organization running vulnerable SiteGuard instances.
- Complete server compromise: Root or SYSTEM access allows attackers to control the entire server
- Data exfiltration: Attackers can read sensitive application data, databases, and configuration files
- Lateral movement: Compromised servers can become launch points for broader network intrusion
- Websites defaced or backdoored: With root access, attackers can modify web content or plant persistent backdoors
- Service disruption: Attackers may disable the WAF or take services offline
Moreover, the 500,000+ WordPress sites running the SiteGuard plugin may also be at risk if they use the Server Edition backend with statistics enabled.
Mitigation and Recommendations
SiteGuard has released patched versions and file replacements for installations that cannot be upgraded immediately.
Immediate Actions for Defenders
- Upgrade SiteGuard Server Edition to 8.00 Update 5 or later (or 7.00 Update 6 for FreeBSD)
- If upgrading is not immediately possible, apply the vendor’s patch that replaces statistics processing files
- Disable the statistics function as a temporary mitigation if it is not business-critical
- Preserve diagnostic information before patching — the vendor warns that remediation may erase attack traces
Detection and Hunting Guidance
Administrators should download and retain diagnostic information from the web management interface before applying updates. Furthermore, review server logs for suspicious command execution or unexpected processes spawned by the SiteGuard service account.
Vendor Communication Timeline
- September 29, 2026: Customers with direct support contacts notified privately
- October 18, 2026: Public disclosure via vendor alert and JPCERT/CC advisory
Bottom line: Patch immediately. CVE-2026-106931 is actively exploited and grants root access. The statistics function is enabled by default, so most installations are vulnerable unless administrators have explicitly disabled it.
Incident Summary
| CVE ID / Incident: | CVE-2026-106931 |
| Affected Systems: | SiteGuard Server Edition for Apache httpd, Nginx, IIS (non-FreeBSD) versions 2.20+ before 8.00 Update 5; Apache httpd and Nginx on FreeBSD versions 2.20+ before 7.00 Update 6 |
| Disclosure Date: | October 18, 2026 |
| Patch Status: | Available — 8.00 Update 5 / 7.00 Update 6 released; file replacement patches available for end-of-life versions |
| Severity: | Critical — active exploitation confirmed; root/SYSTEM privilege escalation |
| Vendor: | EG Secure / SiteGuard |
| Advisory: | JPCERT/CC JVN88474777 |
References
- SiteGuard Security Alert, “OS Command Injection Vulnerability in Statistics Function of SiteGuard Server Edition,” October 18, 2026, https://www.eg-secure.co.jp/siteguard/news/alert-202610-1, accessed October 18, 2026.
- JPCERT/CC, “JVN#88474777: OS Command Injection Vulnerability in SiteGuard Server Edition,” October 18, 2026, https://jvn.jp/en/jp/JVN88474777/index.html, accessed October 18, 2026.
- BleepingComputer, “Hackers exploit SiteGuard WAF flaw to run commands as admins,” October 18, 2026, https://www.bleepingcomputer.com/news/security/hackers-exploit-siteguard-waf-flaw-to-run-commands-as-system-root/, accessed October 18, 2026.