Unpatched AhsayCBS Flaws Exploited to Deploy Webshells and Mine Crypto
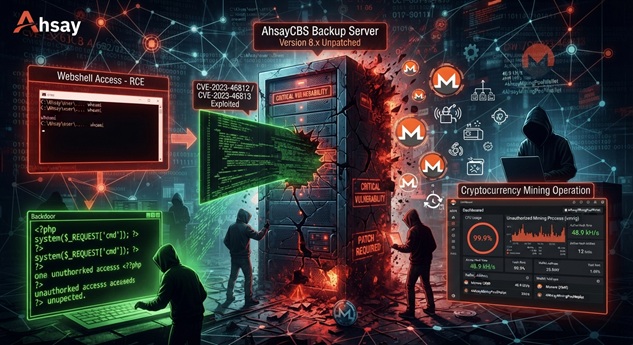
Threat actors are actively exploiting two unpatched vulnerabilities in the AhsayCBS backup management platform to deploy webshells and cryptocurrency miners on victim systems. The flaws, tracked as CVE-2026-105133 and CVE-2026-105134, affect the latest available version of the software and have already targeted at least five organizations.
What Happened: Attackers Chain AhsayCBS Flaws for Crypto Mining
On October 7, 2026, Huntress observed malicious activity exploiting AhsayCBS, a backup solution used by managed service providers and system integrators. The attackers chained an authentication bypass with a command injection flaw to gain unauthorized access.
Once inside, they performed reconnaissance, deployed JSP webshells, and installed the XMRig cryptocurrency miner disguised as a legitimate Microsoft Edge process. A PowerShell script was used to hide mining activity by stopping the service when Task Manager opened.
Technical Details of the AhsayCBS Vulnerabilities
The attack leverages two vulnerabilities that remain unpatched in AhsayCBS version 10.3.4:
- CVE-2026-105133: An authentication bypass vulnerability with a publicly available exploit.
- CVE-2026-105134: An OS command injection vulnerability allowing remote code execution.
Researchers initially believed the flaws were fixed in version 10.3.2. However, further investigation confirmed that version 10.3.4, the latest release, remains vulnerable.
Business and Operational Impact
The exploitation of these flaws poses significant risks to organizations relying on AhsayCBS for data protection:
- Data Integrity: Attackers can install backdoors, compromising backup integrity and recovery capabilities.
- Resource Theft: Cryptocurrency mining consumes CPU and GPU resources, degrading system performance.
- Lateral Movement: Webshells provide persistent access for further network exploitation.
- Supply Chain Risk: MSPs using AhsayCBS could inadvertently expose multiple downstream clients.
Mitigation and Recommendations
Huntress recommends immediate action to reduce exposure and eradicate threats:
- Restrict AhsayCBS management interface access to trusted IP addresses only.
- Investigate systems for signs of compromise, including unauthorized services and processes.
- If compromised, perform a full restore from a clean backup to remove potential backdoors.
- Apply patches immediately once AhsayCBS releases a fixed version.
Detection Guidance
Huntress has released four Sigma rules and indicators of compromise to aid detection. Key IoCs include:
- JSP webshells in web-accessible directories
- Service named
MicrosoftEdgeUpdateSvcrunningmsedge.exe - PowerShell script
Taskgmr.ps1terminating Task Manager
Bottom line: Until an official patch is available, restrict management access, hunt for IoCs, and assume compromise requires full restoration.
Incident Summary
| CVE IDs: | CVE-2026-105133, CVE-2026-105134 |
| Affected Product: | AhsayCBS backup management platform (up to version 10.3.4) |
| Disclosure Date: | October 9, 2026 |
| Exploitation: | Active in the wild since October 7, 2026 |
| Patch Status: | No patch available as of October 10, 2026 |
References
- Huntress. “AhsayCBS Flaws Exploited to Deploy Webshells and Mine Crypto,” October 9, 2026. https://www.huntress.com/blog/ahsaycbs-flaws-exploit
- BleepingComputer. “Unpatched AhsayCBS flaws exploited to deploy webshells, mine crypto,” October 9, 2026. https://www.bleepingcomputer.com/news/security/unpatched-ahsaycbs-flaws-exploited-to-deploy-webshells-mine-crypto/
- NVD. “CVE-2026-105133 Detail,” October 2026. https://nvd.nist.gov/vuln/detail/cve-2026-105133
- NVD. “CVE-2026-105134 Detail,” October 2026. https://nvd.nist.gov/vuln/detail/cve-2026-105134