Fandango Data Breach Card Skimmer Steals Payment Details
Fandango Media has notified customers of a data breach that exposed payment card details entered on its checkout pages between October 8 and October 11, 2026. The ticket seller’s investigation found that card skimmer code injected into the Fandango checkout page intercepted payment card data and sent it to attackers. This breach affects anyone who bought movie tickets online through the official Fandango website or app during the four-day exposure window.
What Happened: Fandango Checkout Page Hack Steals Payment Card Details
Fandango Media, the parent company of the Fandango ticketing platform and Rotten Tomatoes, disclosed on November 16 that an unauthorized party accessed payment card information tied to certain transactions on its checkout page. The exposure window ran from October 8 through October 11, 2026.
The company determined on October 30, 2026 that customer information may have been affected. It then investigated with outside cybersecurity specialists and confirmed that card skimmer code had been injected into the checkout page. Fandango has since fixed the issue on its checkout page.
Consequently, the exposed data set is narrow but sensitive. It does not include names, government-issued identification, Social Security numbers, or Fandango account information. However, payment card numbers, card verification values, expiration dates, billing ZIP codes, and email addresses were exposed. That combination is enough to fuel unauthorized online purchases and card-present fraud attempts.
Technical Details of the Fandango Card Skimmer Attack
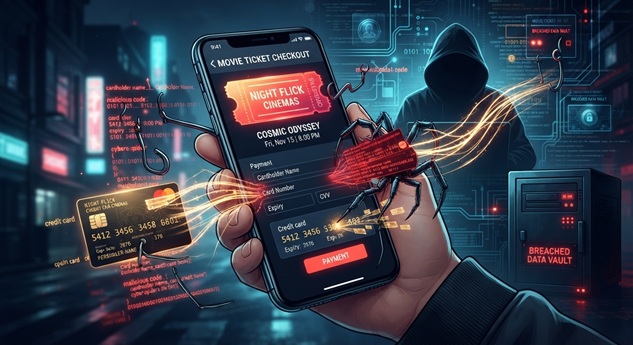
The attack relied on a classic e-commerce technique. Attackers injected malicious script code into the checkout page itself. When a customer typed payment card details into the form, the skimmer read the fields and transmitted the values to infrastructure controlled by the attackers.
Because the skimmer operated inside the genuine Fandango checkout flow, customers saw an ordinary, HTTPS-protected transaction. There was no phishing domain to spot and no obvious sign of tampering at the point of entry. The interception happened after the page was already trusted by the customer and the browser.
- Attack vector: JavaScript card skimmer injected into the legitimate Fandango checkout page
- Exposure window: October 8-11, 2026 (four days)
- Compromise discovered: October 30, 2026
- Public disclosure: November 16, 2026
- Platform affected: Fandango checkout pages for purchases made on the official website and app
- Remediation: Checkout page issue fixed as of disclosure
Importantly, Fandango stated it is currently unaware of any cases of fraud using the stolen data. The company also has not published a count of affected customers. BleepingComputer has asked the company for that figure and says the story will be updated once a response arrives.
Business and Operational Impact
Fandango is a major United States online movie ticketing platform. It sells tickets for roughly 31,000 screens across the country, including AMC, Regal, and Cinemark locations, and it also operates the Rotten Tomatoes review site. A compromise at the checkout layer therefore reaches a large consumer base in a single stroke.
- Financial fraud risk: Exposed card numbers, CVVs, expiration dates, and billing ZIP codes can be replayed for unauthorized purchases.
- Phishing leverage: Compromised email addresses let attackers build convincing targeted phishing and fake chargeback lures.
- Merchant fraud: Chargebacks and dispute costs fall on the merchant, and Fandango may absorb reputational damage.
- Regulatory exposure: Notification obligations across multiple jurisdictions depend on the affected customer count, which remains undisclosed.
- No account takeover: Because Fandango logins were not exposed, the incident is contained to payment data rather than customer accounts.
To reduce risk for affected customers, Fandango is offering two years of free IDX credit monitoring, dark web monitoring, and identity theft recovery services. The enrollment deadline is February 13, 2027.
Mitigation and Recommendations
Fandango has fixed the checkout page, but customers who transacted during the window still carry the exposure. Defenders and consumers should treat the four-day window as a trigger for proactive action rather than waiting for confirmed fraud to appear.
Immediate Actions for Affected Customers
- Review bank and credit card statements closely for charges that you did not authorize, and dispute them with your card issuer promptly.
- Consider replacing the exposed card. A new number makes the stolen card data useless to attackers.
- Place a credit freeze or fraud alert with the credit bureaus if you used the affected card anywhere else.
- Enroll in the free IDX credit and dark web monitoring offered by Fandango before the February 13, 2027 deadline.
- Use one-time virtual card numbers for online purchases where your bank offers them.
Guidance for E-Commerce and Security Teams
The Fandango incident shows that trusted checkout paths remain attractive attack surfaces. First, monitor checkout page JavaScript for unauthorized script injection and enforce a strict Content Security Policy on payment pages. Second, use browser-side integrity and file integrity monitoring to catch skimmer code as it lands. Third, verify payment page code integrity continuously rather than only at deploy time, because skimmers frequently reappear after updates. Finally, treat e-commerce third-party and marketing scripts as first-class code with the same review rigor as first-party checkout code.
Bottom line: Fandango has contained the checkout skimmer and reports no confirmed misuse, yet four days of exposed card data remain the real risk. Affected customers should monitor and rotate their payment cards now, and every online retailer should assume its checkout page will be targeted again.
Incident Summary
| Incident: | Fandango Media checkout page payment card skimmer (no CVE assigned) |
| Affected Systems: | Fandango online movie ticketing checkout pages (website and app) |
| Exposure Window: | October 8-11, 2026 |
| Discovery Date: | October 30, 2026 |
| Disclosure Date: | November 16, 2026 |
| Data Exposed: | Payment card number, CVV, expiration date, billing ZIP, email address |
| Data Not Exposed: | Names, government ID, SSN, Fandango account information |
| Patch Status: | Fixed as of disclosure; no CVE identifiers assigned |
References
- Bill Toulas, “Fandango says hackers stole payment card details from checkout pages,” BleepingComputer, November 16, 2026, https://www.bleepingcomputer.com/news/security/fandango-says-hackers-stole-payment-card-details-from-checkout-pages/ (accessed November 16, 2026).
- Fandango Media, “Notice of Data Security Incident,” Fandango customer notification, https://www.documentcloud.org/documents/28911829-fandangomedia-breachnotification/ (accessed November 16, 2026).
- Fandango Media, “Fandango Media Reports a Payment Card Data Incident,” Fandango Security Information, https://www.fandango.com/policies/security-information/ (accessed November 16, 2026).
- Lawrence Abrams, “Hackers steal payment card data from Fandango checkout pages,” BleepingComputer, November 16, 2026, https://www.bleepingcomputer.com/news/security/fandango-says-hackers-stole-payment-card-details-from-checkout-pages/ (accessed November 16, 2026).