Optimizely Supply Chain Attack Infects CNN, Fox News, BBC, and 175 Other Sites
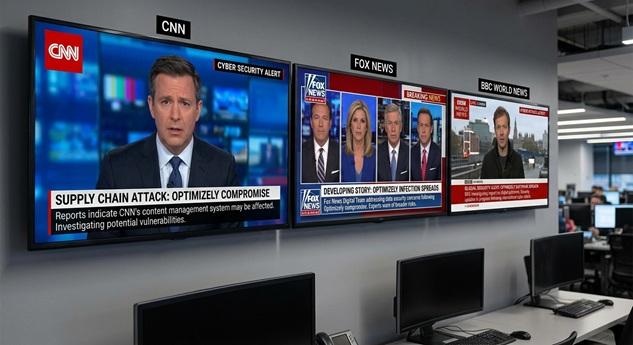
Attackers compromised Optimizely, a widely used digital experience platform, to inject malicious JavaScript into customer projects. Consequently, visitors to major websites including CNN, Fox News, BBC, Salesforce, Zoom, and GitLab were exposed to malware designed to steal cryptocurrency and payment card details. Moreover, the attack delivered iOS exploit kits targeting iPhones and iPads.
What Happened: Optimizely Supply Chain Attack Infects 178 Organizations
On November 16, 2026, security researcher Scott Helme identified 188 infected Optimizely JavaScript files across 178 organizations. The attackers exploited a vulnerability in Optimizely’s Experimentation account signup flow to inject malicious code into customer projects.
Furthermore, the malicious script loaded on high-traffic websites including Zoom, KLM, GitLab, BBC, CNN, Salesforce, Fox News, American Eagle, Air France, Change.org, and UNICEF USA. Therefore, millions of website visitors may have been exposed to the malware during the attack window.
Optimizely confirmed the incident and stated it had blocked the vulnerable path, deployed a fix, removed injected code, ended active sessions, revoked tokens, and reset access for affected accounts. Additionally, the company blocked any code delivery through Cloudflare as a precaution.
Technical Details of the Optimizely Experimentation Exploit
The attackers exploited a vulnerability in Optimizely’s Experimentation account signup flow. They used this access to add malicious JavaScript to customer projects, which then loaded an external payload from https://1688360[.]cc/track.js.
The injected code employed multiple loading techniques to evade detection:
- Direct URL references: Some files loaded the malicious script using the raw URL
- Base64 encoding: Other files used JavaScript’s
atob()function to decode the payload URL - Embedded fallback: A variation contained an embedded copy of the malicious code to execute if the remote script was blocked
Security researcher Scott Helme reported that the earliest observed injection occurred in the early morning of November 16. However, the total exposure window remains unclear as the investigation continues.
Malicious Payload Capabilities
An analysis of the track.js file revealed multiple attack capabilities:
- Cryptocurrency hijacking: Monitors webpages for cryptocurrency wallet addresses and replaces them with attacker-controlled addresses to steal transfers
- Payment card skimming: Searches for credit card numbers, expiration dates, and security codes entered into webpages, then transmits captured data to the attacker’s server
- iOS exploit delivery: Loads additional malicious JavaScript targeting iPhones and iPads using the Coruna and DarkSword exploit kits
- Data collection: Harvests browser cookies, webpage URLs, and screenshots for exfiltration
Cryptocurrency Theft Observed
Helme’s investigation found that cryptocurrency wallets embedded in the malicious script had received approximately $7,000 in transactions as of November 16. However, some wallets were active before the attack, making it difficult to determine the total stolen during this campaign.
| Cryptocurrency | Wallet Address | Amount Received |
| Bitcoin (BTC) | 19g9rZcPeiz8rUvyWpTRyXXhPnjsWrc3kW | ~$5,380 |
| Litecoin (LTC) | ltc1q3wp7g6ds0ggg6fl6kncpa4sepn0q3qfacgred5 | ~$762 |
| TRON (TRX/USDT) | THvs6p56XkUiMkJeSc51cAP64u2RsTYqxa | ~$719 |
| Ethereum (ETH) | 0xC4026b06D82b0F0B363eda0642D61CfbDc17884e | ~$100 |
Business and Operational Impact
The Optimizely supply chain attack carries significant consequences for affected organizations and their users. Supply chain compromises are particularly dangerous because they exploit trusted relationships between vendors and customers.
- Brand reputation damage: Major brands including CNN, Fox News, BBC, and Salesforce unknowingly served malware to visitors
- Cryptocurrency theft: Users who copied wallet addresses from affected sites may have sent funds to attacker-controlled addresses
- Payment card exposure: Shoppers who entered card details on affected websites may have had their information skimmed
- iOS device compromise: iPhone and iPad users visiting affected sites risked exploitation through Coruna and DarkSword exploit kits
- Session hijacking: Stolen cookies could enable unauthorized access to user accounts on affected platforms
- Regulatory scrutiny: Affected organizations may face questions about third-party risk management and supply chain security
Mitigation and Recommendations
Immediate Actions for Website Operators Using Optimizely
- Verify that Optimizely scripts on your websites are clean and have not been modified
- Review all Optimizely projects for unauthorized code injections or configuration changes
- Reset Optimizely account credentials and review access logs for suspicious activity
- Implement Subresource Integrity (SRI) tags on third-party scripts to detect unauthorized modifications
- Monitor website traffic for unexpected outbound connections to unknown domains
Immediate Actions for End Users
- Review cryptocurrency transfers made on November 16 to verify wallet addresses were not replaced
- Monitor credit card and bank statements for unauthorized transactions
- Update iPhones and iPads to the latest iOS or iPadOS version to patch vulnerabilities targeted by Coruna and DarkSword
- Change passwords for accounts accessed while visiting affected websites
- Clear browser cookies and cache, particularly for affected domains
Long-Term Supply Chain Security Recommendations
- Implement Content Security Policy (CSP) headers to restrict which domains can load scripts on your websites
- Use Subresource Integrity (SRI) hashes for all third-party JavaScript to detect tampering
- Conduct regular security assessments of third-party vendors and their code delivery mechanisms
- Monitor third-party scripts using external integrity checking services
- Establish incident response procedures specifically for supply chain compromises
Bottom line: Supply chain attacks exploit the trust users place in legitimate websites. Organizations must verify the integrity of third-party scripts and implement defense-in-depth measures like CSP and SRI to prevent similar incidents.
Incident Summary
| Incident: | Optimizely Experimentation Platform Supply Chain Attack |
| Affected Systems: | Optimizely Experimentation platform; 178 customer organizations including CNN, Fox News, BBC, Salesforce, Zoom, GitLab, and others |
| Disclosure Date: | November 16, 2026 |
| Attack Vector: | Vulnerability in Optimizely Experimentation account signup flow |
| Malicious Capabilities: | Cryptocurrency hijacking, payment card skimming, iOS exploit delivery, data collection |
| Patch Status: | Optimizely deployed fix, removed injected code, and revoked affected tokens |
| Estimated Theft: | Approximately $7,000 in cryptocurrency observed as of November 16, 2026 |
References
- Scott Helme, Report URI Blog, “World’s Largest Brands Infected With Malware via Optimizely,” November 16, 2026, https://blog.report-uri.com/worlds-largest-brands-infected-with-malware-via-optimizely/
- BleepingComputer, “Optimizely hack infected CNN, Fox News, BBC, Salesforce sites with malware,” November 16, 2026, https://www.bleepingcomputer.com/news/security/optimizely-supply-chain-attack-delivers-malware-to-cnn-fox-news-bbc-salesforce-sites/
- BleepingComputer, “Coruna iOS Exploit Framework Linked to Triangulation Attacks,” https://www.bleepingcomputer.com/news/security/coruna-ios-exploit-framework-linked-to-triangulation-attacks/
- BleepingComputer, “New DarkSword iOS Exploit Used in Infostealer Attack on iPhones,” https://www.bleepingcomputer.com/news/security/new-darksword-ios-exploit-used-in-infostealer-attack-on-iphones/