

N-able 4EverAble2Shell Zero-Day Actively Exploited
November 14, 2026 The N-able 4EverAble2Shell zero-day is being actively exploited in the wild, chaining Apache Axis CVE-2026-90436 with an N-central privilege escalation flaw to gain root access on remote monitoring and management servers. Security…
Red Hat Quay CVE Lets Attackers Overwrite All Private Containers
November 14, 2026 A critical vulnerability in Red Hat Quay container registry allows attackers to read and overwrite private container images across every repository. This flaw, tracked as CVE-2026-123710, carries a CVSS score of 9.8 and has existed…
Unreal IRCd CVE-2026-114713 Zero-Day Grants Server Authority
November 14, 2026 The UnrealIRCd CVE-2026-114713 zero-day is a critical command injection flaw in the labeled-response module that lets any ordinary IRC user execute commands with full server authority. CISA added the flaw to its Known Exploited…
Check Point CVE Zero-Day Grants Root Access on Firewalls and Management Servers
November 14, 2026 Check Point Software has released emergency hotfixes for CVE-2026-123039, a high-severity local privilege escalation flaw that threat actors have actively exploited since late October to gain root privileges on enterprise firewalls and…
CryptoBilis Supply Chain Attack Steals Recovery Phrases via Cellular Networks
November 13, 2026 Cryptocurrency hardware wallet maker Trezor confirmed that malicious hardware implants in Safe 5 devices sold by Southeast Asian reseller CryptoBilis were designed to steal wallet recovery phrases and transmit them to attackers over…
22-Year-Old PostgreSQL Bug Grants Authenticated RCE
November 13, 2026 Researchers have disclosed CVE-2026-6460, a 22-year-old type confusion flaw in PostgreSQL that can allow an authenticated database user to achieve remote code execution. The vulnerability was patched on November 9, 2026, alongside 51…
Windows SignDrop Zero-Day Grants SYSTEM Privileges and Bypasses Any Antivirus
November 13, 2026 Security researcher Abdelhamid Naceri (Nightmare Eclipse) has released a new Windows zero-day exploit called SignDrop that can grant attackers SYSTEM privileges on roughly 80% of Windows installations. The flaw exists in the Common Log…
Notion AI Chat Transcripts Exposed in Fireworks AI Third-Party Data Breach
November 12, 2026 Notion disclosed that a security breach at its AI infrastructure provider, Fireworks AI, exposed Notion AI chat transcripts in a small number of workspaces. The incident highlights growing third-party supply chain risks in the…
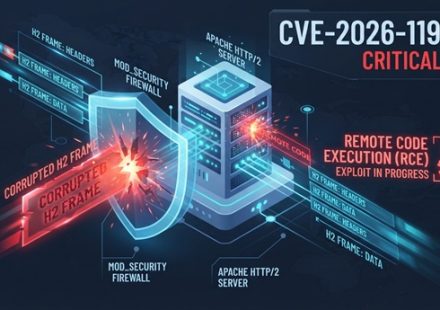
Critical Apache HTTP/2 CVE Enables Unauthenticated Remote Code Execution
November 12, 2026 A critical vulnerability in Apache HTTP Server’s HTTP/2 module allows unauthenticated remote attackers to execute arbitrary code on affected systems. The flaw, tracked as CVE-2026-119618, carries a CVSS score of 9.8 out of 10 and…
GPUStack CVE Critical Authentication Bypass Enables Unauthenticated Admin Takeover
November 12, 2026 GPUStack CVE-2026-102895 is a critical authentication bypass vulnerability. It enables unauthenticated attackers to gain full administrative access to GPUStack deployments. Furthermore, active exploitation has been confirmed in the…