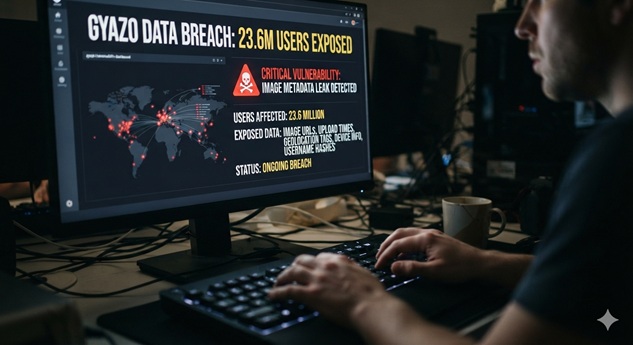
The Gyazo image-sharing platform has confirmed a massive data breach after attackers exploited a server vulnerability. Consequently, approximately 23.6 million user records and 490 million image metadata entries were exposed. The incident has forced the company to take its popular screenshot and screen-recording service offline while it investigates the full scope of the damage.
What Happened: Gyazo Data Breach Hits 23.6 Million Users
Helpfeel Inc., the Kyoto-based operator of Gyazo, disclosed the breach on September 16, 2026. Moreover, the company confirmed that attackers exploited a vulnerability in Gyazo’s image upload server to gain unauthorized access.
The incident occurred on September 11, 2026. Helpfeel detected suspicious activity that same evening and began an immediate investigation. Furthermore, by the early hours of September 12, the company had blocked the identified access routes and terminated unauthorized connections.
However, the data had already been stolen. The investigation confirmed that the attackers accessed Gyazo’s database and extracted both user information and metadata associated with uploaded images. Therefore, Helpfeel took the platform offline as a preventive measure.
Currently, Gyazo remains suspended for maintenance. The company has not provided a timeline for full restoration of service.
Technical Details of the Gyazo Server Vulnerability
The attackers exploited a vulnerability in Gyazo’s image upload server. This flaw allowed them to execute arbitrary commands and gain unauthorized access to internal systems. In addition, the breach exposed two distinct categories of data: user information and image metadata.
The exposed user records total approximately 23.62 million. The types of data vary by user and may include:
- Names and nicknames
- Email addresses
- Password hashes
- User IDs and device IDs
- Login session IDs
- X (formerly Twitter) integration tokens
- Google SSO email addresses
- Profile information and language preferences
- Subscription plans and billing status
- Usage statistics
Moreover, the breach exposed approximately 490 million image metadata records. Most of these relate to images uploaded before January 2019. The image metadata includes:
- Image IDs used to construct image URLs
- Source IP addresses used for uploads
- User-Agent strings
- EXIF location data
- OCR-extracted text from images
- Image titles and source URLs
- Hashed passphrases for private images
The image IDs are particularly concerning. They can potentially be used to construct direct URLs to view images without authorization. For this reason, Helpfeel has temporarily disabled viewing of affected images.
Additionally, the attackers obtained a list identifying private images. The company cannot rule out that some private images were viewed by unauthorized parties.
Business and Operational Impact
The Gyazo data breach carries significant consequences for users, the company, and the broader cybersecurity landscape.
User impact:
- 23.6 million users face potential credential stuffing attacks due to exposed password hashes
- Session IDs and integration tokens could enable account takeover
- EXIF location data in metadata may expose users’ physical locations
- OCR text could reveal sensitive content captured in screenshots
- Private image passphrases, though hashed, may be crackable
Business impact:
- Gyazo service remains offline with no restoration timeline
- Helpfeel must notify affected users and regulatory authorities
- Reputational damage to a platform with 23 million claimed users
- 3.1 billion media items on the platform are now under scrutiny
- Other Helpfeel services (Cosense) require investigation and reassurance
Compliance impact:
- Japan’s Act on the Protection of Personal Information (APPI) notification requirements
- Potential GDPR implications for European users
- Cross-border data protection obligations for global user base
Mitigation and Recommendations
Immediate Actions for Gyazo Users
- Change your Gyazo password immediately. Also change the same password on any other service where you reused it.
- Revoke X (Twitter) and Google SSO connections to Gyazo. Re-authorize only after the service is fully restored.
- Review your Gyazo uploads for sensitive content. Consider removing or making private any screenshots containing personal, financial, or corporate data.
- Monitor for suspicious emails, texts, or phishing attempts referencing Gyazo. Attackers often use breach data for targeted social engineering.
- Enable multi-factor authentication on all accounts where available. This prevents account takeover even if credentials are exposed.
Actions for Security Teams
- Check corporate networks for Gyazo usage. Many employees use screenshot tools without IT approval.
- Review uploaded image metadata policies. Screenshot tools often embed extensive EXIF and OCR data.
- Add Gyazo-related indicators to threat intelligence monitoring. Watch for credential stuffing campaigns using exposed hashes.
- Audit third-party SaaS tools for similar server-side vulnerabilities. Image upload endpoints are common attack surfaces.
Bottom line: The Gyazo breach demonstrates how a single server vulnerability can expose not just user credentials but the actual content users captured. Screenshot and screen-recording tools handle inherently sensitive data, making their security posture critical. Users should treat these services with the same caution as password managers and financial apps.
Incident Summary
| Incident: | Gyazo Data Breach |
| Operator: | Helpfeel Inc. (Kyoto, Japan) |
| Platform: | Gyazo image-sharing and screenshot service |
| Attack Date: | September 11, 2026 |
| Disclosure Date: | September 16, 2026 |
| User Records Exposed: | Approximately 23.62 million |
| Image Metadata Exposed: | Approximately 490 million records |
| Attack Vector: | Server vulnerability in image upload server |
| Data Types: | Password hashes, emails, session IDs, tokens, EXIF data, OCR text, image metadata |
| Payment Data: | No credit card or payment information exposed |
| Status: | Service offline; investigation ongoing; authorities contacted |
References
- Helpfeel Inc., “Notice and Apology Regarding a Data Breach Resulting from Unauthorized Access to Gyazo,” September 16, 2026, https://corp.helpfeel.com/en/news/news-20260916, accessed September 19, 2026.
- BleepingComputer, “Gyazo server flaw exploited to steal 23.6 million user records,” September 18, 2026, https://www.bleepingcomputer.com/news/security/gyazo-server-flaw-exploited-to-steal-236-million-user-records/, accessed September 19, 2026.
- Gyazo (@gyazo_ja), X (formerly Twitter) post regarding service suspension, September 2026, http://x.com/gyazo_ja/status/2100825600835694640, accessed September 19, 2026.
SEO Information
Primary Keyword: Gyazo data breach
SEO Title: Gyazo Data Breach: 23.6M Users and Image Metadata Exposed
Meta Description: Gyazo image-sharing platform confirms data breach exposing 23.6 million user records and 490 million image metadata files. Learn what data was stolen and how to protect yourself.
Focus Keyphrase: Gyazo data breach