Microsoft has patched CVE-2026-124194, an actively exploited zero-day vulnerability in Microsoft Outlook that silently exposes NTLMv2 authentication hashes to remote attackers. Also added to CISA’s Known Exploited Vulnerabilities catalog on November 10, this spoofing flaw requires only a single click on a malicious message file to harvest credentials that can unlock enterprise accounts.
What Happened: Microsoft Outlook CVE-2026-124194 Zero-Day Exposes NTLM Hashes
On November 10, 2026, Microsoft released its November Patch Tuesday update bundle containing fixes for 1,259 vulnerabilities. However, one flaw stood out from the rest: CVE-2026-124194, a Moderate-severity spoofing vulnerability in Microsoft Outlook with a CVSS score of 6.5 that Microsoft confirmed is already under active exploitation in the wild.
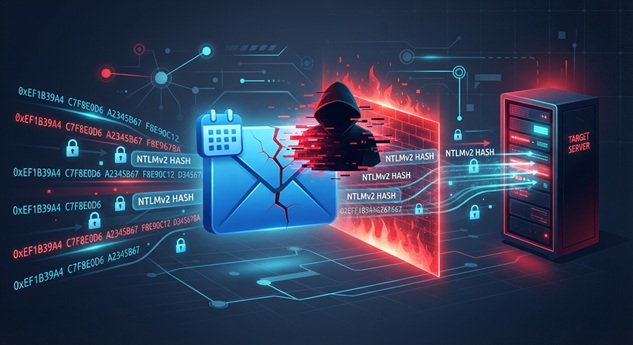
The vulnerability allows an unauthenticated attacker to send a specially crafted Outlook message file to a target. When the victim opens the file, Outlook initiates a connection to an attacker-controlled network location without displaying its usual external-content warning. Consequently, Windows can automatically transmit the user’s NTLMv2 authentication hash to the remote server.
CISA responded swiftly by adding CVE-2026-124194 to its Known Exploited Vulnerabilities catalog on the same day. Federal agencies must now apply the fix by November 24, 2026, under Binding Operational Directive 26-04. However, the exploit is not limited to government networks; any organization running affected Outlook versions remains at risk.
Technical Details of the Outlook Spoofing Vulnerability
CVE-2026-124194 is classified under CWE-356: Product UI Does Not Warn User of Unsafe Actions. In practical terms, Outlook fails to warn users before the application performs a potentially dangerous external-content action.
How the Attack Works
- An attacker crafts a malicious Outlook message file embedded with a reference to an attacker-controlled network resource.
- The attacker delivers this file via email, file-sharing services, or other social-engineering channels.
- The target opens the message file in a vulnerable version of Outlook.
- Outlook connects to the remote resource without displaying the external-content warning users normally expect.
- Windows automatically attempts NTLM authentication, sending the user’s NTLMv2 hash to the attacker’s server.
Key Attack Constraints
- The Preview Pane is not an attack vector; the victim must actively open the message file.
- Network connectivity is required for the outbound connection.
- The attacker does not need an account on the victim’s system or Microsoft 365 tenant.
Affected Products
| Product | Affected Versions | Fixed Version |
| Microsoft 365 Apps for Enterprise | Vulnerable releases before November 2026 update | Current Office Security Release |
| Microsoft Office LTSC 2021 | Earlier than 16.0.14334.21048 | 16.0.14334.21048 or later |
| Microsoft Office LTSC 2024 | Earlier than 16.0.17932.21140 | 16.0.17932.21140 or later |
Both 32-bit and x64 installations are affected. The flaw was discovered by researcher “nono” and Benoît Sevens of Anthropic, who reportedly used Claude AI during the research process.
Business and Operational Impact
Although CVE-2026-124194 carries a CVSS score of only 6.5, operational risk is significantly higher because exploitation is already occurring in the wild. A stolen NTLMv2 hash is not the user’s plaintext password, but it still opens several dangerous attack paths:
- Credential replay and impersonation: Attackers can use captured hashes to authenticate as the victim against services that accept NTLM.
- Offline password cracking: Weak passwords can be recovered from hashes through brute-force or dictionary attacks.
- Lateral movement: Compromised credentials can unlock file shares, remote systems, VPN gateways, and cloud services.
- Privilege escalation: If the affected user holds administrative rights, the attacker gains equivalent access.
- Reputational and compliance costs: Active exploitation triggers incident-response costs, audit obligations, and potential regulatory penalties.
Microsoft has not disclosed the identity of the threat actors, campaign scale, victim organizations, or whether stolen credentials have already been abused. Nevertheless, the confirmed exploitation status makes this vulnerability a priority for immediate remediation.
Mitigation and Recommendations
Immediate Actions for Defenders
- Install November 2026 Office security updates immediately. Verify that all affected Outlook installations are running the fixed builds listed above.
- Block outbound SMB traffic to the internet. Microsoft explicitly recommends preventing SMB on TCP port 445 from leaving the corporate network unless there is a specific operational requirement.
- Audit and restrict outgoing NTLM authentication. Use the Windows policy “Network security: Restrict NTLM: Outgoing NTLM traffic to remote servers” in audit mode first to identify legitimate dependencies.
- Monitor for suspicious behavior. Correlate Outlook activity with unexpected outbound SMB connections, NTLM authentication attempts to external systems, and subsequent identity abuse.
- Educate users. Warn employees against opening unsolicited Outlook message files or attachments from untrusted sources.
Investigating Potential Compromise
If suspicious exploitation is suspected, merely installing the patch is not sufficient. Security teams should:
- Identify the affected identity and review authentication activity after the suspected message file was opened.
- Look for unusual SMB connections, remote logons, lateral movement, and file-share access.
- Reset passwords and revoke active sessions where evidence suggests authentication information was exposed.
- Preserve endpoint, proxy, firewall, email, and identity logs before remediation to reconstruct the attack chain.
Bottom line: CVE-2026-124194 proves that even Moderate CVSS scores can carry severe real-world consequences when active exploitation is confirmed. Patch Outlook now, block outbound SMB, and hunt for signs of credential compromise before attackers use stolen hashes to walk deeper into your network.
Incident Summary
| CVE ID / Incident: | CVE-2026-124194 |
| Affected Systems: | Microsoft 365 Apps for Enterprise, Office LTSC 2021, Office LTSC 2024 (32-bit and x64) |
| Disclosure Date: | November 10, 2026 (Patch Tuesday) |
| Patch Status: | Fixed in November 2026 Office security updates |
| CVSS Score: | 6.5 (Moderate) |
| CISA KEV Added: | November 10, 2026 |
| Federal Patch Deadline: | November 24, 2026 |
| Exploitation Status: | Actively exploited in the wild |
References
- Microsoft Security Response Center, “November 2026 Security Update Release Notes,” November 10, 2026, https://msrc.microsoft.com/update-guide/releaseNote/2026-Nov, accessed November 12, 2026.
- Microsoft, “CVE-2026-124194 Security Update Guide,” November 10, 2026, https://msrc.microsoft.com/update-guide/vulnerability/CVE-2026-124194, accessed November 12, 2026.
- U.S. Cybersecurity and Infrastructure Security Agency, “CISA Adds Six Known Exploited Vulnerabilities to Catalog,” November 10, 2026, https://www.cisa.gov/news-events/alerts/2026/11/10/cisa-adds-six-known-exploited-vulnerabilities-catalog, accessed November 12, 2026.
- The Hacker News, “Microsoft Patches 1,259 Flaws, Including Exploited Outlook Bug That May Expose NTLMv2 Hashes,” November 11, 2026, https://thehackernews.com/2026/11/microsoft-patches-1259-flaws-including.html, accessed November 12, 2026.
- SOC Prime, “CVE-2026-124194: Microsoft Outlook Zero-Day Exploited to Steal NTLM Hashes,” November 11, 2026, https://socprime.com/blog/cve-2026-124194-microsoft-outlook-zero-day-exploited-to-steal-ntlm-hashes/, accessed November 12, 2026.