NoisyTCP Linux Kernel Flaw CVE Crashes Servers
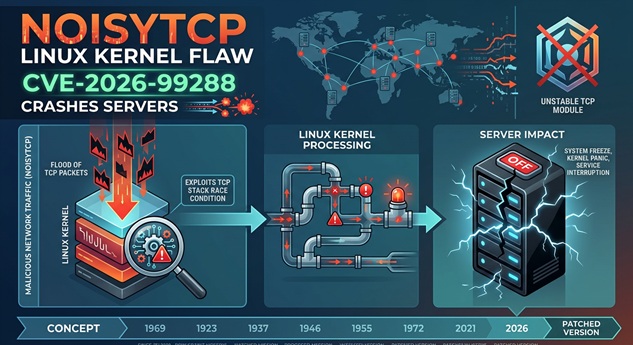
The NoisyTCP vulnerability (CVE-2026-99288) is an 11-year-old Linux kernel flaw that lets unauthenticated attackers crash nearly every Linux server running Nginx, Apache, or SSH with default settings. Security researcher Hyunwoo Kim disclosed the pre-authenticated remote denial-of-service bug, and a fix is already merged into the mainline kernel.
What Happened: NoisyTCP Flaw Crashes Linux Servers Remotely
Hyunwoo Kim, a well-known Linux kernel researcher, published details on November 16, 2026 about a vulnerability he dubbed NoisyTCP. The bug is tracked as CVE-2026-99288 and carries a CVE (Common Vulnerabilities and Exposures) identification record in the National Vulnerability Database. It affects almost every mainstream Linux distribution because the flaw lives in the kernel’s core TCP networking subsystem.
Unlike a typical remote code execution bug, NoisyTCP only allows denial of service. When triggered, the kernel panics and the entire host goes down, taking every service on it offline. Kim stressed that attackers cannot alter data or execute arbitrary code, but a full crash of a production host is still a serious operational event.
Consequently, the timing matters for defenders. A patch for CVE-2026-99288 merged into the mainline Linux kernel roughly two weeks ago, and distribution packages are already shipping fixes. However, the disclosure arrived with no known working exploit in the wild, so administrators have a narrow window to patch before scanners pick up the technique.
Technical Details of the NoisyTCP Vulnerability
NoisyTCP is a NULL pointer dereference (CWE-476) triggered by a race condition during lockless socket lookups in the Linux kernel. Recycled socket memory can be accessed before it is properly initialized and hashed. Red Hat’s security team explained the flaw as follows: an attacker who generates network traffic that drives socket reuse can trigger the dereference and crash the kernel.
Because the condition is pre-authentication, no valid session or credential is needed. However, the exploit path is narrow, so hitting a quiet bare-metal server can take considerable time.
How the Race Condition Is Triggered
The researcher documented a specific set of technical requirements for exploitation. All of the following must hold:
- A stale ehash lookup must run concurrently with the freeing and reallocation of an existing request socket.
- The concurrent work must happen in different RX (receive queue) contexts.
- Packet processing must be spread across two or more RX queues, or RPS must distribute packets across multiple CPUs.
- IPv4 fragments and regular TCP packets must differ in receive hash to force the split across queues.
Servers with a single RX queue and no RPS are far harder to attack. The bug also requires an active TCP workload, so idle hosts that never receive inbound connections present a much smaller target.
Business and Operational Impact
A single packet sequence can take a server offline without warning. Because NoisyTCP requires no credentials and no prior access, it fits the profile of a cheap, high-volume denial-of-service tool aimed at exposed infrastructure.
- Availability risk: Nginx, Apache, and SSH services on default Linux configurations are directly in scope. A kernel panic ends all workloads on the host.
- Low attacker cost: No authentication, no malware, and no foothold are needed. Attack traffic can be generated from commodity infrastructure.
- Downstream blast radius: Crashing a host that runs databases, CI runners, or virtualisation hypervisors disrupts more than the exposed web service.
- Insurance and compliance: Extended unplanned outages can trigger availability clauses in contracts and complicate post-incident reporting.
- Detection difficulty: A clean kernel panic can be misattributed to hardware failure or an unrelated bug without careful triage of preceding network traffic.
Mitigation and Recommendations
Because CVE-2026-99288 already has an upstream patch, the fix is straightforward for organisations that can patch quickly. The harder part is covering hosts that cannot be updated immediately.
Immediate Actions for Defenders
- Patch the kernel. Update to a distribution release that includes the NoisyTCP fix and reboot affected hosts. A mainline commit is already available in the Linux kernel tree.
- Disable SYN cookies as a temporary measure. This removes the SYN cookie handling timing window the exploit relies on. Note that this reduces protection against SYN flood attacks, so use it only as a short bridge to patching.
- Serialise to a single RX queue. Where possible, pin packet processing to one receive queue or disable RPS distribution across CPUs. This blocks the concurrency requirement for exploitation.
- Restrict TCP exposure. Use host firewalls, security groups, or load balancers to limit direct TCP access to Nginx, Apache, and SSH from untrusted networks.
- Watch for crash and traffic anomalies. Alert on kernel panic logs, unexpected reboots, and unusual inbound SYN volume or fragmented IPv4 traffic.
Long-Term Recommendations
Organizations should inventory which hosts run internet-facing TCP workloads and verify kernel versions against their distribution’s advisory feed. In addition, keep the emergency patch cycle short for kernel-level denial-of-service issues, since these bugs spread quickly once public proof-of-concept material appears. Furthermore, consider upstream rate limiting and SYN flood protection at the edge so that even unpatched hosts are shielded. Finally, document the NoisyTCP mitigation steps in your incident response runbook so operators can act without delay.
Bottom line: NoisyTCP is a remote crash bug with no fix complexity and no authentication barrier. Patch the kernel now, disable SYN cookies and single-queue your receive path as interim coverage, and treat unpatched Linux servers as denial-of-service targets.
Incident Summary
| CVE ID: | CVE-2026-99288 (NoisyTCP) |
| Severity: | High — remote, pre-authenticated denial of service |
| Affected Systems: | Linux kernel TCP subsystem; servers running Nginx, Apache, or SSH with default configurations across major distributions |
| Weakness: | NULL pointer dereference (CWE-476) via race condition in lockless socket lookups |
| Disclosure Date: | November 16, 2026 |
| Patch Status: | Available — merged into mainline kernel approximately two weeks prior to disclosure; distribution packages shipping |
| Researcher: | Hyunwoo Kim |
References
- BleepingComputer, “New NoisyTCP vulnerability lets attackers crash Linux servers,” November 16, 2026, https://www.bleepingcomputer.com/news/linux/new-noisytcp-linux-kernel-flaw-lets-attackers-crash-servers/ (accessed November 16, 2026).
- National Vulnerability Database, “CVE-2026-99288,” https://nvd.nist.gov/vuln/detail/cve-2026-99288 (accessed November 16, 2026).
- Red Hat, “CVE-2026-99288 — Linux Kernel TCP Socket Race Condition,” https://access.redhat.com/security/cve/cve-2026-99288 (accessed November 16, 2026).
- Hyunwoo Kim, “NoisyTCP — Research Advisory and Abstract,” GitHub, https://github.com/V4bel/NoisyTCP#abstract (accessed November 16, 2026).
- Linux Kernel, “Mainline Fix Commit for CVE-2026-99288,” https://git.kernel.org/pub/scm/linux/kernel/git/torvalds/linux.git/commit/?id=4e2b3ef19e0e04adca38442f07dd6bc93c712bf1 (accessed November 16, 2026).
- MITRE, “CWE-476: NULL Pointer Dereference,” https://cwe.mitre.org/data/definitions/476.html (accessed November 16, 2026).