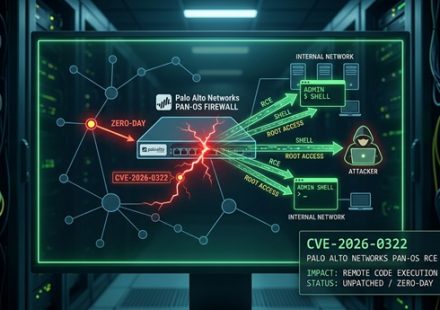
Palo Alto Networks PAN-OS RCE Zero-Day Lets Attackers Gain Root on Firewalls

October 15, 2026 Palo Alto Networks disclosed a high-severity remote code execution vulnerability in PAN-OS on October 14, 2026. The flaw, tracked as CVE-2026-0322, lets authenticated attackers execute code as root on vulnerable firewalls. CISA quickly…
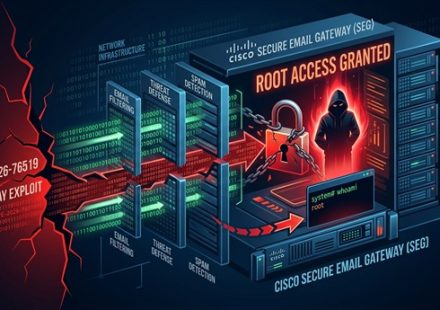
Cisco Secure Email Gateway Zero-Day Grants Root via Malicious Attachments
October 14, 2026 Cisco disclosed an actively exploited zero-day vulnerability in its Secure Email Gateway (SEG) on October 14, 2026. Tracked as CVE-2026-76519, this flaw lets remote unauthenticated attackers execute commands with root privileges by…
Actively Exploited Windows Shell Flaw Bypasses Mark of the Web Defenses
October 14, 2026 Microsoft patched an actively exploited command injection vulnerability in Windows Shell on October 13, 2026. Tracked as CVE-2026-96951, the flaw lets unauthorized attackers bypass Mark of the Web (MOTW) defenses over a network.…
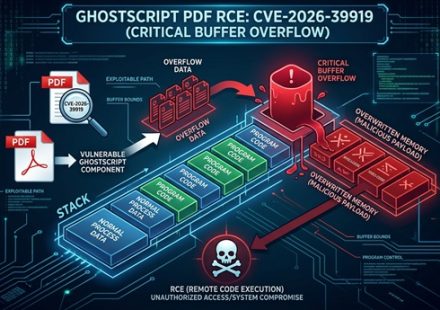
Critical Ghostscript PDF RCE Flaw Lets Attackers Hijack Servers via Malicious PDF Uploads
October 13, 2026 A critical heap buffer overflow vulnerability tracked as CVE-2026-39919 has been disclosed in the Ghostscript interpreter and rendering engine. Also known as the Ghostscript PDF RCE flaw, this vulnerability lets attackers execute remote…
Ivanti Connect Secure Zero-Day Chain Grants Root to Attackers
October 13, 2026 Ivanti disclosed an actively exploited zero-day vulnerability chain in Connect Secure (ICS) VPN appliances on October 13, 2026. Tracked as CVE-2026-104935, the flaw combines an authentication bypass and remote code execution to let…
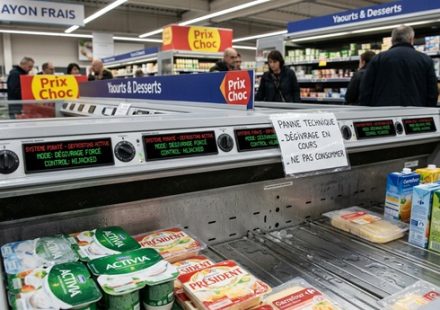
French Supermarket Danfoss Controllers Hijacked to Defrost Fridges
October 13, 2026 Attackers hijacked Danfoss refrigeration controllers at hundreds of French supermarkets on October 11, 2026. They remotely triggered defrost cycles and raised temperatures to 50°C, forcing stores to discard fresh and frozen food. The…
Dell System Update Path Traversal Grants Root to Unauthenticated Attackers
October 11, 2026 Dell disclosed a critical path traversal vulnerability in its System Update (DSU) command-line tool that allows unauthenticated remote attackers to execute arbitrary code with root privileges. The flaw, tracked as CVE-2026-86360, carries…
Rejetto HFS Authentication Bypass Under Active Exploitation
October 11, 2026 Threat actors are actively exploiting a critical authentication bypass in Rejetto HTTP File Server (HFS) that enables full administrative access and remote code execution. The vulnerability, tracked as CVE-2026-61500 (CVSS score: 9.3),…
ARTEX AI Attacks South Korean Banks
October 10, 2026 A Chinese-speaking threat actor used the open-source ARTEX AI penetration testing suite and Claude agents to breach multiple South Korean financial institutions in late September and early October 2026. CrowdStrike Intelligence confirmed…
Unpatched AhsayCBS Flaws Exploited to Deploy Webshells and Mine Crypto
October 10, 2026 Threat actors are actively exploiting two unpatched vulnerabilities in the AhsayCBS backup management platform to deploy webshells and cryptocurrency miners on victim systems. The flaws, tracked as CVE-2026-105133 and CVE-2026-105134,…