Citrix Confirms Two NetScaler RCE Zero-Days

September 27, 2026 Citrix has confirmed active exploitation of two critical remote code execution vulnerabilities in NetScaler ADC and NetScaler Gateway appliances. Tracked as CVE-2026-88771 and CVE-2026-88772, both flaws carry a severity score of 9.5…
CISA Adds WSO2 and Adobe Commerce Critical Flaws to KEV Catalog
September 27, 2026 CISA has added two new critical vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog, warning that attackers are actively exploiting flaws in WSO2 enterprise software and Adobe Commerce e-commerce platforms. Federal…
CISA Confirms Ransomware Gangs Exploiting Critical TeamCity RCE Flaw
September 24, 2026 CISA has upgraded its warning for CVE-2026-63077, a critical JetBrains TeamCity authentication bypass flaw now confirmed to be exploited by ransomware gangs. The vulnerability allows unauthenticated remote code execution via the agent…
WordPress CVE Critical Path Traversal Enables RCE
September 22, 2026 WordPress has released version 7.1.2 to patch a critical path traversal vulnerability in core. The flaw, tracked as CVE-2026-87902 with a CVSS score of 9.2, allows an unauthenticated attacker to include a readable PHP file from outside…
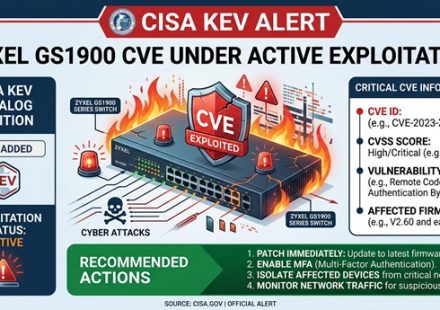
CISA KEV Alert: Zyxel GS1900 Switch CVE Under Active Exploitation
September 22, 2026 Attackers are now actively exploiting a stack-based buffer overflow in Zyxel GS1900 series switches, enabling unauthenticated remote code execution on local area networks. The flaw, tracked as CVE-2026-7273, has been added to…
CISA Flags Three Linux Kernel Flaws: Active Exploitation Confirmed
September 21, 2026 The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added three Linux kernel vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog after confirming active exploitation in the wild. Furthermore, one of…
WordPress Click2Shell Flaw Forces Theme Installs
September 20, 2026 WordPress released a security update on September 17, 2026, to fix a new core vulnerability researchers call Click2Shell. A crafted link can force a logged-in administrator to install a theme from the official WordPress.org directory…
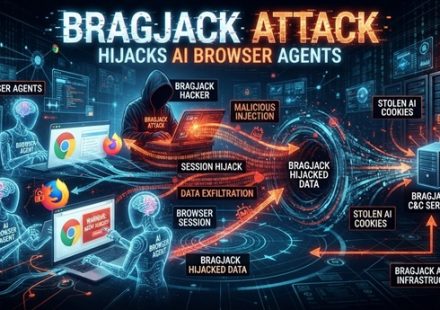
BragJack Attack Hijacks AI Browser Agents
September 19, 2026 Security researcher Gal Weizman of Forever Security has disclosed BragJack, a new attack technique that hijacks AI browser agents through malicious extensions. The proof-of-concept works against five major Chromium-based browsers and…
Check Point Root RCE via Management Server Login Flaw
September 18, 2026 Check Point Software has disclosed a critical vulnerability that lets unauthenticated attackers execute code with root privileges on Security Management Server and Log Server systems. The flaw, tracked as CVE-2026-91843, stems from a…
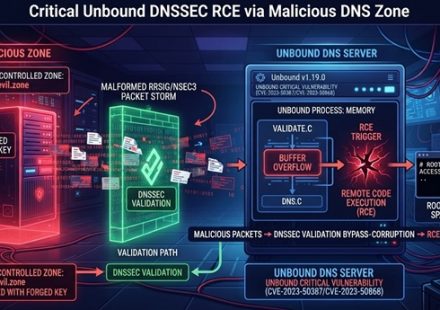
Critical Unbound DNSSEC Validator RCE via Malicious DNS Zone
September 18, 2026 A critical heap overflow vulnerability in the Unbound DNS resolver enables remote code execution through malicious DNS zones. The flaw, tracked as CVE-2026-81642, affects every Unbound release before version 1.26.1 and carries a CVSS…