Arista VeloCloud Orchestrator SQL Injection Zero-Day Grants Operator Privileges
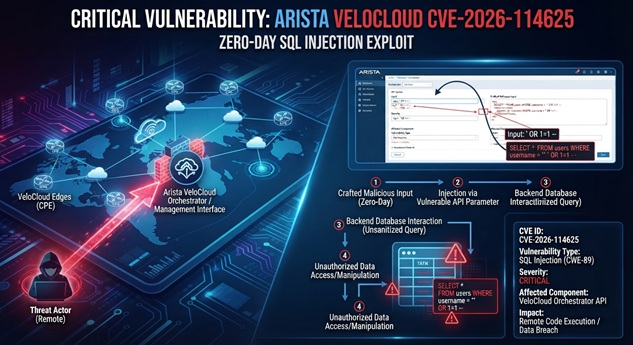
Arista Networks disclosed a critical zero-day vulnerability in VeloCloud Orchestrator on October 22, 2026. CVE-2026-114625 lets any authenticated user escalate to operator privileges through SQL injection. Attackers are actively exploiting it in the wild.
What Happened: Arista VeloCloud Orchestrator Zero-Day Under Active Attack
On October 22, 2026, Arista Networks released security updates for an actively exploited zero-day in VeloCloud Orchestrator (VCO). The flaw is tracked as CVE-2026-114625 and carries a CVSS score of 9.9. In addition, it is the fourth zero-day in VCO this year.
VeloCloud Orchestrator is the central management system for VeloCloud SD-WAN networks. It helps administrators configure, monitor, and manage SD-WAN deployments and edge devices. Consequently, a compromise of the orchestrator can give attackers broad control over an entire WAN infrastructure.
Technical Details of the CVE-2026-114625 Vulnerability
The vulnerability is a SQL injection flaw in the VCO web interface. Specifically, an attacker with a valid authenticated session can escalate privileges from any built-in role to operator level. The minimum required role is Enterprise Read Only, which is the lowest customer role.
Furthermore, the attack does not require user interaction and is considered low complexity. VCO is exposed by default, and no existing setting prevents the exposure. Therefore, this flaw is especially dangerous for organizations with internet-facing orchestrators.
Successful exploitation allows the attacker to:
- Masquerade as a local superuser operator
- Access internal functionality intended for remote use only
- Impact the confidentiality, integrity, and availability of the orchestrator
- Potentially affect the VCO host itself
This is the first of the four 2026 VCO zero-days that requires authentication. However, the July flaw (CVE-2026-16812) and September flaw (CVE-2026-93952) were both exploitable without any credentials. Therefore, organizations that patched for those flaws are still at risk if they have not applied the latest update.
Business and Operational Impact
VeloCloud SD-WAN is widely used by enterprises to manage branch connectivity. Moreover, a compromised orchestrator gives attackers full visibility and control over the network. The real-world consequences include:
- Network-wide disruption: Attackers can reconfigure or disable SD-WAN edge devices.
- Data exposure: Confidential network topology and traffic policies can be leaked. Moreover, encryption keys and certificates managed by VCO may also be compromised.
- Lateral movement: A compromised orchestrator can become a foothold for deeper intrusions. Consequently, the attacker may pivot to connected edge devices and branch networks.
- Supply-chain risk: Partners managed through VCO may also be affected.
Arista Networks is a Fortune 500 company with more than 10,000 customers worldwide. Therefore, the blast radius of this flaw is significant. In conclusion, any organization running vulnerable VCO instances should treat this as an emergency patching event.
Mitigation and Recommendations
Arista has released patches for on-premises deployments. In addition, hosted and dedicated orchestrators have already been patched by the vendor.
Immediate Actions for Defenders
- Upgrade on-premises VCO to one of the fixed releases: 5.2.3.18, 6.1.3.10, or 6.4.2.12.
- Restrict access to the VCO web interface to trusted administrative networks.
- Monitor VCO logs for connections from known malicious IP addresses: 74.82.197.86 and 38.54.50.151.
- Review recent administrator activity for unexpected changes.
- Check VCO web access logs for unusual URL-like path components, encoded characters, or references to internal services.
- Watch for unexpected outbound network activity from the VCO host.
- Consider blocking outbound ports that normal operation does not need.
- Preserve logs before remediation if compromise is suspected.
If You Cannot Upgrade Yet
If patching is not immediately possible, Arista recommends limiting web interface access to trusted networks and monitoring for the known malicious IPs. Moreover, watch for backdoor daemons and webshells on the VCO host. Also, consider disabling outbound internet access from the VCO host where feasible.
Bottom line: If you run VeloCloud Orchestrator on-premises, patch immediately. Restrict web access to administrative networks and monitor logs for the known attacker IPs. This is a critical flaw with active exploitation.
Incident Summary
| CVE ID / Incident: | CVE-2026-114625 |
| Affected Systems: | VeloCloud Orchestrator (VCO) On-Prem deployments before 5.2.3.18, 6.1.3.10, and 6.4.2.12 |
| Disclosure Date: | October 22, 2026 |
| Patch Status: | Patches available for on-premises deployments; hosted and dedicated orchestrators already patched |
| CVSS Score: | 9.9 (Critical) |
| Known Attacker IPs: | 74.82.197.86, 38.54.50.151 |
References
- Arista Networks, “Security Advisory 0199: VeloCloud Orchestrator SQL Injection Vulnerability,” October 22, 2026, https://www.arista.com/en/support/advisories-notices/security-advisory/24838-security-advisory-0199.
- BleepingComputer, “Arista patches new VeloCloud Orchestrator zero-day exploited in attacks,” October 22, 2026, https://www.bleepingcomputer.com/news/security/arista-patches-new-velocloud-orchestrator-zero-day-exploited-in-attacks/.
- The Hacker News, “Arista Warns of Critical VeloCloud SQL Injection Zero-Day Exploited in Attacks,” October 22, 2026, https://thehackernews.com/2026/10/arista-warns-of-critical-velocloud-sql.html.