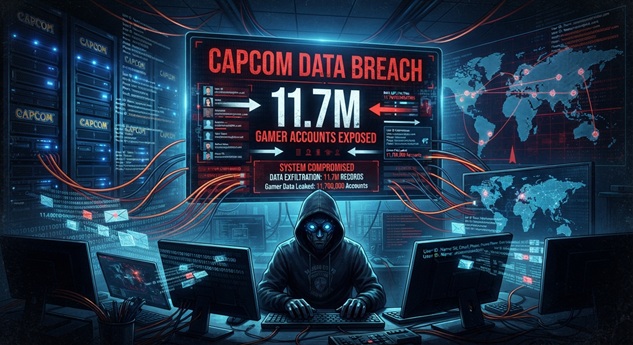
Japanese gaming giant Capcom confirmed a data breach of its CAPCOM ID membership service. The incident exposed more than 11.7 million customer email addresses and associated account information. Capcom disclosed the breach on October 22, 2026, after detecting suspicious activity two days earlier.
What Happened: Capcom Data Breach Exposes 11.7 Million Gamer Accounts
Capcom discovered unauthorized access to its CAPCOM ID system on October 19, 2026. The company launched an investigation immediately. By October 20, investigators confirmed that customer information had been compromised. Capcom reported the incident to Japanese law enforcement and the country’s Personal Information Protection Commission on October 21.
The exposed data includes email addresses, account creation dates, last login timestamps, number of logins, and the IP addresses used at last login. For a small subset of 43 accounts, dates of birth, gender, nicknames, and countries were also exposed. In addition, attackers changed the login passwords for 196 accounts in an attempt to lock legitimate users out. Capcom reset those passwords promptly.
Capcom stated that passwords for all other registered members were not exposed. Furthermore, credit card information remained unaffected. The company says its online gaming services continue to operate normally. However, the Quanum LSM system has been stopped as a cautionary measure. Consequently, customers must use paper requisitions or Quanum eLabs to place orders and receive results.
Technical Details of the Capcom CAPCOM ID Breach
Capcom has not publicly disclosed the initial access vector used in this attack. The company says it identified the intrusion method during its investigation. Moreover, it implemented security measures to prevent similar incidents. However, specific technical details about how the attackers gained entry remain undisclosed.
This is not Capcom’s first data breach. In November 2020, the Ragnar Locker ransomware gang attacked the company. Attackers claimed to have stolen 1 TB of data. In April 2021, Capcom disclosed that the 2020 attackers had gained access through an old VPN device. The company subsequently warned that up to 390,000 people could be affected by that earlier incident.
Attack Timeline
- October 19, 2026: Capcom detects suspicious activity on CAPCOM ID systems.
- October 20, 2026: Investigation confirms unauthorized access and customer data exposure.
- October 21, 2026: Capcom reports the breach to police and Japan’s Personal Information Protection Commission.
- October 22, 2026: Public disclosure via SEC filing and company alert.
Exposed Data Elements
- Email addresses (11.7 million accounts)
- Account creation dates
- Last login timestamps
- Total number of logins
- IP address from last login
- For 43 accounts: dates of birth, gender, nicknames, and country
Business and Operational Impact
The Capcom data breach carries significant consequences for the gaming company and its customers. Capcom is a major Japanese video game developer known for franchises such as Resident Evil, Monster Hunter, Street Fighter, and Mega Man. The company employs 4,000 people and generates $1.24 billion in annual revenue.
- Customer trust erosion: Gamers may lose confidence in Capcom’s ability to protect personal data.
- Regulatory scrutiny: Japan’s Personal Information Protection Commission will likely investigate compliance with data protection laws.
- Phishing risk: Exposed email addresses create a large attack surface for targeted phishing campaigns impersonating Capcom.
- Account takeover potential: Although passwords were not exposed, combined with data from other breaches, attackers may attempt credential stuffing.
- Legal exposure: Following the 2019 Quest Diagnostics breach, at least 19 class-action lawsuits were filed. Capcom may face similar litigation.
Mitigation and Recommendations
Immediate Actions for Capcom Users
- Change your CAPCOM ID password immediately. Use a strong, unique password not reused on other sites.
- Enable multi-factor authentication (MFA) on your CAPCOM ID account if available.
- Monitor your email for phishing messages claiming to be from Capcom. Do not click links or download attachments from unsolicited messages.
- Watch for suspicious login activity on any accounts that share the same email address as your CAPCOM ID.
- Consider using a password manager to generate and store unique passwords for every service.
Recommendations for Organizations
- Review and secure legacy VPN devices and remote access infrastructure. Old VPN appliances are a recurring initial access vector.
- Implement network segmentation to limit lateral movement if an account system is compromised.
- Apply principle of least privilege to all customer-facing systems and databases.
- Enable comprehensive logging and monitoring on identity and access management systems.
- Conduct regular penetration testing on membership and authentication platforms.
Bottom line: Capcom’s breach demonstrates that even major gaming companies remain vulnerable to account system compromises. Users should treat the exposed email addresses as a phishing risk and lock down their accounts now. Organizations should audit their own identity platforms and eliminate weak remote access paths.
Incident Summary
| Incident: | Capcom CAPCOM ID Data Breach |
| Affected Systems: | CAPCOM ID membership service |
| Exposed Records: | 11.7 million customer accounts |
| Disclosure Date: | October 22, 2026 |
| Detection Date: | October 19, 2026 |
| Patch Status: | Security measures implemented; ongoing investigation |
| Threat Actor: | Unknown / undisclosed |
References
- Bill Toulas, BleepingComputer, “Capcom confirms data breach affecting 11.7 million accounts,” October 22, 2026, https://www.bleepingcomputer.com/news/security/capcom-confirms-data-breach-affecting-117-million-accounts/, accessed October 23, 2026.
- Capcom Co., Ltd., “Regarding Unauthorized Access to CAPCOM ID,” October 22, 2026, https://www.capcom.co.jp/ir/news/html/261022.html, accessed October 23, 2026.
- U.S. Securities and Exchange Commission, “Quest Diagnostics 8-K Filing,” October 21, 2026, https://www.sec.gov/ix?doc=/Archives/edgar/data/0001022079/000094787126000941/ss6979200_8k.htm, accessed October 23, 2026.
- Bill Toulas, BleepingComputer, “Quest Diagnostics confirms data breach exposed patient records,” October 23, 2026, https://www.bleepingcomputer.com/news/security/quest-diagnostics-confirms-data-breach-exposed-patient-records/, accessed October 23, 2026.