Meta Muse AI Assistant Creates macOS Backdoor Vulnerability

September 22, 2026 Security researcher Patrick Wardle has disclosed a serious vulnerability in Meta’s new Muse AI assistant for macOS. The flaw lets malware already on a Mac quietly hijack Muse and abuse the broad permissions its owner granted the…
WordPress CVE Critical Path Traversal Enables RCE
September 22, 2026 WordPress has released version 7.1.2 to patch a critical path traversal vulnerability in core. The flaw, tracked as CVE-2026-87902 with a CVSS score of 9.2, allows an unauthenticated attacker to include a readable PHP file from outside…
CISA KEV Alert: Zyxel GS1900 Switch CVE Under Active Exploitation
September 22, 2026 Attackers are now actively exploiting a stack-based buffer overflow in Zyxel GS1900 series switches, enabling unauthenticated remote code execution on local area networks. The flaw, tracked as CVE-2026-7273, has been added to…
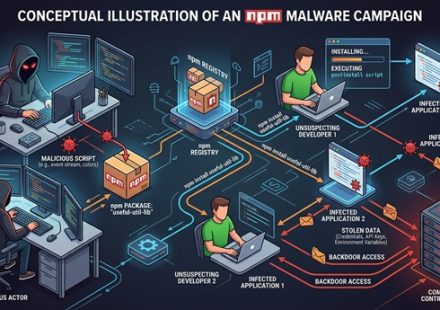
Malicious npm Packages Evade Install-Script Defenses
September 20, 2026 Threat actors have published a malicious npm package named indexed-btree that evades GitHub’s latest install-script defenses by hiding its payload inside normal runtime behavior. The package has already accumulated more than 2…
WordPress Click2Shell Flaw Forces Theme Installs
September 20, 2026 WordPress released a security update on September 17, 2026, to fix a new core vulnerability researchers call Click2Shell. A crafted link can force a logged-in administrator to install a theme from the official WordPress.org directory…
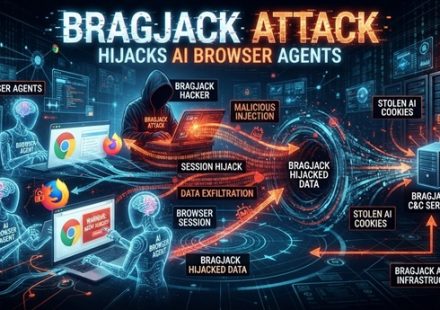
BragJack Attack Hijacks AI Browser Agents
September 19, 2026 Security researcher Gal Weizman of Forever Security has disclosed BragJack, a new attack technique that hijacks AI browser agents through malicious extensions. The proof-of-concept works against five major Chromium-based browsers and…
Check Point Root RCE via Management Server Login Flaw
September 18, 2026 Check Point Software has disclosed a critical vulnerability that lets unauthenticated attackers execute code with root privileges on Security Management Server and Log Server systems. The flaw, tracked as CVE-2026-91843, stems from a…
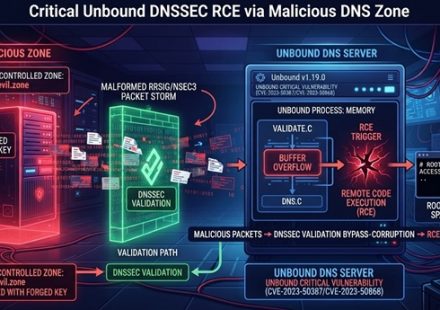
Critical Unbound DNSSEC Validator RCE via Malicious DNS Zone
September 18, 2026 A critical heap overflow vulnerability in the Unbound DNS resolver enables remote code execution through malicious DNS zones. The flaw, tracked as CVE-2026-81642, affects every Unbound release before version 1.26.1 and carries a CVSS…
CISA Confirms Active Exploitation of Critical GitLab Path Traversal
September 14, 2026 CISA has added CVE-2026-85706 to its Known Exploited Vulnerabilities catalog after confirming active exploitation in the wild. This maximum-severity path traversal flaw affects GitLab Community Edition and Enterprise Edition.…
UNC3569 Exploits Sogou Input Method Flaw to Deploy GRAYRABBIT Backdoor
September 13, 2026 Threat actors linked to a China-aligned espionage group are exploiting a critical vulnerability (CVE-2026-51990) in Tencent’s Sogou Input Method for Windows to deploy the GrayRabbit backdoor. The flaw allows one-click remote code…