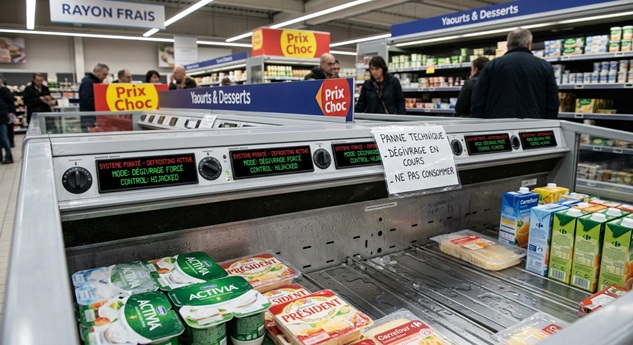
Attackers hijacked Danfoss refrigeration controllers at hundreds of French supermarkets on October 11, 2026. They remotely triggered defrost cycles and raised temperatures to 50°C, forcing stores to discard fresh and frozen food. The incident marks one of the most direct operational technology attacks against retail supply chains in recent years.
What Happened: Attackers Hijack Danfoss Controllers to Defrost French Supermarket Fridges
On the night of October 11, threat actors took remote control of refrigeration systems at major French retail chains. The attackers targeted controllers manufactured by Danish company Danfoss, which maintenance firms use to manage store fridges and freezers remotely.
Victims include Intermarché, Coopérative U, Carrefour Market, Monoprix, and E.Leclerc. French outlets report that between 250 and 350 stores were affected. Les Mousquetaires, which owns the Intermarché chain, confirmed its fridges and freezers were put into defrost and heated to as much as 50°C.
Consequently, stores had to throw away large volumes of perishable goods. Intermarché said affected stores discarded all products concerned. Thierry Cotillard, head of Les Mousquetaires, told BFMTV he expected losses of tens of millions of euros across France.
The Paris prosecutor’s office opened an investigation on October 12 into what it described as a “large-scale cyberattack affecting the refrigerators of several major food retail chains across France.” The inquiry aims to identify victims and link the attack to reported damage, including food losses and equipment fires.
Technical Details of the Refrigeration Controller Attack
The attackers reached supermarket refrigeration systems through Danfoss controllers. These devices manage cooling across entire stores and are often remotely accessible for maintenance.
CERT-FR, France’s national computer emergency response team, issued an alert on October 12 naming two compromised controller series: the AK-SM and the AK-SC. ANSSI head Vincent Strubel called it urgent to take both series off the internet or filter access very tightly.
Danfoss stated that most units hit were older models no longer receiving updates:
- AK-SM 800 — End of life since May 2021. No software or security updates available.
- AK-SC 355 — Phased out in 2016. No software or security updates available.
- AK-SM 800A — Current model. Some units running outdated firmware were also compromised.
Moreover, researchers at Claroty disclosed three vulnerabilities in the newer AK-SM 800A in 2025. CVE-2025-41450 is an authentication bypass, and CVE-2025-41451 is a command injection flaw leading to remote code execution. Both were fixed in version 4.3.1. While neither French authorities nor Danfoss has linked these CVEs directly to this attack, the existence of known flaws in internet-exposed controllers highlights the attack surface.
Predicta Lab CEO Baptiste Robert found 2,752 Danfoss systems exposed online on October 12, with 1,590 of them in France. Shodan tracks over 4,500 Danfoss devices reachable over the internet.
Business and Operational Impact
The attack caused immediate operational disruption across France’s retail sector. Stores faced food spoilage, supply chain delays, and financial losses.
- Intermarché and Netto: At least 300 stores affected across both brands.
- Coopérative U: 80 of 2,000 stores hit. Most maintained cold chain, but a minority lost goods.
- Carrefour: 80 supermarkets affected.
- Monoprix: About 30 stores hit.
- E.Leclerc: Several stores affected.
In addition, EU agriculture and food commissioner Christophe Hansen condemned the attack. Coopérative U president Dominique Schelcher called it “unprecedented” and “unacceptable” to target equipment essential for preserving fresh produce.
The attack may have spread beyond France. Félix Aimé, a senior threat intelligence analyst at Sekoia, told Reuters that Spain, Portugal, Poland, Germany, and Belgium had also been affected. Furthermore, retail giant Ahold Delhaize announced on October 12 that it had taken some systems offline after a “cybersecurity incident,” though no direct link to the Danfoss attack has been confirmed.
Mitigation and Recommendations
CERT-FR issued immediate guidance for operators of AK-SM and AK-SC controllers.
Immediate Actions for Defenders
- Disconnect controllers from the internet or filter access to trusted IP addresses only.
- Perform a factory reset on any potentially compromised device.
- Apply all available security fixes for supported models.
- Change all device passwords and secrets.
- Audit existing accounts for unauthorized access.
- Reconfigure devices completely after remediation.
Long-Term Hardening
For AK-SM 800A units, Danfoss advises upgrading to the latest firmware package (5.3.x as of October 13). Starting with version 4.0, Strict Session Control is enabled by default and makes HTTPS mandatory. Therefore, operators should prioritize firmware updates and disable direct internet exposure.
Danfoss’s general security guidance recommends keeping controllers unreachable from the internet, changing default passwords at installation, and requiring remote users to log in through a single managed entry point.
Bottom line: Internet-exposed operational technology devices with end-of-life firmware present a growing attack surface. Retailers and facility managers must inventory OT assets, remove them from public internet access, and replace unsupported hardware before attackers exploit known vulnerabilities.
Incident Summary
| Incident: | French Supermarket Refrigeration Cyberattack — Danfoss Controller Hijacking |
| Affected Systems: | Danfoss AK-SM 800, AK-SC 355, AK-SM 800A refrigeration controllers |
| Disclosure Date: | October 12, 2026 |
| Patch Status: | AK-SM 800 and AK-SC 355 are end-of-life with no patches. AK-SM 800A firmware 5.3.x available. |
| Known CVEs: | CVE-2025-41450 (auth bypass), CVE-2025-41451 (command injection/RCE) in AK-SM 800A |
| Affected Retailers: | Intermarché, Coopérative U, Carrefour, Monoprix, E.Leclerc |
| Estimated Stores Hit: | 250–350+ stores across France |
References
- BleepingComputer, “Cyberattack shuts down refrigerators at French supermarkets,” October 12, 2026, https://www.bleepingcomputer.com/news/security/cyberattack-shuts-down-refrigerators-at-french-supermarkets/.
- The Hacker News, “Attackers Heat French Supermarket Fridges Up to 50°C by Hijacking Danfoss Controllers,” October 13, 2026, https://thehackernews.com/2026/10/attackers-heat-french-supermarket.html.
- CERT-FR, “Alerte CERT-FR-2026-ALE-012,” October 12, 2026, https://www.cert.ssi.gouv.fr/alerte/CERTFR-2026-ALE-012/.
- Claroty Team82, “Freeze the Controller, Defrost the Food: Uncovering Vulnerabilities in Danfoss Refrigeration Controllers,” August 2025, https://claroty.com/team82/research/freeze-the-controller-defrost-the-food-uncovering-vulnerabilities-in-danfoss-refrigeration-controllers.
- CISA, “Vulnerability Bulletins SB25-132 and SB25-237,” May and August 2025, https://www.cisa.gov/news-events/bulletins/sb25-132.
- Danfoss Security Advisories, “DSA-2025-03-01” and “DSA-2025-08-01,” 2025, https://www.danfoss.com/en/service-and-support/coordinated-vulnerability-disclosure/danfoss-security-advisories/.