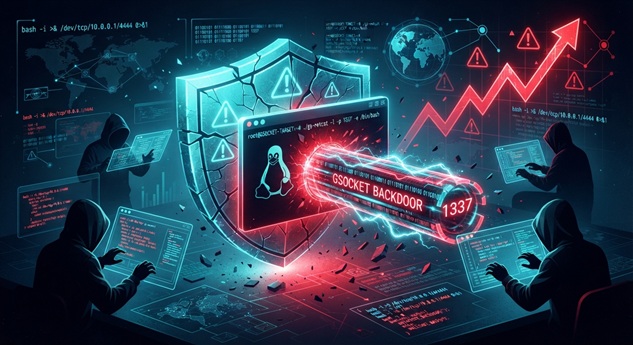
Threat actors are weaponizing GSocket, a legitimate open-source remote access tool, to maintain persistent access to Linux servers even after defenders patch the vulnerabilities used for initial entry. Microsoft Defender for Endpoint telemetry shows detections of malicious GSocket activity surged 356.2 percent between March and August this year, with web applications and hosting environments bearing the brunt of the abuse.
What Happened: Threat Actors Weaponize GSocket for Stealthy Linux Backdoors
Since March 2026, multiple threat actors have increasingly abused GSocket to establish covert command-and-control channels on compromised Linux systems. GSocket is an open-source tool designed to let users reach systems behind firewalls and NAT by routing connections through the Global Socket Relay Network. However, attackers are subverting this same capability to create stealthy backdoors that do not require inbound listeners or public IP addresses.
Microsoft published research on November 11, 2026, warning that the compromised host and the operator both connect outbound to the relay. Consequently, the server needs no inbound listener, and network address translation does not prevent the connection. This also removes the need for attackers to deploy a dedicated command-and-control server. Therefore, traditional inbound firewall rules do not catch the malicious traffic, forcing defenders to rely on egress filtering and outbound monitoring instead.
Technical Details of the GSocket Attack
GSocket intercepts network connections and replaces a program’s conventional IP-layer communication with its own transport layer. Both the compromised server and the attacker initiate outbound connections to the Global Socket Relay Network, which matches the sessions and brokers an end-to-end encrypted tunnel. The attacker can reconnect without needing the compromised server’s IP address or hostname.
Microsoft found that 87.1 percent of detected GSocket incidents involved web applications and hosting environments. PHP web applications and cPanel hosting accounted for 63.9 percent of cases, and Apache servers accounted for 24.3 percent. In addition, researchers observed attackers disguising GSocket as kernel threads and using cron jobs, systemd services, and shell startup files for persistence.
- Attackers require no inbound listener implant on the compromised host.
- Both endpoints initiate outbound connections to a relay network, making IP- and domain-based blocklists ineffective.
- Persistence is achieved via cron jobs, systemd services, and shell startup file modifications.
- In some cases, attackers attempted to escalate privileges by exploiting the Linux kernel Dirty Frag flaw (CVE-2026-43284).
Business and Operational Impact
The abuse of legitimate remote access tools for malicious purposes creates significant operational challenges. Because GSocket is a genuine open-source project, its presence alone does not trigger many endpoint detection rules, and its traffic may blend with legitimate outbound flows. Moreover, the removal of inbound listener requirements means that standard network segmentation and firewall rules are insufficient.
- Education and research sectors were the most frequently targeted industries.
- Technology and communications, manufacturing, and government entities also saw significant activity.
- Defenders face difficulty disrupting connections because attackers do not need the server’s public IP or hostname to reconnect.
- The use of native persistence mechanisms complicates cleanup and increases dwell time.
Mitigation and Recommendations
Microsoft recommends a defense-in-depth approach that prioritizes egress controls and host-level hygiene. Consequently, organizations should not rely solely on perimeter firewalls to detect or prevent this threat.
Immediate Actions for Defenders
- Remove GSocket and associated files from potentially impacted servers immediately.
- Verify that outbound connections to the Global Socket Relay Network have stopped.
- Audit cron jobs, systemd services, and shell startup files for rogue additions.
- Restrict outbound traffic to predetermined destinations and known-good endpoints.
- Apply patches for CVE-2026-43284 and other Linux kernel vulnerabilities to close privilege escalation paths.
Long-Term Hardening
Organizations should implement egress filtering and monitor outbound connections for anomalies. Furthermore, maintaining up-to-date operating systems and applications reduces the attack surface that threat actors exploit for initial access. Finally, security teams should review web application and hosting configurations, particularly for PHP and cPanel environments, which represent the majority of observed targets.
Bottom line: Threat actors are abusing legitimate remote access tools to build stealthy, persistent backdoors on Linux servers. Defenders must shift focus from inbound perimeter controls to egress monitoring, host-level auditing, and timely patching to disrupt these campaigns.
Incident Summary
| CVE ID / Incident: | GSocket Abuse Campaign (CVE-2026-43284 — Dirty Frag Privilege Escalation) |
| Affected Systems: | Linux servers; PHP web apps and cPanel hosting (63.9%), Apache (24.3%) |
| Disclosure Date: | November 11, 2026 |
| Patch Status: | Patch available for CVE-2026-43284; remove GSocket and audit for persistence mechanisms |
References
- Microsoft Security Blog, “Global Socket: How Threat Actors Are Weaponizing GSocket for Stealthy C2,” November 11, 2026, https://www.microsoft.com/en-us/security/blog/2026/11/11/global-socket-how-threat-actors-weaponizing-gsocket-stealthy-c2/, accessed November 12, 2026.
- BleepingComputer, “Hackers plant GSocket on Linux servers for persistent access,” November 12, 2026, https://www.bleepingcomputer.com/news/security/hackers-plant-gsocket-on-linux-servers-for-persistent-access/, accessed November 12, 2026.