CISA has added four Plex Media Server vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog after confirming active exploitation in the wild. The flaws, collectively tracked as Plex2Shell, allow remote attackers to achieve unauthenticated remote code execution on exposed servers. Consequently, threat actors are already weaponizing the bugs to deploy cryptocurrency miners and proxy malware.
What Happened: Plex2Shell Attack Chain Exploits Plex Media Server
On October 20, 2026, CISA published an alert adding six vulnerabilities to its KEV catalog. Four of those affect Plex Media Server and have been chained together into the Plex2Shell exploit. In addition, researchers confirmed in-the-wild exploitation within hours of public disclosure.
Security researcher Zach Main discovered and reported the vulnerabilities on July 27, 2026. Plex patched them on September 1 with version 1.43.3.10861. However, the detailed write-up and proof-of-concept code were released publicly on October 16. Furthermore, another researcher running a vulnerable Plex honeypot observed the first successful exploitation attempt on October 17.
The four vulnerabilities are:
- CVE-2026-96652 (CVSS 5.3) — Server-Side Request Forgery (SSRF) via the
/player/timelineendpoint - CVE-2026-96654 (CVSS 6.9) — Improper neutralization of encoded URI schemes in a web page
- CVE-2026-96655 (CVSS 5.3) — Server-Side Request Forgery (SSRF) vulnerability
- CVE-2026-96656 (CVSS 8.6) — External control of file name or path
Technical Details of the Plex2Shell Vulnerability Chain
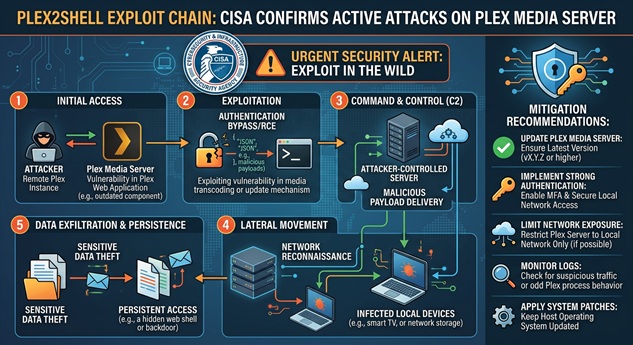
The Plex2Shell exploit chain is a five-stage attack that starts with an unauthenticated attacker on the internet and ends with arbitrary code execution on the Plex host.
Stage 1: Unauthenticated SSRF
Plex Media Server includes a companion protocol for remote controls and casting devices. The /player/timeline endpoint checks only that an X-Plex-Token header exists, not that the value is valid. Therefore, any junk token is accepted.
The endpoint’s subscription flow constructs a callback URL from user-supplied protocol, host, and port parameters. The protocol parameter is inserted into the URL without validation. For example, an attacker can inject a full URL pointing to http://127.0.0.1:32400/system/agents/.... When the server unsubscribes, it POSTs to that URL — from a genuine loopback origin. Thus, the attacker achieves a blind SSRF against the server itself.
Stage 2: Loopback Pivot
The /system/agents/* API family is intended to manage plugins and agents. Moreover, it requires no token when the request originates from loopback. Using the Stage 1 SSRF, the attacker can reach this API.
The searchOne endpoint contains a broken guard: a @lock decorator wraps the inner function and discards its return value. Consequently, even when the identifier check fails, the function continues executing. The attacker can then forge a call to any plugin function on loopback.
Stage 3: Owner Token Theft
The bundled TheTVDB agent includes a GetResultFromNetwork function that fetches URLs. When the plugin framework makes an outbound HTTP request whose URL starts with http://127.0.0.1, it automatically appends the owner admin token in the X-Plex-Token header.
The prefix check is unbounded: http://127.0.0.1.evil.com also matches. Therefore, the attacker uses sslip.io DNS trickery to make a hostname that passes the prefix check but resolves to the attacker’s IP. The server sends the owner token to the attacker, granting full admin access.
Stage 4: Payload Delivery
With the owner token, the attacker controls the TranscoderH264Options server preference. This value is appended verbatim to the x264 encoder command line on every transcode. By setting dump-yuv=/path/to/target.so, the attacker can write attacker-controlled bytes to an arbitrary file path during a transcode operation.
Stage 5: Code Execution
At startup, Plex enumerates and dlopen()s every .so file in its Codecs directory. It does not verify signatures, require execute bits, or check for expected symbols. Therefore, the attacker-written shared object is loaded automatically. Its constructor runs inside the Plex process, achieving code execution as the plex user.
Business and Operational Impact
Organizations running exposed or poorly segmented Plex Media Server instances face several risks:
- Cryptocurrency mining: In-the-wild exploitation has already been observed deploying XMRig miners on compromised servers.
- Proxy malware: Attackers have also deployed proxy software called myawesomeproxy, likely to abuse residential IP addresses for pivoting into corporate VPNs and email systems.
- Data access: The attacker gains owner-level access, which includes reading preferences, managing libraries, and potentially accessing media files.
- Supply-chain risk: Plex is commonly run on home servers and small cloud instances that may share networks with more sensitive assets.
Mitigation and Recommendations
Immediate Actions for Defenders
- Upgrade Plex Media Server to version 1.43.3.10861 or later on every host. This is the only complete fix.
- Restrict admin access to trusted networks using firewall rules or reverse-proxy access controls.
- Review TranscoderH264Options and reset it to the default if it has been modified.
- Inspect Plex module and plugin directories for unauthorized
.sofiles and remove any that are unexpected. - Rotate any credentials or tokens that may have been exposed if a server was compromised.
Detection and Monitoring
- Monitor for unexpected
.sofiles inside Plex plugin, codec, or resource directories. - Alert on non-default values in the
TranscoderH264Optionspreference. - Track administrative logins to the Plex web interface and flag unfamiliar source addresses.
- Correlate transcode activity with subsequent library loads to spot writes followed by dynamic loading.
Network and Architecture Controls
- Run Plex under a dedicated, least-privileged account.
- Apply filesystem permissions that prevent the Plex user from writing into directories scanned for
.sofiles. - Enable filesystem integrity monitoring on Plex module and plugin directories.
Bottom line: Plex Media Server versions before 1.43.3.10861 are under active attack. If you run Plex, patch immediately. Moreover, restrict admin access to trusted networks and audit your deployment for unauthorized shared objects.
Incident Summary
| CVE IDs: | CVE-2026-96652, CVE-2026-96654, CVE-2026-96655, CVE-2026-96656 |
| Affected Product: | Plex Media Server versions prior to 1.43.3.10861 |
| Disclosure Date: | September 1, 2026 (patch); October 16, 2026 (public details) |
| CISA KEV Addition: | October 20, 2026 |
| Patch Status: | Fixed in Plex Media Server 1.43.3.10861 (released August 3, 2026) |
| CVSS Scores: | 5.3 (CVE-2026-96652), 6.9 (CVE-2026-96654), 5.3 (CVE-2026-96655), 8.6 (CVE-2026-96656) |
| Exploitation Status: | Confirmed in the wild; cryptominer and proxy malware payloads observed |
| Discovered By: | Zach Main (reported July 27, 2026) |
References
- CISA, “CISA Adds Six Known Exploited Vulnerabilities to Catalog,” October 20, 2026, https://www.cisa.gov/news-events/alerts/2026/10/20/cisa-adds-six-known-exploited-vulnerabilities-catalog.
- The Hacker News, “CISA Orders Federal Agencies to Patch Exploited Plex2Shell, Siemens, and SiteGuard Flaws,” October 21, 2026, https://thehackernews.com/2026/10/cisa-orders-federal-agencies-to-patch.html.
- Zach Main, “Plex2Shell,” October 16, 2026, https://zmain.info/blog/plex2shell.
- BoredHackerBlog, “Plex vulnerabilities being exploited in the wild to drop a cryptominer,” October 17, 2026, https://www.boredhackerblog.info/2026/10/plex-vulnerabilities-being-exploited-in.html.
- SecurityWeek, “Plex2Shell Exploit Chain Weaponized Against Plex Servers Hours After Disclosure,” October 18, 2026, https://www.securityweek.com/plex2shell-exploit-chain-weaponized-against-plex-servers-hours-after-disclosure/.
- SentinelOne, “CVE-2026-96656: Plex Media Server RCE Vulnerability,” September 24, 2026, https://www.sentinelone.com/vulnerability-database/cve-2026-96656/.