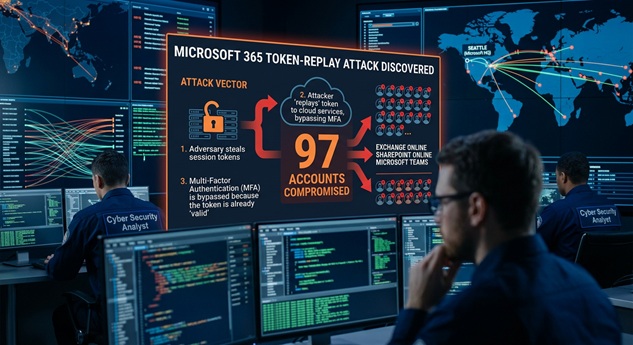
Huntress researchers have disclosed a widespread Microsoft 365 campaign that leveraged adversary-in-the-middle (AitM) relays to steal and replay session tokens. Consequently, attackers compromised 97 accounts across 79 organizations without ever guessing a password.
What Happened: Token-Spraying Attack Hijacks Microsoft 365 Accounts at Scale
Between July 14 and September 22, 2026, threat actors operated an AitM relay that intercepted legitimate sign-in traffic. Moreover, they replayed captured tokens in a technique Huntress calls token spraying. Therefore, the attackers bypassed multi-factor authentication at machine speed.
Huntress observed 497 successful sign-in events originating from over 200,000 login attempts. Furthermore, the campaign was traced to the 193.26.115.0/24 IP range hosted by 1337 Services GmbH in Germany. In at least 19 organizations, the attackers removed existing MFA methods and registered a new authenticator app within three hours of first entry.
Technical Details of the Token-Replay Attack
The attack chain follows a now-familiar AitM pattern, but with a twist. First, victims are lured to a fake Microsoft login page. Then the attacker relays entered credentials and MFA codes to the real Microsoft infrastructure in real time. However, the goal is not the password itself. Instead, the attacker harvests the session token issued after successful authentication.
Within minutes, the stolen token is replayed from attacker-controlled devices. Also, the threat actors registered at least 48 rogue Entra devices across victim organizations. Thus, they gained a durable way to request fresh tokens even after original sessions expired.
Moreover, the attackers established hidden email rules in compromised inboxes. For example, rules with names such as “.”, “sss”, and “……..” automatically deleted or moved messages containing keywords like payroll, deposit, and bonus to obscure folders like RSS Feeds and Conversation History.
Business and Operational Impact
The campaign demonstrates how AitM attacks can render traditional MFA ineffective. Therefore, organizations relying solely on password-plus-MFA remain exposed. The impact extends across several areas:
- Account takeover at scale: 97 confirmed compromises across 79 organizations.
- Financial fraud: Hidden email rules targeted payroll and bonus communications.
- Outbound abuse: At least one compromised mailbox was used to send spam to hundreds of external recipients.
- Persistence: Rogue Entra device registrations provided long-term access independent of stolen session tokens.
- Reputational harm: Victims included businesses whose customer trust depends on secure communications.
Mitigation and Recommendations
Immediate Actions for Defenders
- Revoke sessions and reset passwords for any accounts suspected of compromise.
- Audit Entra devices and remove any that are unrecognized or unregistered by IT.
- Review MFA methods on all accounts for unexpected authenticator app registrations.
- Check inbox rules for hidden or obscurely named filters that delete or redirect mail.
- Restrict device-code workflows using Conditional Access policies.
Strategic Hardening
Huntress recommends implementing Conditional Access Policies (CAP) that require MFA unconditionally for all users, all cloud apps, and all client app types. Furthermore, CAPs should be configured to block sign-ins from unexpected locations or devices. Also, organizations should monitor for rapid MFA method changes and new device registrations as high-fidelity indicators of compromise.
Bottom line: AitM token replay bypasses the MFA your users trust. Therefore, defense must shift from identity verification alone to continuous session and device verification through Conditional Access.
Incident Summary
| Incident: | Microsoft 365 Token-Replay / Token-Spraying Campaign |
| Affected Platform: | Microsoft 365 / Entra ID |
| Disclosure Date: | October 26, 2026 |
| Observation Window: | July 14 – September 22, 2026 |
| Compromised Accounts: | 97 accounts across 79 organizations |
| Attack Vector: | Adversary-in-the-middle (AitM) relay + token replay |
| Persistence Mechanism: | Rogue Entra device registration + attacker-controlled MFA |
| Attacker Infrastructure: | 193.26.115.0/24 (1337 Services GmbH) |
| Patch Status: | N/A — configuration and policy-based mitigation |
References
- Huntress, “Token Replay Spray: How Attackers Are Replaying Stolen Microsoft 365 Tokens at Scale,” October 26, 2026, https://www.huntress.com/blog/token-replay-spray.
- The Hacker News, “Microsoft 365 Token-Replay Attacks Compromise 97 Accounts at 79 Organizations,” October 26, 2026, https://thehackernews.com/2026/10/microsoft-365-token-replay-attacks.html.
- GreyNoise, “1337 Services GmbH IP Intelligence,” accessed October 26, 2026, https://viz.greynoise.io/ips.