Palo Alto Networks PAN-OS RCE Zero-Day Lets Attackers Gain Root on Firewalls
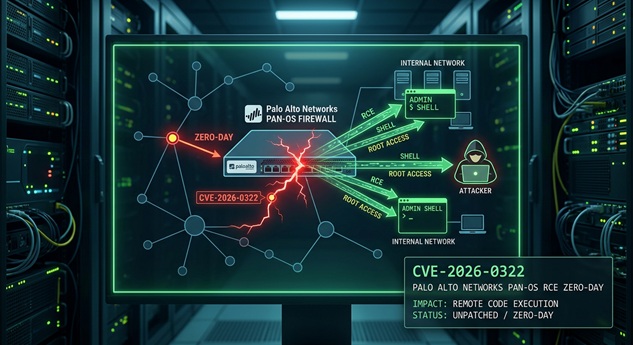
Palo Alto Networks disclosed a high-severity remote code execution vulnerability in PAN-OS on October 14, 2026. The flaw, tracked as CVE-2026-0322, lets authenticated attackers execute code as root on vulnerable firewalls. CISA quickly added it to the Known Exploited Vulnerabilities catalog and set a federal patching deadline of October 17, 2026.
What Happened: Palo Alto Networks PAN-OS RCE Zero-Day Under Active Exploitation
Palo Alto Networks published a security advisory confirming limited but active exploitation of CVE-2026-0322. The vulnerability resides in the PAN-OS management interface. Attackers with valid credentials and network access can inject code and gain root privileges on the target device.
The U.S. Cybersecurity and Infrastructure Security Agency added the flaw to its KEV catalog on October 14, 2026. Federal civilian agencies must remediate it by October 17, 2026. Palo Alto Networks also shared three attacker IP addresses observed exploiting the flaw:
- 66.42.72[.]14
- 208.83.239[.]114
- 149.248.47[.]234
However, the vendor has not disclosed when exploitation began, who is behind the attacks, or whether any firewalls were fully compromised.
Technical Details of the PAN-OS Management Interface Vulnerability
CVE-2026-0322 is a code injection vulnerability in the PAN-OS management interface. An authenticated attacker with network access can exploit it to execute arbitrary code with root privileges. No special device configuration is required for exploitation.
The vulnerability affects the following Palo Alto Networks products:
- PA-Series firewalls
- VM-Series firewalls
- Panorama virtual appliances
- Panorama M-Series appliances
Cloud NGFW and Prisma Access are not affected.
The affected PAN-OS versions include multiple releases across the 10.2, 11.1, 11.2, 12.1, and 12.2 branches. A fix for PAN-OS 11.2.16 is expected on October 15, 2026. Customers running end-of-life versions must upgrade to a supported release.
Customers with a Threat Prevention subscription can enable Threat IDs 510046 and 510047 for limited coverage. However, these signatures require SSL decryption and may not detect all attack variations.
Business and Operational Impact
Firewalls are a critical security control. A compromise at the root level can undermine an entire network perimeter. The potential consequences include:
- Complete firewall takeover — Attackers gain root access and can modify rules, exfiltrate logs, or pivot into internal networks
- Network visibility loss — Compromised firewalls may stop logging or inject false negatives
- Lateral movement facilitation — Root access on a perimeter device is an ideal staging point
- Regulatory exposure — Federal agencies face a CISA-mandated three-day patching window
- Operational disruption — Emergency patching on production firewalls can cause outages
Because exploitation requires valid credentials, organizations with weak or leaked management passwords face the highest immediate risk.
Mitigation and Recommendations
Palo Alto Networks has published patches for most affected versions. There are no known workarounds.
Immediate Actions for Defenders
- Patch immediately — Upgrade to a fixed PAN-OS version. A patch for 11.2.16 is expected today
- Restrict management access — Limit the management interface to trusted internal IP addresses only
- Rotate credentials — Change PAN-OS admin passwords if there is any suspicion of compromise
- Enable Threat Prevention signatures — Turn on Threat IDs 510046 and 510047 if you have a subscription and SSL decryption
- Audit access logs — Review management interface logs for sessions from the known attacker IPs
Detection Guidance
Security teams should monitor for:
- Unusual login activity on the PAN-OS management interface
- Connections to the three disclosed attacker IP addresses
- Unexpected configuration changes on firewalls or Panorama
- Anomalous SSL sessions to the management interface
Bottom line: CVE-2026-0322 is a root-level RCE on a core perimeter device. Patch now, restrict management access, and audit your logs. Do not wait for the CISA deadline.
Incident Summary
| CVE ID / Incident: | CVE-2026-0322 |
| Affected Systems: | Palo Alto Networks PA-Series, VM-Series, Panorama (virtual and M-Series); PAN-OS 10.2, 11.1, 11.2, 12.1, 12.2 |
| Severity: | High (CVSS 8.6) |
| Disclosure Date: | October 14, 2026 |
| Patch Status: | Available for most versions; PAN-OS 11.2.16 patch expected October 15, 2026 |
| CISA KEV Deadline: | October 17, 2026 (federal agencies) |
| Known Attacker IPs: | 66.42.72[.]14, 208.83.239[.]114, 149.248.47[.]234 |
References
- Palo Alto Networks, “CVE-2026-0322 PAN-OS: Authenticated Remote Code Execution (RCE) in the Management Interface,” October 14, 2026, https://security.paloaltonetworks.com/CVE-2026-0322, accessed October 15, 2026
- BleepingComputer, “Palo Alto Networks warns of PAN-OS RCE flaw exploited in attacks,” October 14, 2026, https://www.bleepingcomputer.com/news/security/palo-alto-networks-warns-of-pan-os-rce-flaw-exploited-in-attacks/, accessed October 15, 2026
- CISA, “CISA Adds Four Known Exploited Vulnerabilities to Catalog,” October 14, 2026, https://www.cisa.gov/news-events/alerts/2026/10/14/cisa-adds-four-known-exploited-vulnerabilities-catalog, accessed October 15, 2026