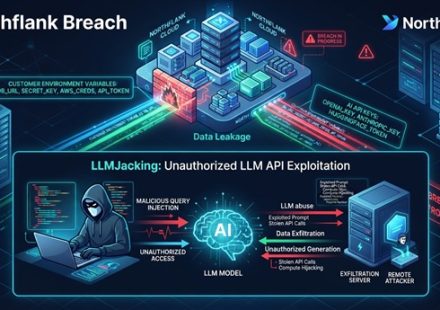
Northflank Breach Exposes AI API Keys in Black October Campaign

October 31, 2026 On October 30, 2026, cloud application hosting platform Northflank disclosed a security breach that exposed decrypted customer environment variables. Attackers abused stolen AI API keys across multiple accounts in what security…
Hackers Scan for Critical Oracle EBS RCE Flaw Days After Patch
October 29, 2026 Threat actors have started scanning for a newly patched critical vulnerability in Oracle E-Business Suite (EBS) within days of its disclosure. Tracked as CVE-2026-101767, this unauthenticated SQL injection flaw carries a CVSS score of…
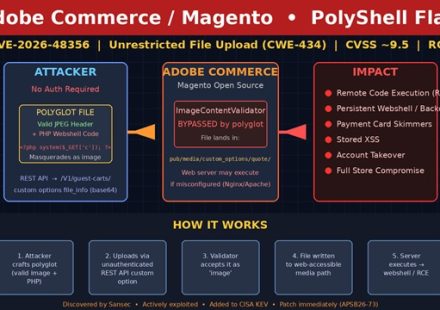
CISA Adds Adobe Commerce PolyShell Flaw to KEV
October 28, 2026 The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a critical Adobe Commerce and Magento vulnerability to its Known Exploited Vulnerabilities (KEV) catalog on October 27, 2026. Tracked as CVE-2026-48356 and dubbed…
CISA Adds Brotli2Shell to KEV Catalog Enables RCE Across Node.js, .NET, and Python
October 28, 2026 CISA has added CVE-2026-111497 to its Known Exploited Vulnerabilities catalog after confirmed in-the-wild exploitation. The flaw, also known as Brotli2Shell, Node2Shell, and HTTP2Shell, is an out-of-bounds write in Google’s Brotli…
CISA Confirms PHP2Shell RCE Exploitation Added to KEV Catalog
October 27, 2026 CISA confirmed active exploitation of two critical PHP vulnerabilities collectively tracked as PHP2Shell. Threat actors can exploit CVE-2026-109618 and CVE-2026-109619 to gain unauthenticated remote code execution on millions of…
k0t Threat Actor Breaches Enterprise Firewalls and VPNs
October 25, 2026 Cybersecurity researchers from Group-IB and NyxLab have uncovered a massive campaign that has breached enterprise firewalls and VPNs worldwide. Consequently, the threat actor known as k0t has exposed over 70,000 credentials and…
Arista VeloCloud Orchestrator SQL Injection Zero-Day Grants Operator Privileges
October 22, 2026 Arista Networks disclosed a critical zero-day vulnerability in VeloCloud Orchestrator on October 22, 2026. CVE-2026-114625 lets any authenticated user escalate to operator privileges through SQL injection. Attackers are actively…
GitLab Critical RCE Allows Unauthenticated Code Execution Across 12 Years of Releases
October 22, 2026 GitLab has released emergency security updates for a critical unauthenticated remote code execution vulnerability that affects every self-managed version of the platform released since 2014. The flaw, tracked as CVE-2026-110264, carries…
eMudhra CA Private Keys Compromised
October 20, 2026 The private keys of eight eMudhra intermediate certificate authority certificates have been compromised. Mozilla and Google confirmed the breach on October 20, 2026, after a researcher reported it on the evening of October 17. The…
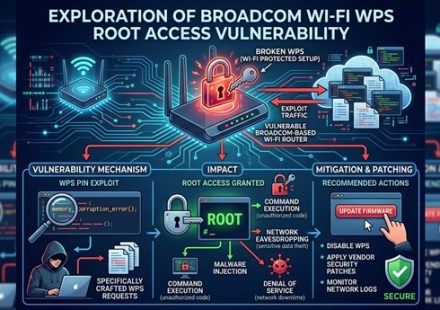
Broadcom Wi-Fi WPS Vulnerability Grants Root Access to Nearby Attackers
October 20, 2026 A newly disclosed vulnerability in Broadcom’s Wi-Fi software lets attackers within wireless range take complete control of vulnerable routers without knowing the Wi-Fi password. Security researcher Quentin Kaiser revealed the flaw…