
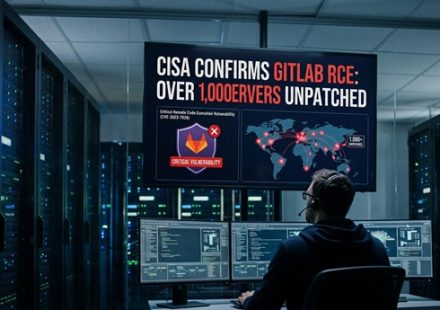
CISA Confirms GitLab CI/CD RCE Exploitation

November 2, 2026 CISA has confirmed active exploitation of a maximum-severity remote code execution (RCE) flaw in GitLab. Over 1,000 self-managed GitLab servers remain unpatched and exposed to ongoing attacks, despite patches being available for three…
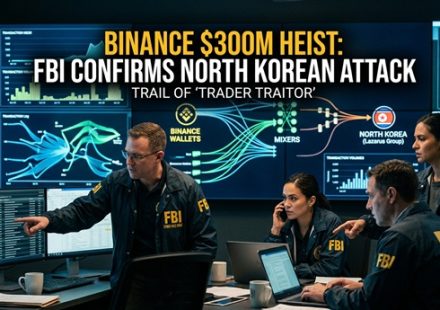
FBI Confirms North Korean TraderTraitor Group Behind Largest Crypto Theft in History
November 2, 2026 The FBI has officially attributed a record-breaking $6.3 billion cryptocurrency heist at Binance to North Korean state-sponsored hackers. The attack, which unfolded on October 29, 2026, stands as the largest crypto theft in history.…
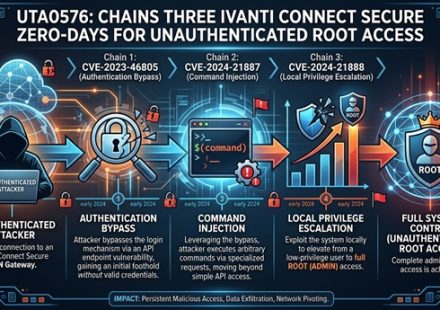
UTA0576 Chains Three Ivanti Connect Secure Zero-Days for Unauthenticated Root Access
November 1, 2026 CISA has added two actively exploited Ivanti Connect Secure flaws to its Known Exploited Vulnerabilities catalog, intensifying pressure on federal agencies to patch before November 2. Threat actor UTA0576 chained three zero-day…
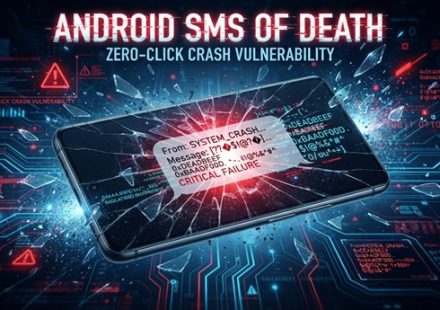
Android SMS of Death Zero-Click Text Message Crash Threatens Phones
November 1, 2026 A zero-click Android vulnerability, dubbed the SMS of Death, lets attackers crash phones by sending a single malformed text message. The flaw, tracked as CVE-2026-58882, disrupts cellular service and can even interrupt emergency calls…
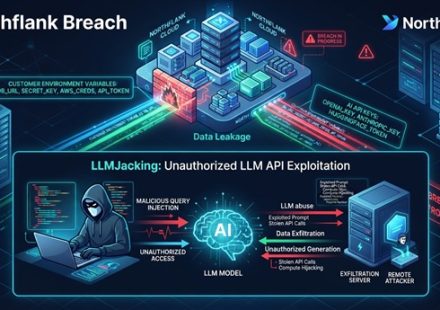
Northflank Breach Exposes AI API Keys in Black October Campaign
October 31, 2026 On October 30, 2026, cloud application hosting platform Northflank disclosed a security breach that exposed decrypted customer environment variables. Attackers abused stolen AI API keys across multiple accounts in what security…
Claude Code Extension Plants SSH Backdoors
October 30, 2026 A trojanized version of Anthropic’s official Claude Code VS Code extension was distributed through Cursor’s extension marketplace for approximately 11 hours on October 29, 2026. Furthermore, the malicious update exposed up to…
Cisco ASA and FTD SSL VPN Zero-Day Lets Attackers Crash Firewalls Remotely
October 30, 2026 Cisco has released urgent patches for a high-severity zero-day vulnerability in its Secure Firewall Adaptive Security Appliance (ASA) and Threat Defense (FTD) software. The flaw, tracked as CVE-2026-76418, allows unauthenticated remote…
CISA Adds VMware ESX Logging Zero-Day to KEV After Warp Panda Exploits
October 29, 2026 The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added a Broadcom VMware ESX logging flaw to its Known Exploited Vulnerabilities (KEV) Catalog. The vulnerability, tracked as CVE-2026-41709, was exploited as a zero-day…
Hackers Scan for Critical Oracle EBS RCE Flaw Days After Patch
October 29, 2026 Threat actors have started scanning for a newly patched critical vulnerability in Oracle E-Business Suite (EBS) within days of its disclosure. Tracked as CVE-2026-101767, this unauthenticated SQL injection flaw carries a CVSS score of…
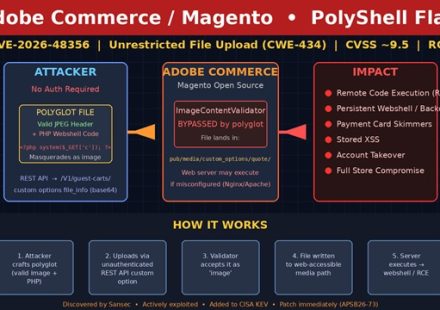
CISA Adds Adobe Commerce PolyShell Flaw to KEV
October 28, 2026 The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a critical Adobe Commerce and Magento vulnerability to its Known Exploited Vulnerabilities (KEV) catalog on October 27, 2026. Tracked as CVE-2026-48356 and dubbed…