UK fashion retailer ASOS confirmed a data breach after attackers hijacked the company’s mobile app to send threatening push notifications directly to millions of customers. The incident, which occurred on October 6, 2026, raises fresh concerns about third-party platform security and the growing tactic of using official brand channels for extortion campaigns.
What Happened: ASOS Hackers Hijack App Notifications for Extortion
At approximately 10:00 AM UK time on October 6, 2026, ASOS app users worldwide received an unauthorized push notification headlined “ASOS HACKED.” The message claimed attackers had “fully compromised the Snowflake instance” and demanded engagement under threat of a data leak.
The notification included a link to a Telegram channel operated by a previously unknown threat actor calling itself the Xuanye Group. Moreover, the message reached many, if not all, of ASOS’s mobile app users, making it one of the most visible breach disclosures in recent memory. Consequently, ASOS shares dropped approximately 10 percent after the incident became public.
ASOS later confirmed unauthorized access to third-party platforms used for customer communications. The company stated that basic personal information, including names and contact details, may have been accessed. However, ASOS said it does not believe payment-card information or account passwords were impacted. The retailer’s website and app remained online throughout the incident, with no reported disruption to orders or operations.
Technical Details of the ASOS Attack
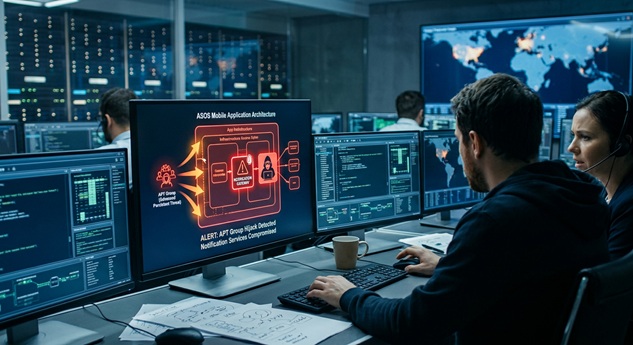
The attack appears to have targeted third-party communication platforms rather than ASOS’s core infrastructure directly. This approach highlights a growing threat vector: compromising the services that connect brands to their customers.
The attackers gained sufficient access to push notification systems to send messages through ASOS’s official mobile app. This is significant because users inherently trust notifications that appear to come from legitimate applications they installed. Furthermore, the inclusion of a Telegram channel link suggests the attackers wanted to control the narrative and establish a direct communication channel.
Key technical observations include:
- The Xuanye Group used a gateway Telegram channel that redirected visitors to a separate broadcast channel, a structure designed to maintain persistence if one channel is removed
- Snowflake investigated the claims and found no evidence that its platform itself was compromised, pointing to a potential customer-environment issue
- The attackers did not publish samples of stolen data, making the scope of the breach difficult to verify independently
Business and Operational Impact
The ASOS breach carries significant implications beyond the immediate data exposure. Therefore, organizations relying on third-party communication platforms should review their security posture.
- Stock Price Impact: ASOS shares fell roughly 10 percent following disclosure, after dropping more than 14 percent during trading
- Customer Trust: The breach weaponized ASOS’s own app against its user base, turning a trusted communication channel into an extortion tool
- Regulatory Exposure: The UK’s National Cyber Security Centre is assisting ASOS, indicating potential regulatory scrutiny under UK GDPR
- Supply Chain Risk: The incident underscores how third-party platforms can become single points of failure for customer communication security
In addition, the attackers’ ability to reach the entire app user base raises questions about access controls and monitoring within ASOS’s notification infrastructure.
Mitigation and Recommendations
Organizations using third-party communication platforms should treat this incident as a wake-up call. The following steps can reduce similar exposure.
Immediate Actions for Defenders
- Audit access controls on all third-party communication and marketing platforms
- Enable multifactor authentication for every account with push-notification or customer-messaging privileges
- Review API keys and service accounts for excessive permissions
- Implement monitoring for unusual notification volumes or unauthorized message content
- Establish an incident-response playbook for compromised customer-communication channels
Detection Guidance
Security teams should monitor for these indicators:
- Unusual API activity from third-party messaging platforms outside normal business hours
- Unexpected changes to notification templates or content
- Login attempts from unfamiliar IP addresses or geographies on communication-platform accounts
- Customer reports of suspicious messages appearing to come from official apps
Customer Protection Advice
ASOS customers and users of similar platforms should take the following precautions:
- Ignore the unauthorized Telegram link and any follow-up messages referencing it
- Be cautious of phishing emails or texts that use names and contact details to appear convincing
- Monitor bank and credit-card statements for unusual activity
- Obtain updates only through the official ASOS website or app
Bottom line: This breach demonstrates how third-party communication platforms have become high-value targets. Organizations must secure these channels with the same rigor applied to their core infrastructure.
Incident Summary
| Incident: | ASOS Data Breach via Hijacked Push Notifications |
| Threat Actor: | Xuanye Group |
| Disclosure Date: | October 6, 2026 |
| Affected Data: | Names and contact details possibly accessed; payment and password data not believed impacted |
| Claimed Target: | Snowflake instance (unverified) |
| Response: | UK NCSC assisting; ASOS restricted access to affected platforms |
References
- BleepingComputer, “ASOS confirms data breach after ‘HACKED’ in-app notifications,” October 6, 2026, https://www.bleepingcomputer.com/news/security/asos-confirms-data-breach-after-hacked-in-app-notifications/
- Hackread.com, “ASOS Hackers Hijack App Notifications, Claim Snowflake Data Breach,” October 6, 2026, https://hackread.com/asos-hackers-hijack-app-notifications-snowflake-data-breach/
- Reuters, “UK online retailer ASOS shares drop on hack reports,” October 6, 2026, https://www.reuters.com/business/retail-consumer/uk-online-retailer-asos-shares-drop-hack-reports-2026-10-06/
- The Guardian, “Asos customers receive ‘hack’ notification threatening leak,” October 6, 2026, https://www.theguardian.com/business/2026/oct/06/asos-hack-notification-website-app