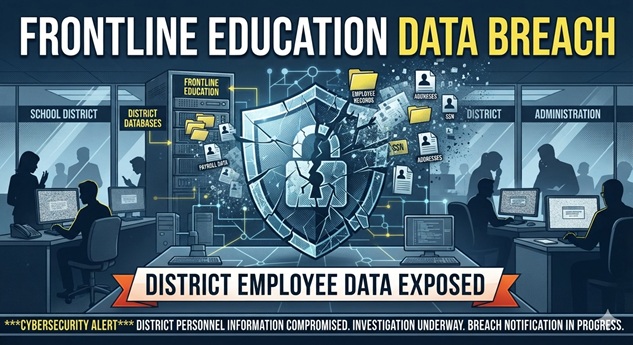
Frontline Education, a major edtech provider serving thousands of U.S. school districts, has disclosed a data breach after attackers exploited a vulnerability in third-party software to steal employee information. Consequently, the incident has exposed Social Security numbers, email addresses, and physical addresses of school district employees across the country.
What Happened: Frontline Education Data Breach Hits School District Employees
On August 14, 2026, Frontline Education’s security team identified a vulnerability in a third-party software product that allowed unauthorized access to a portion of its environment. Attackers leveraged this flaw to gain entry and steal employee data from multiple school districts. Frontline has not publicly named the third-party application involved or disclosed when the initial unauthorized access first occurred.
The company investigated the incident with the help of an independent cybersecurity firm. Furthermore, it remediated the vulnerability, engaged with law enforcement, and took steps to reinforce its security posture. However, the stolen data included personally identifiable information that poses significant identity theft risks for affected employees.
Impacted individuals have begun receiving breach notification letters. One district reported that 1,210 employees were affected. The exposed information included:
- Social Security numbers
- Email addresses
- Physical addresses
It remains unclear how many school districts or total individuals were affected overall. Frontline Education has stated that it will handle notifications to affected individuals on behalf of impacted school districts unless a district opts out by October 16, 2026.
Technical Details of the Frontline Education Breach
The attack vector centered on a vulnerability in a third-party application integrated into Frontline’s environment. This type of supply-chain or third-party exposure is increasingly common in the education sector. Attackers often target software vendors that serve multiple organizations because a single breach can yield access to data across many downstream customers.
Frontline Education provides administration and workforce management software used by school districts nationwide. Its platform handles sensitive employee data including payroll, benefits, and human resources information. Therefore, a compromise of this platform carries significant downstream consequences.
Key technical observations from the disclosure include:
- The vulnerability was in a third-party software product, not Frontline’s core platform.
- Attackers exploited the flaw to gain unauthorized access to a “portion of the environment.”
- The breach was discovered on August 14, but the actual intrusion may have occurred earlier.
- Frontline engaged an independent cybersecurity firm to investigate and remediate.
The company has not disclosed whether the attack involved ransomware, data encryption, or additional payloads beyond data exfiltration.
Business and Operational Impact
The Frontline Education breach carries serious implications for both the company and the school districts it serves.
- Identity theft risk: Exposed Social Security numbers enable fraudsters to open credit accounts, file fraudulent tax returns, and commit synthetic identity fraud.
- Workforce disruption: School districts must now manage breach notifications, credit monitoring enrollment, and employee concerns during an already strained academic year.
- Regulatory exposure: State attorneys general must be notified. Frontline has committed to covering these notification costs and providing credit monitoring services.
- Reputational damage: School districts rely on Frontline for sensitive HR and payroll functions. Trust erosion may prompt districts to evaluate alternative vendors.
- Supply-chain precedent: This incident adds to a growing list of education-sector breaches rooted in third-party software vulnerabilities.
Frontline is offering affected adults two years of free credit monitoring and identity theft protection through TransUnion. Minors will receive cyber monitoring services instead.
Mitigation and Recommendations
Immediate Actions for Affected Individuals
- Enroll in the free credit monitoring and identity theft protection offered through TransUnion.
- Place a fraud alert or credit freeze on your credit reports with all three major bureaus.
- Monitor bank accounts, credit card statements, and tax records for unusual activity.
- Be alert for phishing emails, texts, or calls that reference the breach or appear to come from Frontline.
- File your taxes early to reduce the risk of fraudulent tax return filing.
Actions for School District IT and Security Teams
- Review all third-party integrations and software vendors for known vulnerabilities.
- Require security questionnaires and breach notification clauses in vendor contracts.
- Implement network segmentation to limit the blast radius of third-party compromises.
- Enable multi-factor authentication on all administrative and HR platforms.
- Conduct regular vulnerability assessments of edtech and SaaS providers.
- Establish an incident response plan specific to third-party data breaches.
Actions for EdTech Vendors
- Conduct annual security audits and penetration tests of third-party integrations.
- Maintain an accurate software bill of materials (SBOM) for all dependencies.
- Implement continuous vulnerability monitoring for third-party components.
- Establish clear breach notification timelines in customer agreements.
- Encrypt sensitive data at rest and in transit, with key management separated from application layers.
Bottom line: Third-party software vulnerabilities remain one of the most efficient attack paths for data thieves. School districts and edtech vendors must treat supply-chain security as a core competency, not an afterthought.
Incident Summary
| Incident: | Frontline Education data breach via third-party software vulnerability |
| Affected Systems: | Frontline Education environment (third-party application) |
| Disclosure Date: | October 2, 2026 |
| Discovery Date: | August 14, 2026 |
| Data Exposed: | Social Security numbers, email addresses, physical addresses |
| Attack Vector: | Vulnerability in third-party software product |
| Impact: | School district employees across multiple U.S. districts |
| Patch Status: | Vulnerability remediated; investigation ongoing |
References
- BleepingComputer, “Frontline Education breach exposes school district employee data,” October 2, 2026, https://www.bleepingcomputer.com/news/security/frontline-education-data-breach-impacts-school-district-employees/, accessed October 4, 2026.
- Reddit r/k12sysadmin, “Frontline breach” discussion thread, October 2026, https://www.reddit.com/r/k12sysadmin/comments/1wvtkev/frontline_breach/, accessed October 4, 2026.