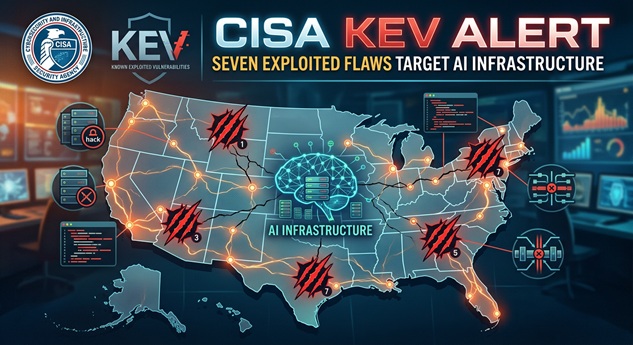
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added seven critical vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog. Threat actors are actively exploiting these flaws to deploy reverse shells, cryptocurrency miners, and unauthorized administrative access across enterprise networks and artificial intelligence infrastructure.
The additions span SonicWall SMA appliances, Sangoma Switchvox phone systems, JFrog Artifactory repositories, Starlette web frameworks, Kestra workflow engines, and LiteLLM AI gateways. Consequently, organizations running any of these technologies face immediate risk and should prioritize patching.
What Happened: CISA KEV Alert Adds Seven Actively Exploited Flaws
On September 2, 2026, CISA published a KEV catalog update confirming active exploitation of seven distinct vulnerabilities. Moreover, the agency set binding patch deadlines under Binding Operational Directive (BOD) 26-04 for Federal Civilian Executive Branch (FCEB) agencies.
The vulnerabilities range from CVSS 6.5 to 10.0, with multiple flaws scoring near maximum severity. Therefore, defenders cannot afford to treat any of them as theoretical risks.
Technical Details of the Seven Exploited Vulnerabilities
Each flaw offers attackers a different path into enterprise environments. Below is a breakdown of the vulnerabilities and their exploitation mechanics.
SonicWall SMA 1000 Appliances: SSRF and Command Injection
- CVE-2026-83548 (CVSS 10.0): A server-side request forgery vulnerability allows remote unauthenticated attackers to access sensitive functionality without credentials.
- CVE-2026-83549 (CVSS 7.8): A post-authentication operating system command injection flaw enables authenticated administrators to execute arbitrary OS commands remotely.
SonicWall confirmed active exploitation of both flaws, making immediate firmware updates essential for affected organizations.
Sangoma Switchvox: SQL Injection to Remote Code Execution
- CVE-2026-9586 (CVSS 9.3): An unauthenticated SQL injection vulnerability allows attackers to execute arbitrary SQL statements against the backend PostgreSQL database using a single crafted request. Furthermore, successful exploitation can lead to remote code execution.
JFrog Artifactory: Authentication Bypass to Admin
- CVE-2026-82329 (CVSS 9.8): An improper authentication flaw under default configuration allows unauthenticated attackers with network access to obtain administrative privileges.
Threat actors have weaponized this vulnerability to mint admin tokens and enumerate users, groups, and federated access topologies.
Kludex Starlette: HTTP Request Smuggling
- CVE-2026-48710 (CVSS 6.5): An HTTP request and response smuggling vulnerability allows attackers to inject paths into the host part, prepending the actual path. Moreover, this can enable authentication bypass when authentication depends on the reconstructed URL’s path.
Kestra OSS: Unauthenticated Command Injection
- CVE-2026-49869 (CVSS 10.0): An operating system command injection flaw allows unauthenticated remote attackers to create and execute arbitrary workflows without credentials. Microsoft reported that threat actors exploited this in late June 2026 to establish a reverse shell, perform Docker container discovery, deploy a cryptocurrency miner, and harvest data.
Berri LiteLLM: Improper Authentication on MCP Endpoint
- CVE-2026-59822 (CVSS 8.8): An improper authentication vulnerability in LiteLLM’s Model Context Protocol (MCP) Streamable HTTP endpoint allows unauthenticated attackers to establish an authenticated MCP session using an arbitrary Bearer token.
Business and Operational Impact
The exploitation of these seven flaws carries severe consequences for affected organizations.
- Unauthorized administrative access: Attackers can escalate from unauthenticated to admin-level privileges on critical systems.
- Reverse shell deployment: CVE-2026-49869 enables attackers to establish persistent command-and-control channels.
- Cryptocurrency mining: Threat actors are monetizing compromised infrastructure by deploying XMRig miners.
- AI infrastructure targeting: LiteLLM and Kestra flaws expose AI gateways, enabling theft of API keys, model configurations, and provider credentials.
- Data harvesting: Attackers abuse workflow engines and database interfaces to exfiltrate collected output.
- Container environment compromise: Docker socket access allows attackers to escape containers and access host resources.
Microsoft and Wiz researchers confirmed that AI infrastructure, including LiteLLM, Flowise, LangChain, Langflow, ChromaDB, Ollama, Marimo, and MCP servers, has become a lucrative target. Attackers steal API keys, gain backend access, maintain persistence, and monetize infected hosts.
Mitigation and Recommendations
Immediate Actions for Defenders
- Inventory all affected products across your environment, including SonicWall SMA, Sangoma Switchvox, JFrog Artifactory, Starlette, Kestra, and LiteLLM deployments.
- Apply vendor patches or hotfixes immediately. FCEB agencies must patch by September 5, 2026, for most flaws, and by September 16, 2026, for Starlette and LiteLLM.
- Isolate internet-facing appliances and AI gateways behind Web Application Firewalls (WAFs) or Zero Trust network segments.
- Rotate all credentials, API keys, and tokens for affected systems, especially LiteLLM virtual keys and OAuth secrets.
- Hunt for indicators of compromise, including unusual OAuth authentication failures, TMM SIGABRT events, and unauthorized workflow executions.
Monitoring and Detection Guidance
Security teams should monitor the following:
- Repeated OAuth authentication failures from single IP addresses
- Suspicious command execution on NetScaler or BIG-IP appliances
- Unauthorized workflow creation in Kestra instances
- Abnormal CPU usage indicating cryptomining activity
- Access to LiteLLM_ProxyModelTable and LiteLLM_VerificationToken database tables
Bottom line: These seven vulnerabilities represent a coordinated threat against both traditional enterprise infrastructure and emerging AI platforms. Patching alone is not enough — defenders must also hunt for signs of pre-patch compromise and harden AI gateway deployments.
Incident Summary
| CVE IDs / Incident: | CVE-2026-83548, CVE-2026-83549, CVE-2026-9586, CVE-2026-82329, CVE-2026-48710, CVE-2026-49869, CVE-2026-59822 |
| Affected Systems: | SonicWall SMA 1000, Sangoma Switchvox, JFrog Artifactory, Kludex Starlette, Kestra OSS, Berri LiteLLM |
| Disclosure Date: | September 2, 2026 (CISA KEV addition) |
| Patch Status: | Vendor patches and hotfixes available; FCEB deadline September 5–16, 2026 |
| Severity Range: | CVSS 6.5 to 10.0 |
| Threat Actors: | Unknown; Qilin ransomware operators linked to LiteLLM exploitation |
References
- CISA, “CISA Adds Seven Known Exploited Vulnerabilities to Catalog,” September 2, 2026, https://www.cisa.gov/news-events/alerts/2026/09/02/cisa-adds-seven-known-exploited-vulnerabilities-catalog, accessed September 28, 2026.
- The Hacker News, “CISA Adds Seven Exploited Flaws as Attackers Deploy Reverse Shells and Crypto Miners,” September 2026, https://thehackernews.com/2026/09/cisa-adds-seven-exploited-flaws-as.html, accessed September 28, 2026.
- Microsoft Security Blog, “When AI Infrastructure Becomes the Target: Securing Gateways and Control Points,” August 26, 2026, https://www.microsoft.com/en-us/security/blog/2026/08/26/when-ai-infrastructure-becomes-target-securing-gateways-control-points/, accessed September 28, 2026.
- SonicWall Security Advisory on SMA 1000 vulnerabilities, https://thehackernews.com/2026/09/attackers-exploit-two-sonicwall-sma.html, accessed September 28, 2026.
- Wiz Blog, “AI Infrastructure Honeypot,” https://www.wiz.io/blog/ai-infrastructure-honeypot, accessed September 28, 2026.