CISA Confirms Active Exploitation of Critical GitLab Path Traversal
CISA has added CVE-2026-85706 to its Known Exploited Vulnerabilities catalog after confirming active exploitation in the wild. This maximum-severity path traversal flaw affects GitLab Community Edition and Enterprise Edition. Unauthenticated attackers can exploit it to read arbitrary files, including credentials and secrets, from vulnerable servers with a single HTTP request.
What Happened: CISA Confirms Active Exploitation of Critical GitLab Path Traversal Flaw
On September 10, 2026, GitLab released patches for a critical path traversal vulnerability in its DevSecOps platform. The flaw, tracked as CVE-2026-85706, stems from missing authentication enforcement and improper path confinement in the repository commits API. Consequently, unauthenticated attackers can read sensitive files from vulnerable GitLab servers.
GitLab is a widely adopted DevSecOps platform used by over 50% of Fortune 100 companies and more than 30 million registered users worldwide. Therefore, this vulnerability poses a significant risk to enterprises that rely on GitLab for source code management, CI/CD pipelines, and DevOps workflows.
One day after GitLab released its patches, threat intelligence firm watchTowr reported observing in-the-wild exploitation probes. Attackers were scanning the internet for unpatched GitLab instances. Shortly after, on September 11, CISA added CVE-2026-85706 to its Known Exploited Vulnerabilities catalog under Binding Operational Directive 26-04. Federal agencies now have three days to patch or mitigate the flaw.
Technical Details of the GitLab Path Traversal Vulnerability
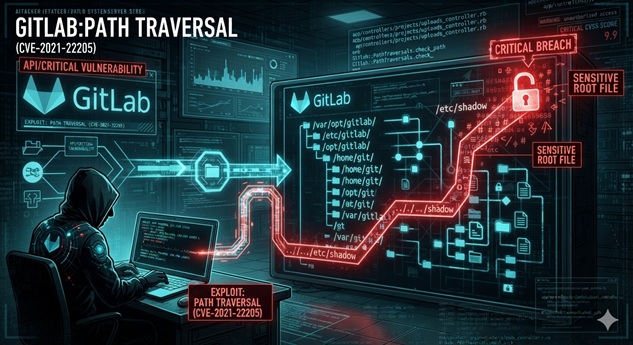
CVE-2026-85706 is a path traversal issue in the repository commits API. The vulnerability allows unauthenticated attackers to specify arbitrary file paths when creating commits through the API. Because the application fails to properly validate and confine the file path parameter, attackers can traverse the file system and read sensitive files.
The attack requires only a single HTTP POST request to the following endpoint:
/api/v4/projects/{id}/repository/commits/
Attackers supply a malicious file.path parameter within the request payload. This parameter can include directory traversal sequences such as ../ to access files outside the intended repository scope. As a result, attackers can extract credentials, API keys, configuration files, and other sensitive data stored on the GitLab server.
The following GitLab versions are affected:
- GitLab Community Edition and Enterprise Edition prior to 19.3.2
- GitLab Community Edition and Enterprise Edition prior to 19.2.6
- GitLab Community Edition and Enterprise Edition prior to 19.1
GitLab fixed the issue in versions 19.3.2, 19.2.6, and 19.1 on September 10, 2026. Users running older versions should upgrade immediately.
Business and Operational Impact
A successful exploitation of CVE-2026-85706 can have severe consequences for affected organizations. Because GitLab servers often store proprietary source code, API keys, database credentials, and CI/CD secrets, attackers who exploit this flaw can gain access to the software supply chain.
The potential impacts include:
- Credential theft: Attackers can extract database passwords, API keys, and service account credentials stored in configuration files or CI/CD variables.
- Source code exposure: Proprietary source code, intellectual property, and internal documentation may be accessed and exfiltrated.
- Supply chain compromise: Stolen CI/CD secrets could allow attackers to poison build pipelines, inject backdoors, or compromise downstream artifacts.
- Regulatory and compliance violations: Exposure of customer data or proprietary information may trigger breach notification requirements under GDPR, CCPA, and other frameworks.
- Reputational damage: Organizations that rely on GitLab for secure development may face loss of customer trust and competitive disadvantage.
Since GitLab is used by major enterprises and government agencies, this vulnerability represents a broad attack surface. CISA’s addition of CVE-2026-85706 to the KEV catalog signals that defenders should treat this as a high-priority threat.
Mitigation and Recommendations
Organizations running vulnerable GitLab instances should take immediate action to reduce their exposure. The following steps are recommended:
Immediate Actions for Defenders
- Apply patches immediately. Upgrade to GitLab CE or EE 19.3.2, 19.2.6, or 19.1 as soon as possible. GitLab released these patches on September 10, 2026.
- Restrict network access. Limit access to GitLab instances to trusted IP ranges or VPN connections. Remove public internet exposure where it is not required.
- Review logs for exploitation. Hunt through web server and GitLab logs for HTTP POST requests to
/api/v4/projects/{id}/repository/commits/containingfile.pathparameters with traversal sequences such as../. - Rotate exposed credentials. If exploitation is suspected, rotate all credentials, API keys, and secrets stored on or accessible from the GitLab server.
- Enable multi-factor authentication. Require MFA for all GitLab accounts to reduce the impact of credential theft.
Long-Term Hardening Measures
- Implement network segmentation to isolate GitLab servers from public-facing infrastructure.
- Use Web Application Firewalls (WAFs) to block path traversal patterns in API requests.
- Enable GitLab’s built-in security features, including container scanning, dependency scanning, and secret detection.
- Subscribe to GitLab security advisories and CISA alerts for timely notification of future vulnerabilities.
- Conduct regular vulnerability assessments on DevOps infrastructure.
Bottom line: CVE-2026-85706 is under active exploitation, and GitLab servers are a high-value target. Patch immediately, restrict network access, and hunt for signs of compromise in your logs.
Incident Summary
| CVE ID / Incident: | CVE-2026-85706 — GitLab CE/EE Path Traversal Vulnerability |
| Affected Systems: | GitLab Community Edition and Enterprise Edition prior to 19.3.2, 19.2.6, and 19.1 |
| Disclosure Date: | September 10, 2026 |
| CISA KEV Addition: | September 11, 2026 |
| Patch Status: | Available — upgrade to 19.3.2, 19.2.6, or 19.1 |
| Exploitation Status: | Active exploitation confirmed by CISA and watchTowr |
| Severity: | Critical (CVSS maximum severity) |
References
- Sergiu Gatlan, “CISA: Hackers now exploit max severity GitLab flaw in attacks,” BleepingComputer, September 14, 2026, https://www.bleepingcomputer.com/news/security/cisa-hackers-now-exploit-max-severity-gitlab-flaw-in-attacks/.
- U.S. Cybersecurity and Infrastructure Security Agency, “CISA Adds One Known Exploited Vulnerability to Catalog,” CISA Alert, September 11, 2026, https://www.cisa.gov/news-events/alerts/2026/09/11/cisa-adds-one-known-exploited-vulnerability-catalog.
- GitLab, “Patch Release GitLab 19.3.2 Released,” GitLab Releases, September 10, 2026, https://docs.gitlab.com/releases/patches/patch-release-gitlab-19-3-2-released/.
- watchTowr, “watchTowr Intel observations on CVE-2026-85706,” LinkedIn post, September 11, 2026, https://www.linkedin.com/posts/watchtowr-intel-is-already-observing-in-the-wild-share-7504127030326673408-E8qx/.
- U.S. Cybersecurity and Infrastructure Security Agency, “Binding Operational Directive 26-04: Prioritizing Security Updates Based on Risk,” CISA Directives, https://www.cisa.gov/news-events/directives/bod-26-04-implementation-guidance-prioritizing-security-updates-based-risk.